
Expert insights
Unlock a wealth of knowledge with our comprehensive resources library, featuring insightful guides, e-books, checklists and white papers
-
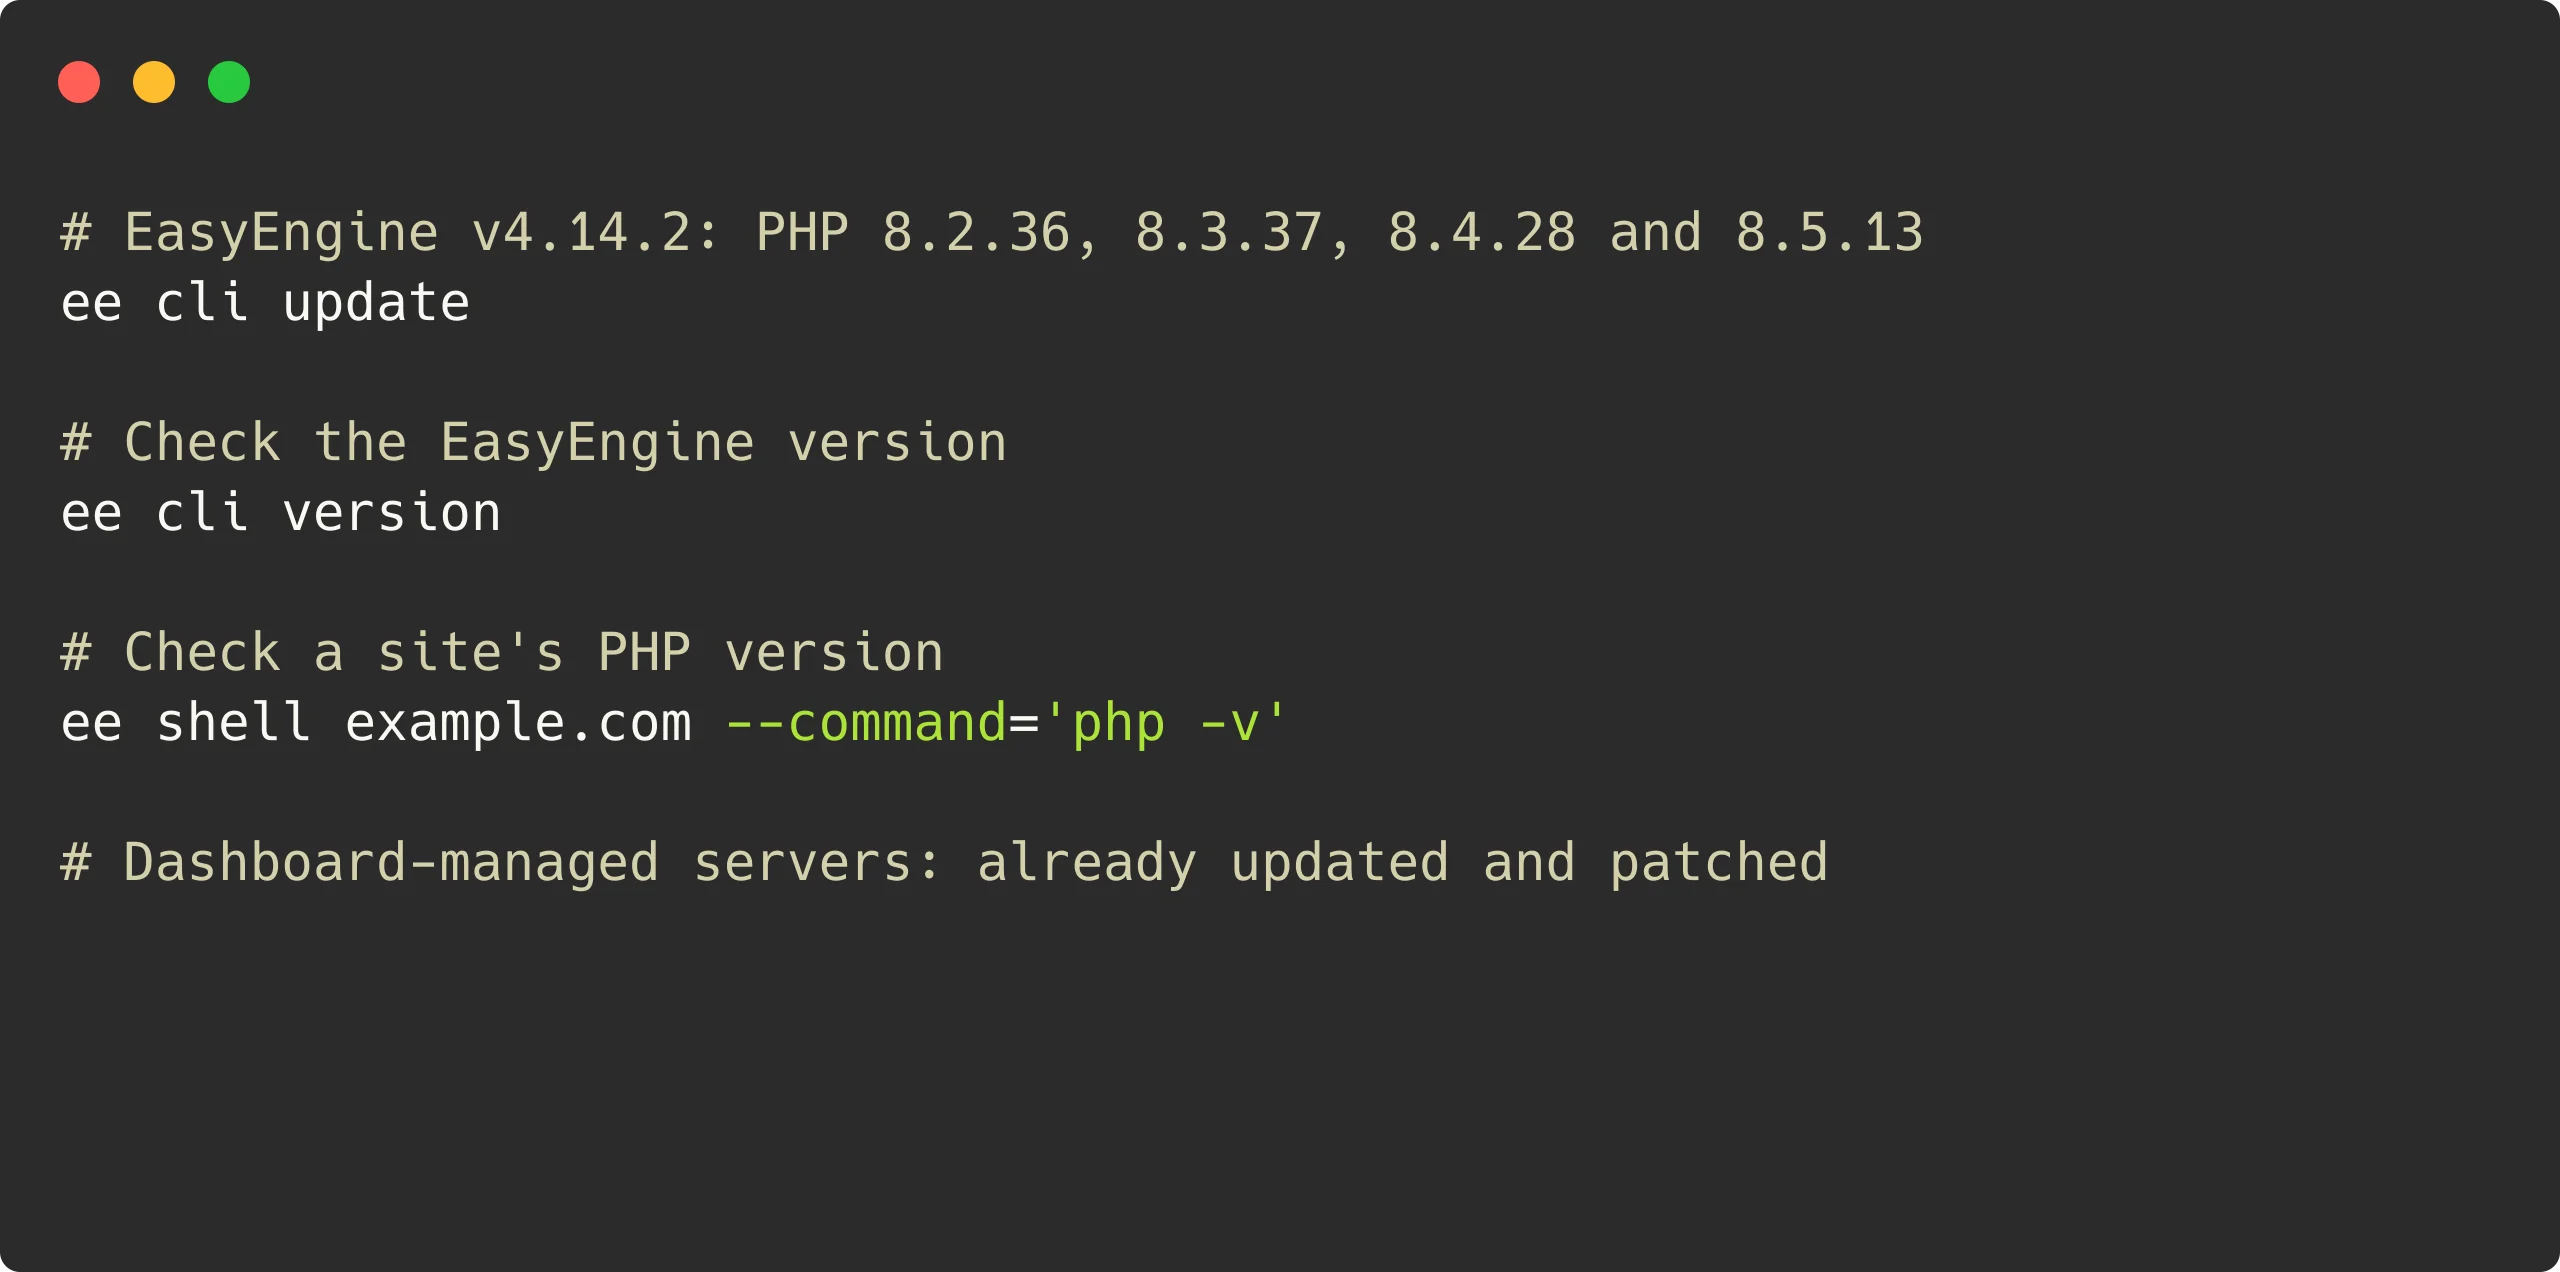
EasyEngine v4.14.2 Delivers November’s PHP Security Fixes
EasyEngine v4.14.2 delivers PHP’s security fixes for PHP 8.2 to 8.5, moving enabled sites to PHP 8.2.36, 8.3.37, 8.4.28 and 8.5.13. PHP released fixes for 17 security advisories, 7 of them rated critical. On CLI-managed servers, run ee cli update. Dashboard-managed servers are already updated and patched. There’s nothing for you to do unless you have sites on PHP 8.1 or older.
-
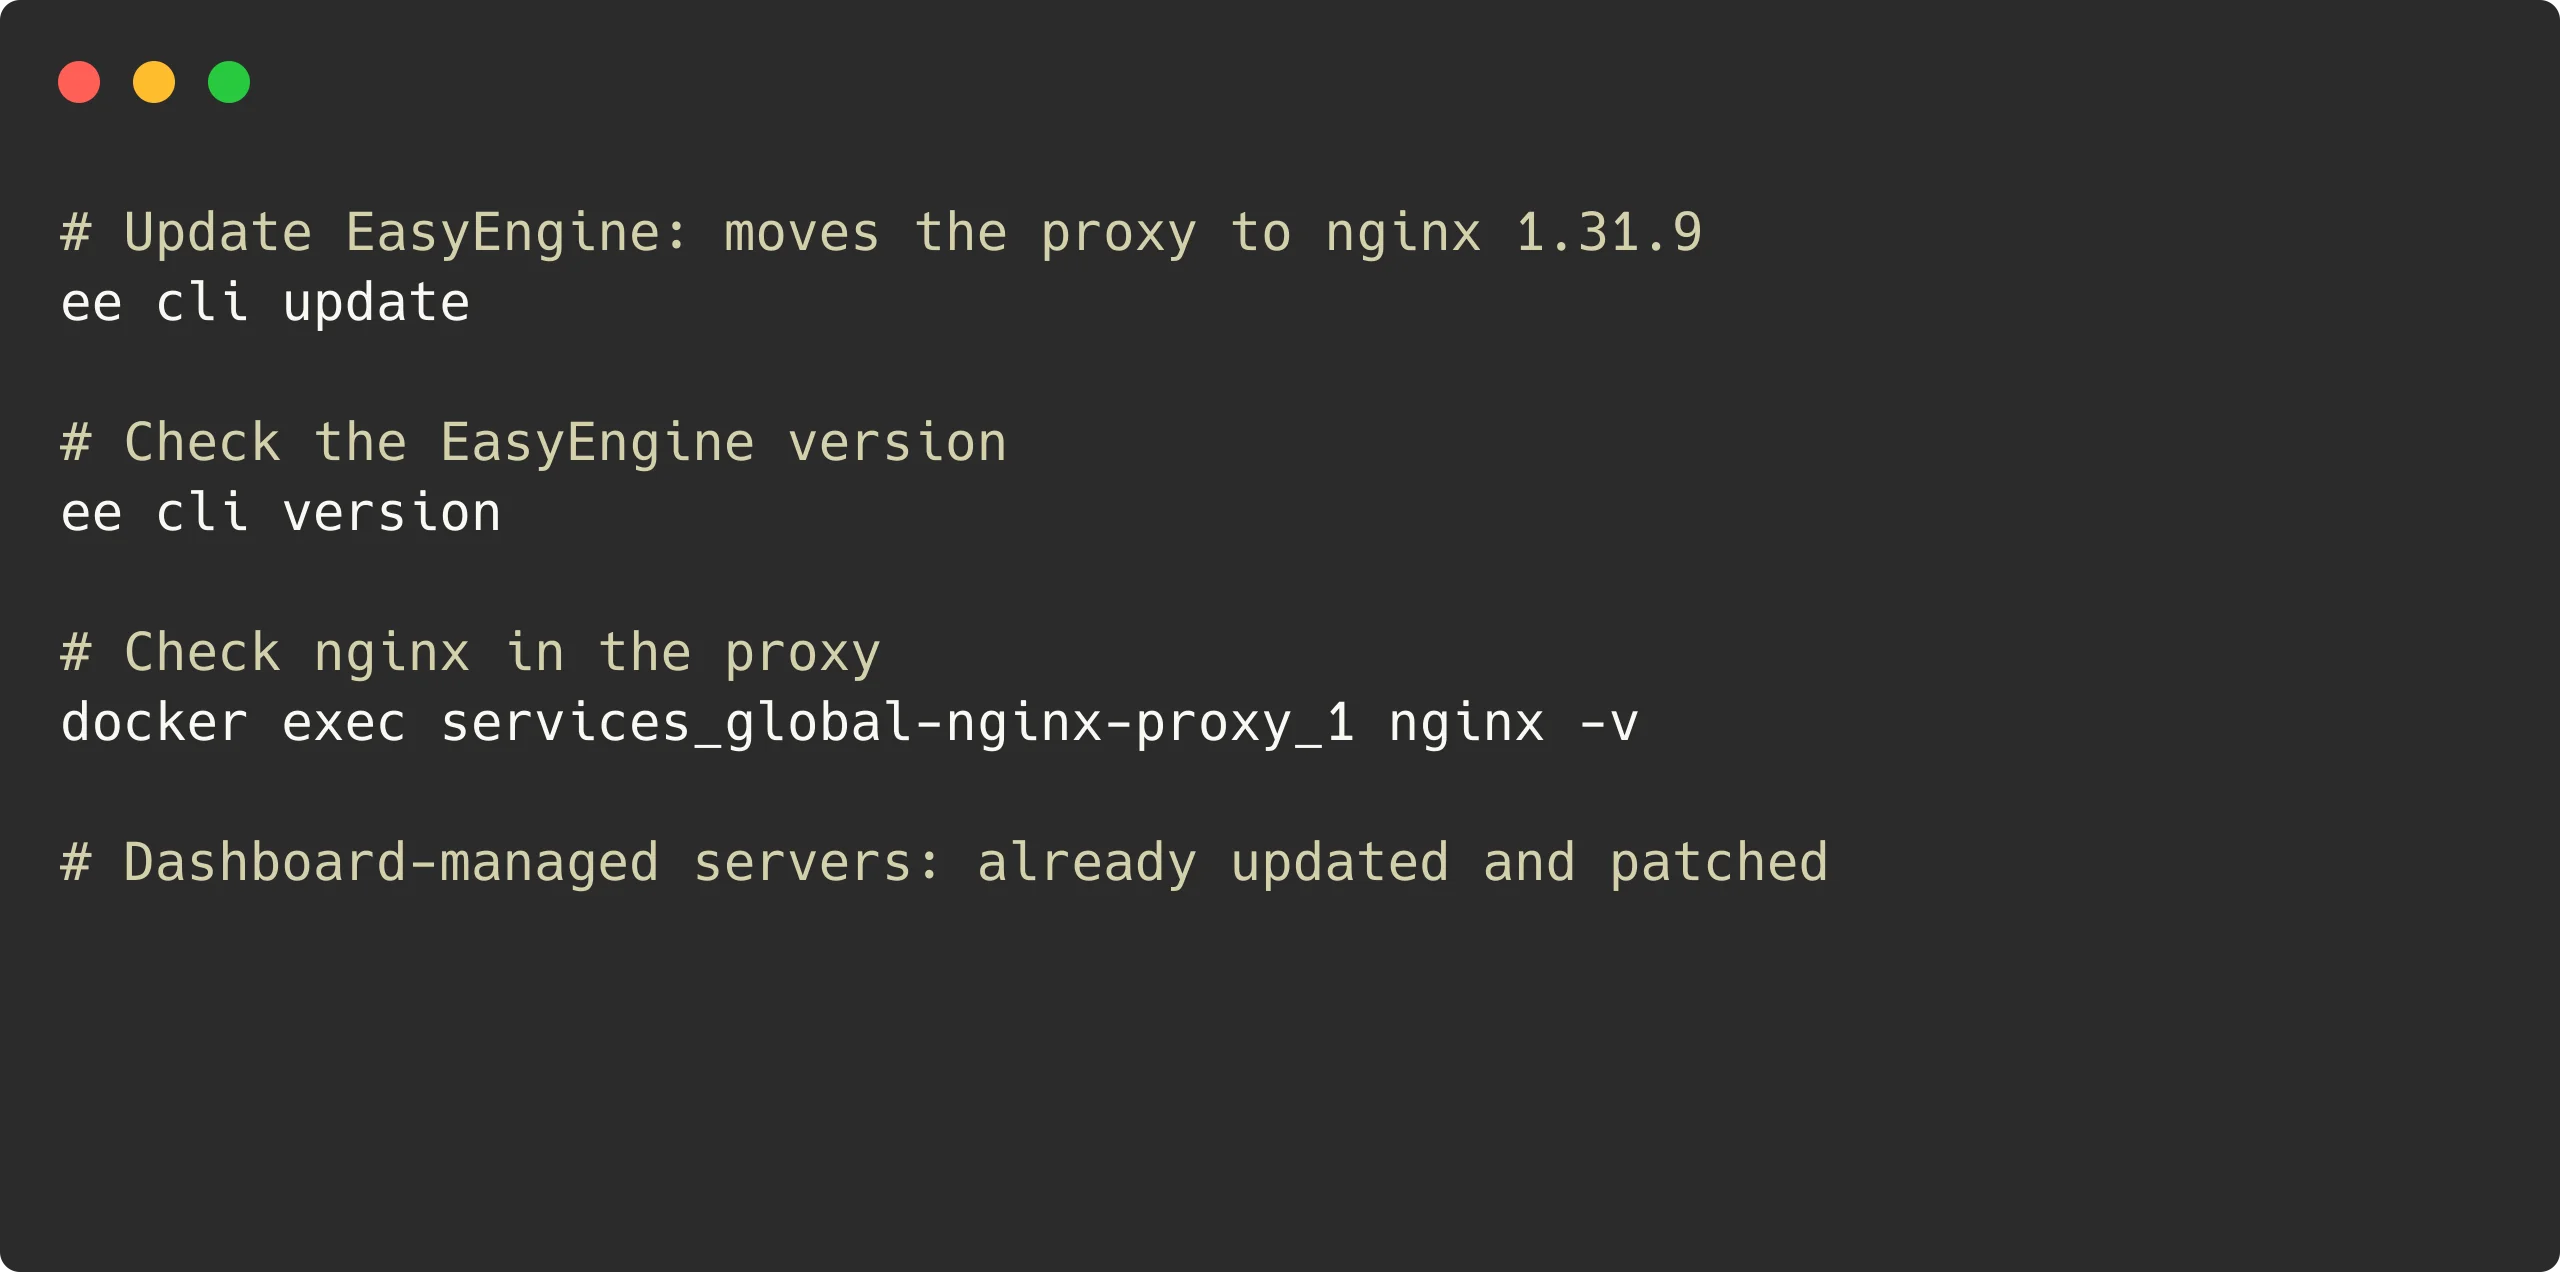
EasyEngine v4.14.1 Fixes nginx HTTP/2 Vulnerabilities
EasyEngine v4.14.1 fixes two HTTP/2 vulnerabilities in nginx, in the proxy that all traffic to your sites passes through. Servers on EasyEngine v4.14.0 or earlier are affected. On CLI-managed servers, run ee cli update. Dashboard-managed servers are already updated and patched, so there’s nothing for you to do.
-
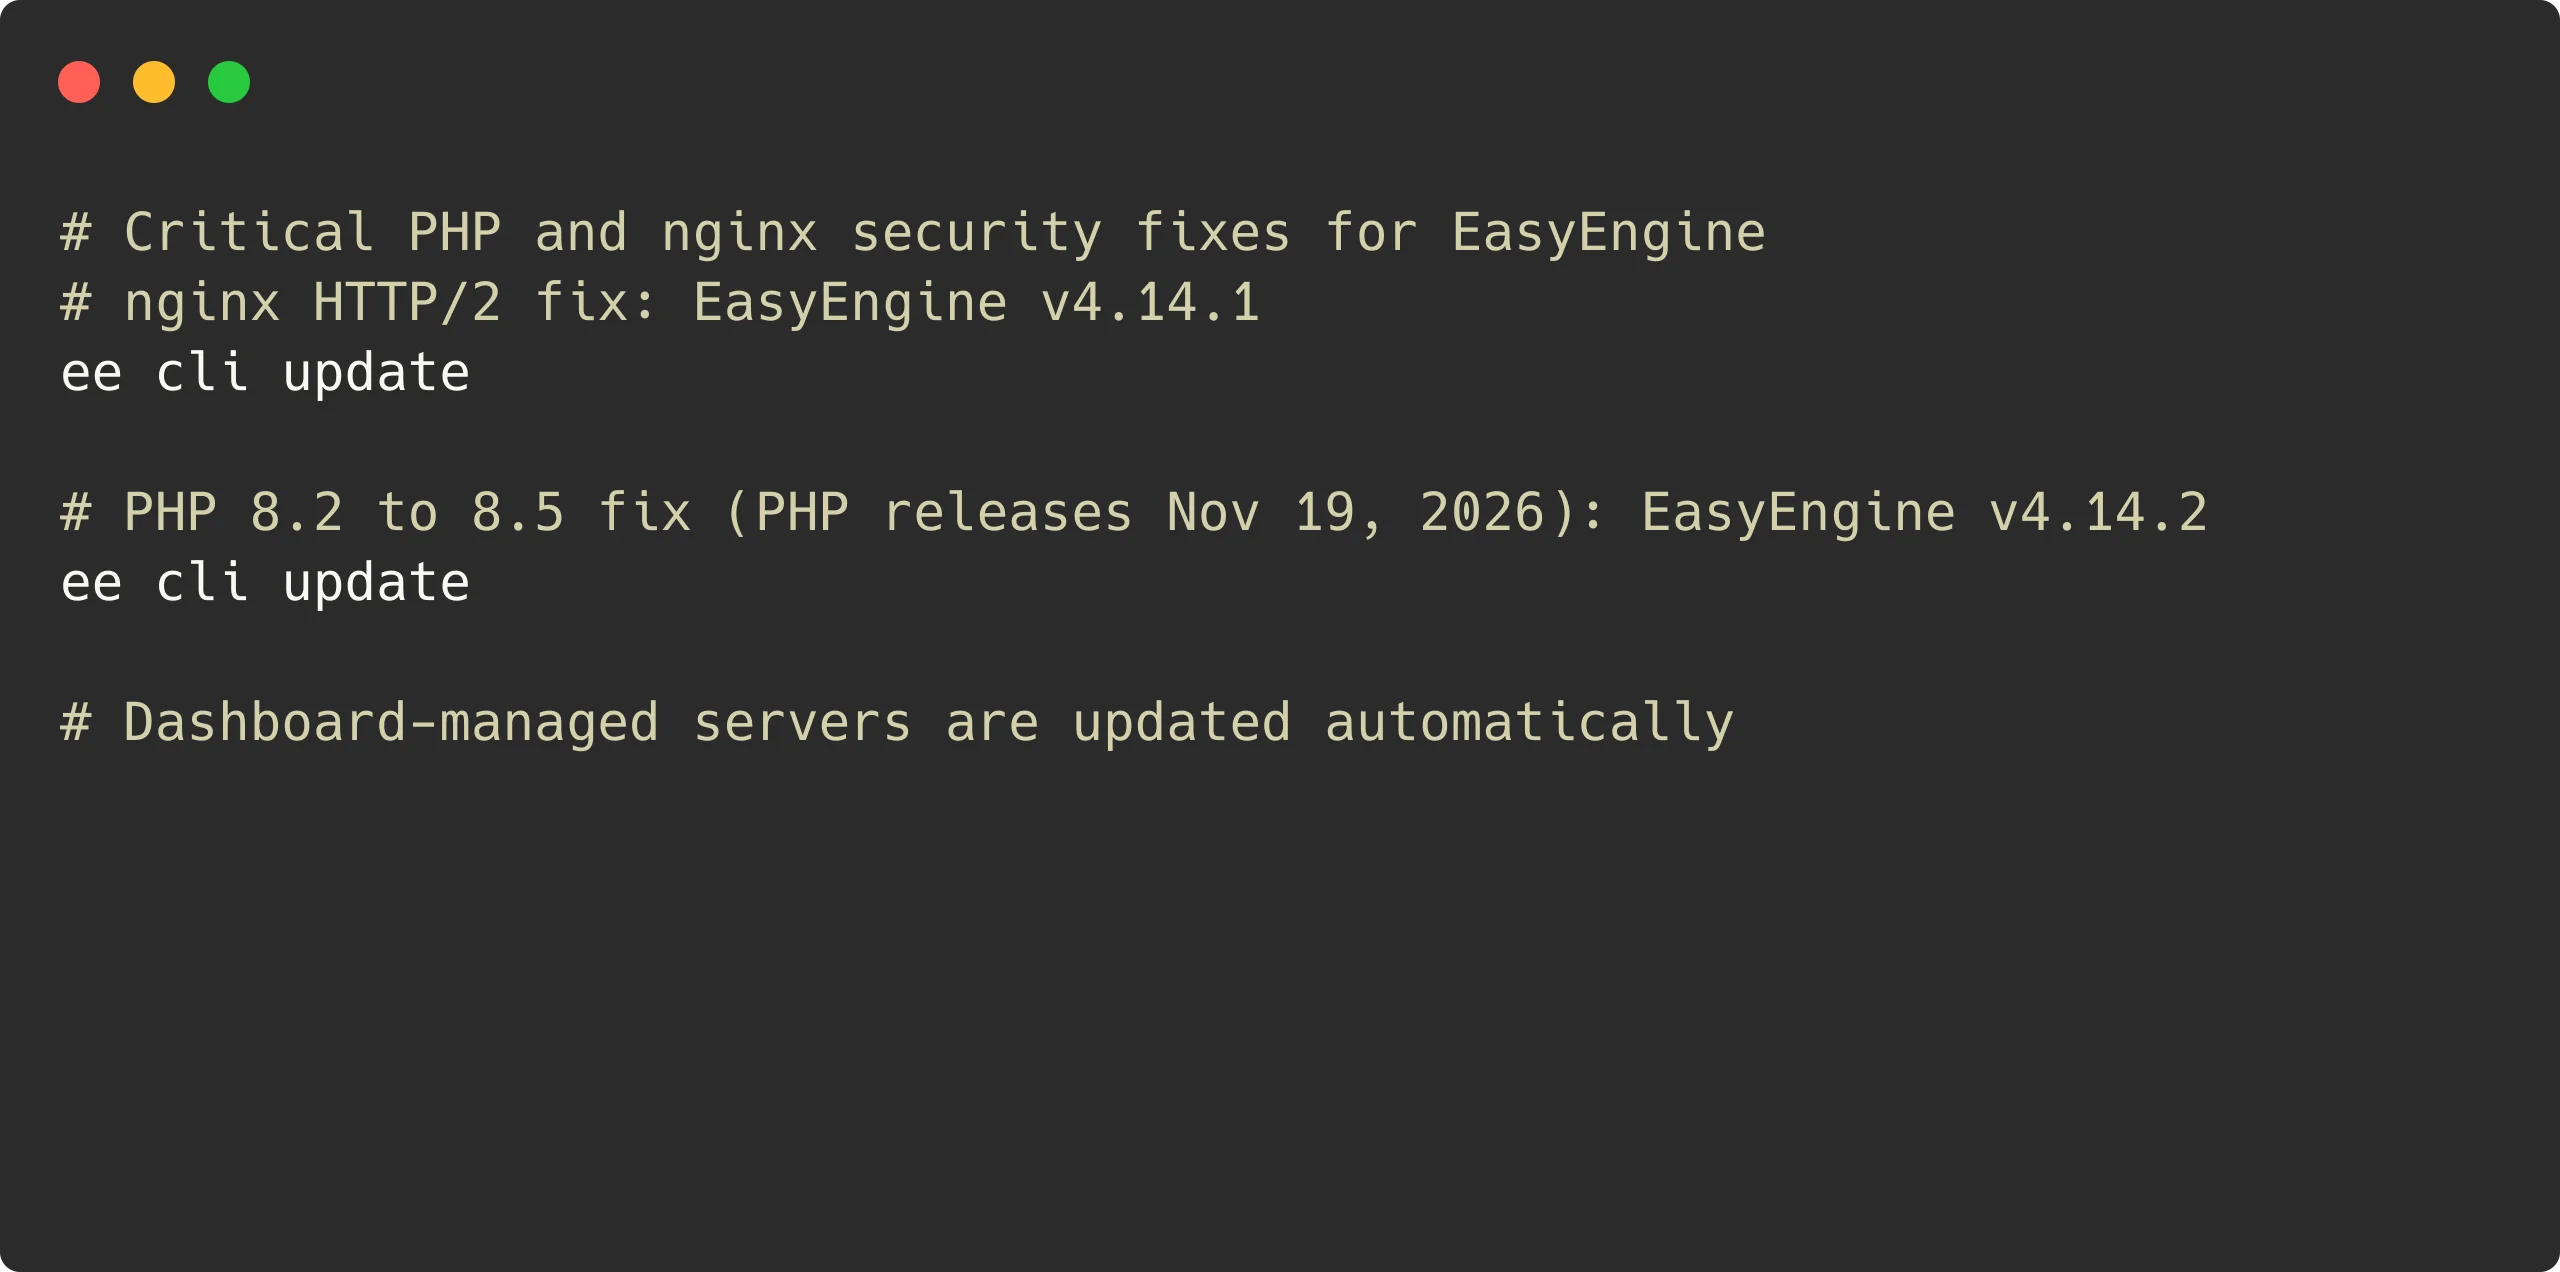
Critical PHP and nginx Security Fixes: EasyEngine’s Release Plan
EasyEngine v4.14.2 is out with PHP’s security fixes for PHP 8.2 to 8.5, and EasyEngine v4.14.1 with nginx’s fixes for two HTTP/2 vulnerabilities in the proxy that serves every HTTPS site. On CLI-managed servers, run ee cli update. Dashboard-managed servers are already updated to v4.14.2.
-
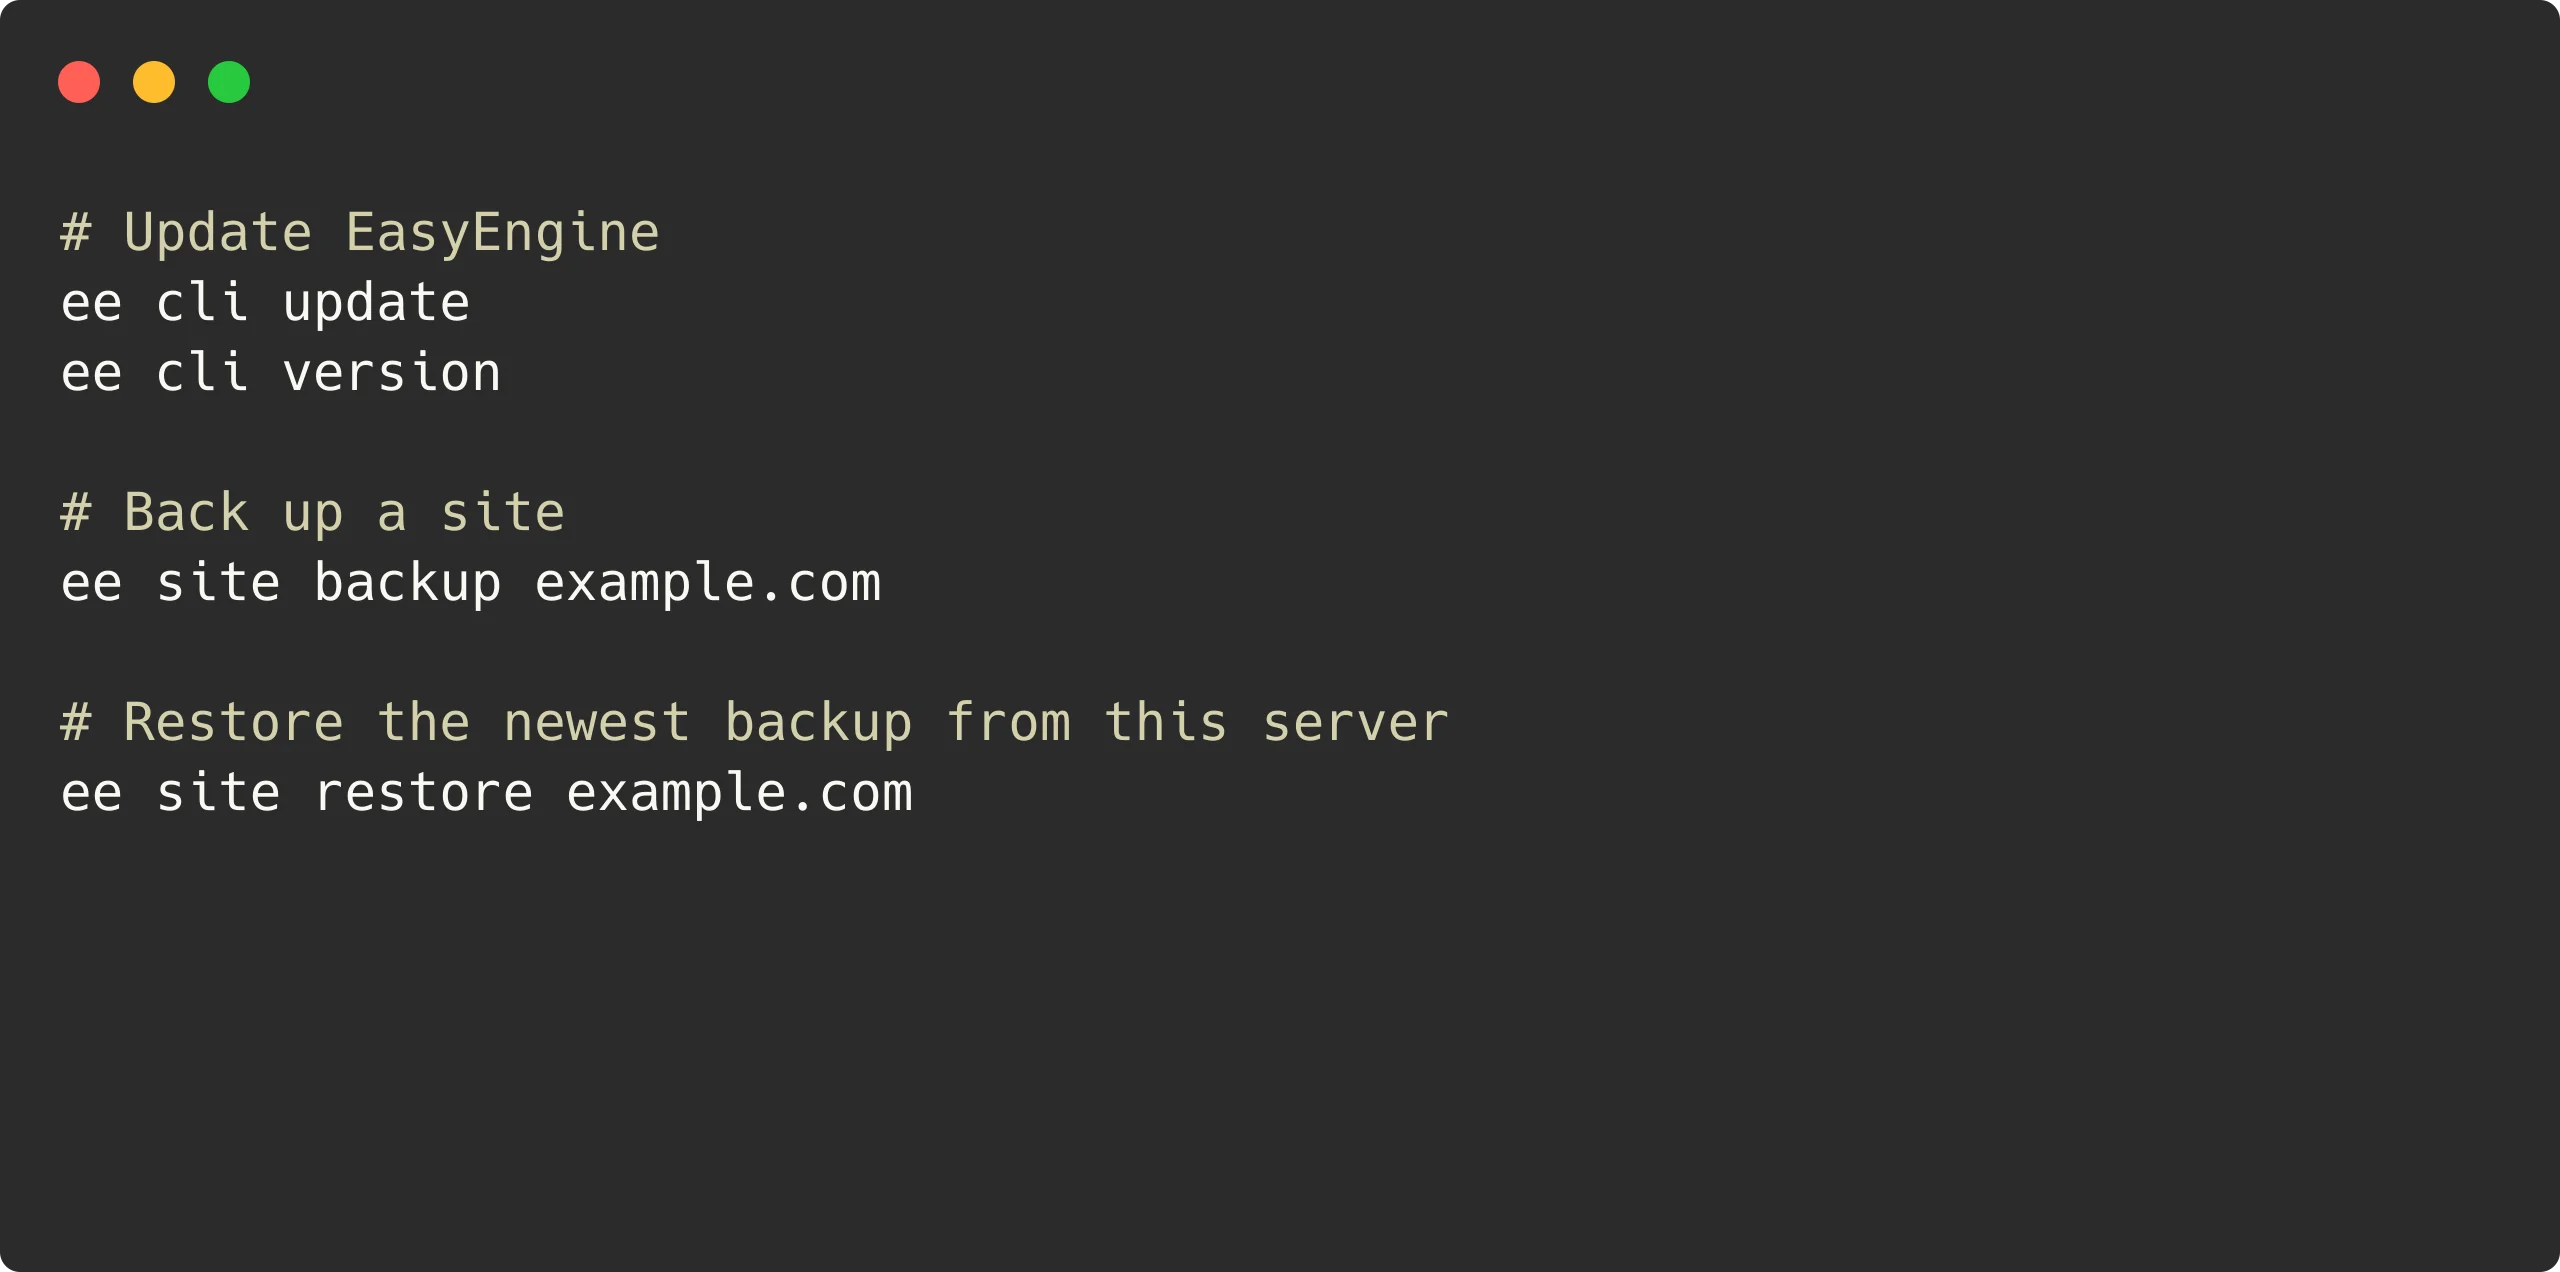
EasyEngine v4.14.0 Released
EasyEngine v4.14.0 changes what a failure leaves behind. A restore that fails before the backup is fully in place puts the site back as it was, an update rolls back if a service it recreates doesn’t come up, and every backup archive is tested before upload. Read the update notes, then run ee cli update.
-
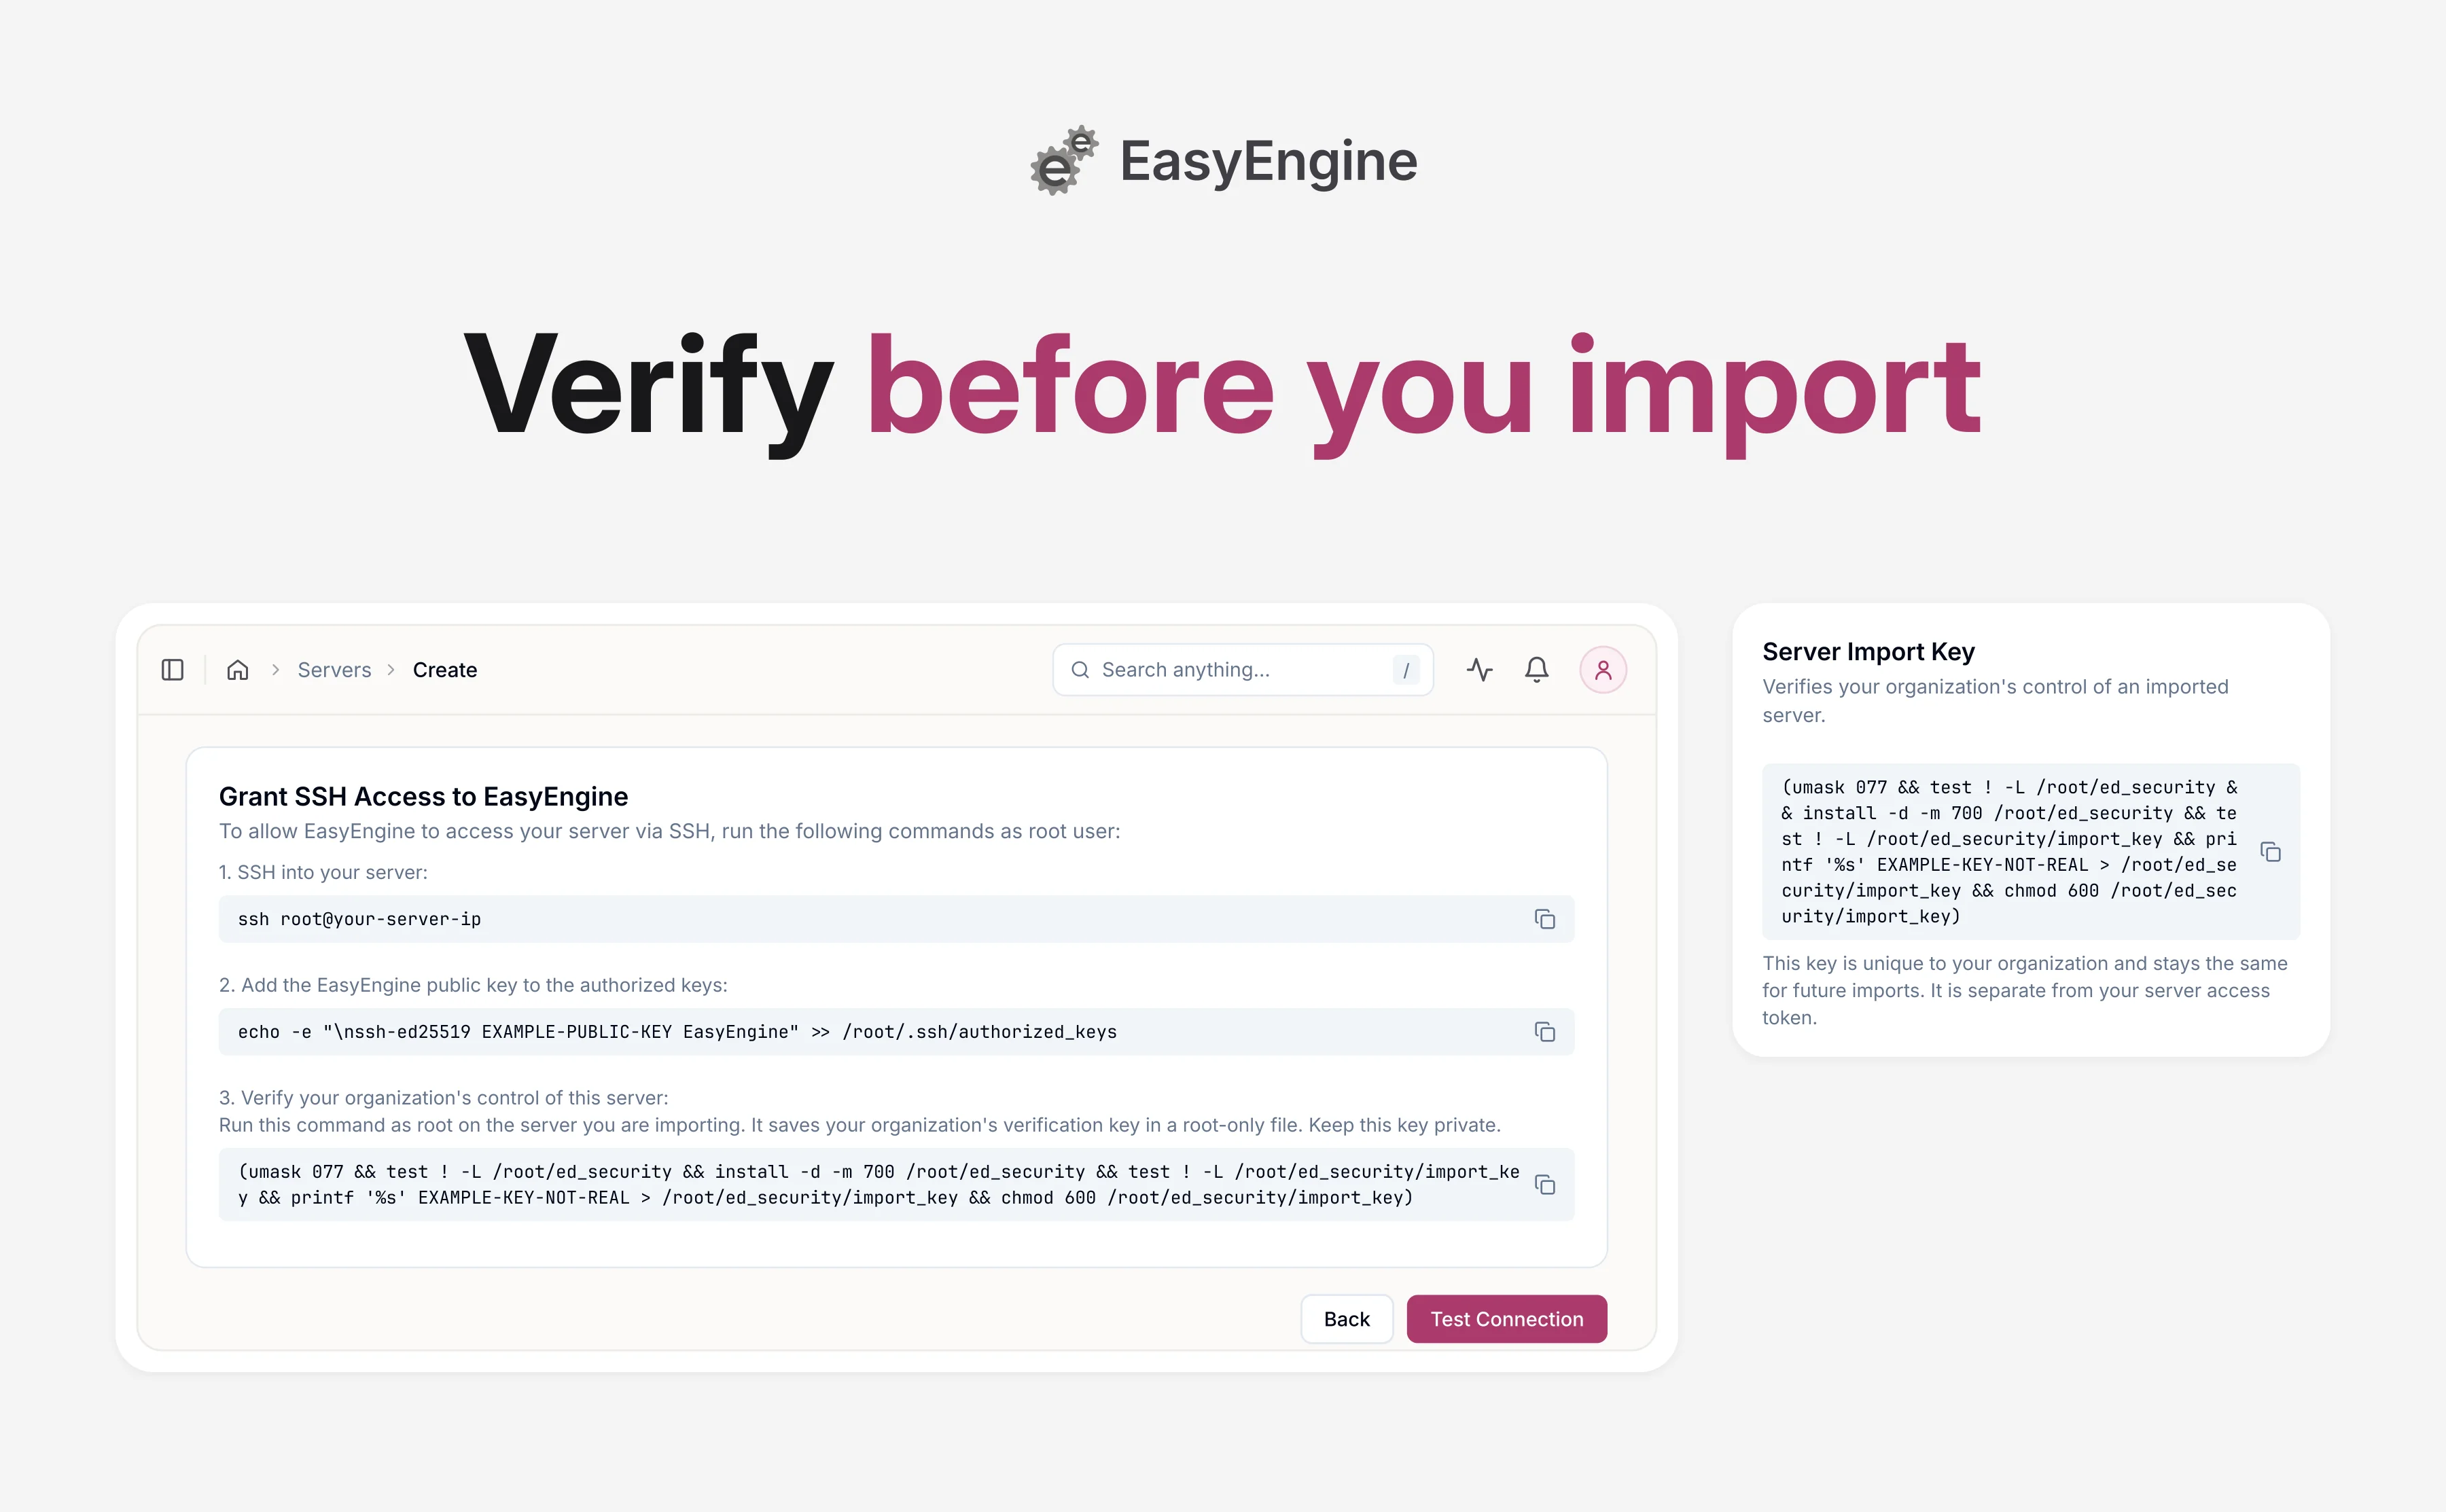
EasyEngine Dashboard security update: verified server imports, safer sign-ups
EasyEngine Dashboard now adds a server you import to your organization only after it finds your organization’s key in a root-only file, which only someone with root on that server can write. Email sign-ups start clean when you verify your email, and 26 security fixes ship in all.
-
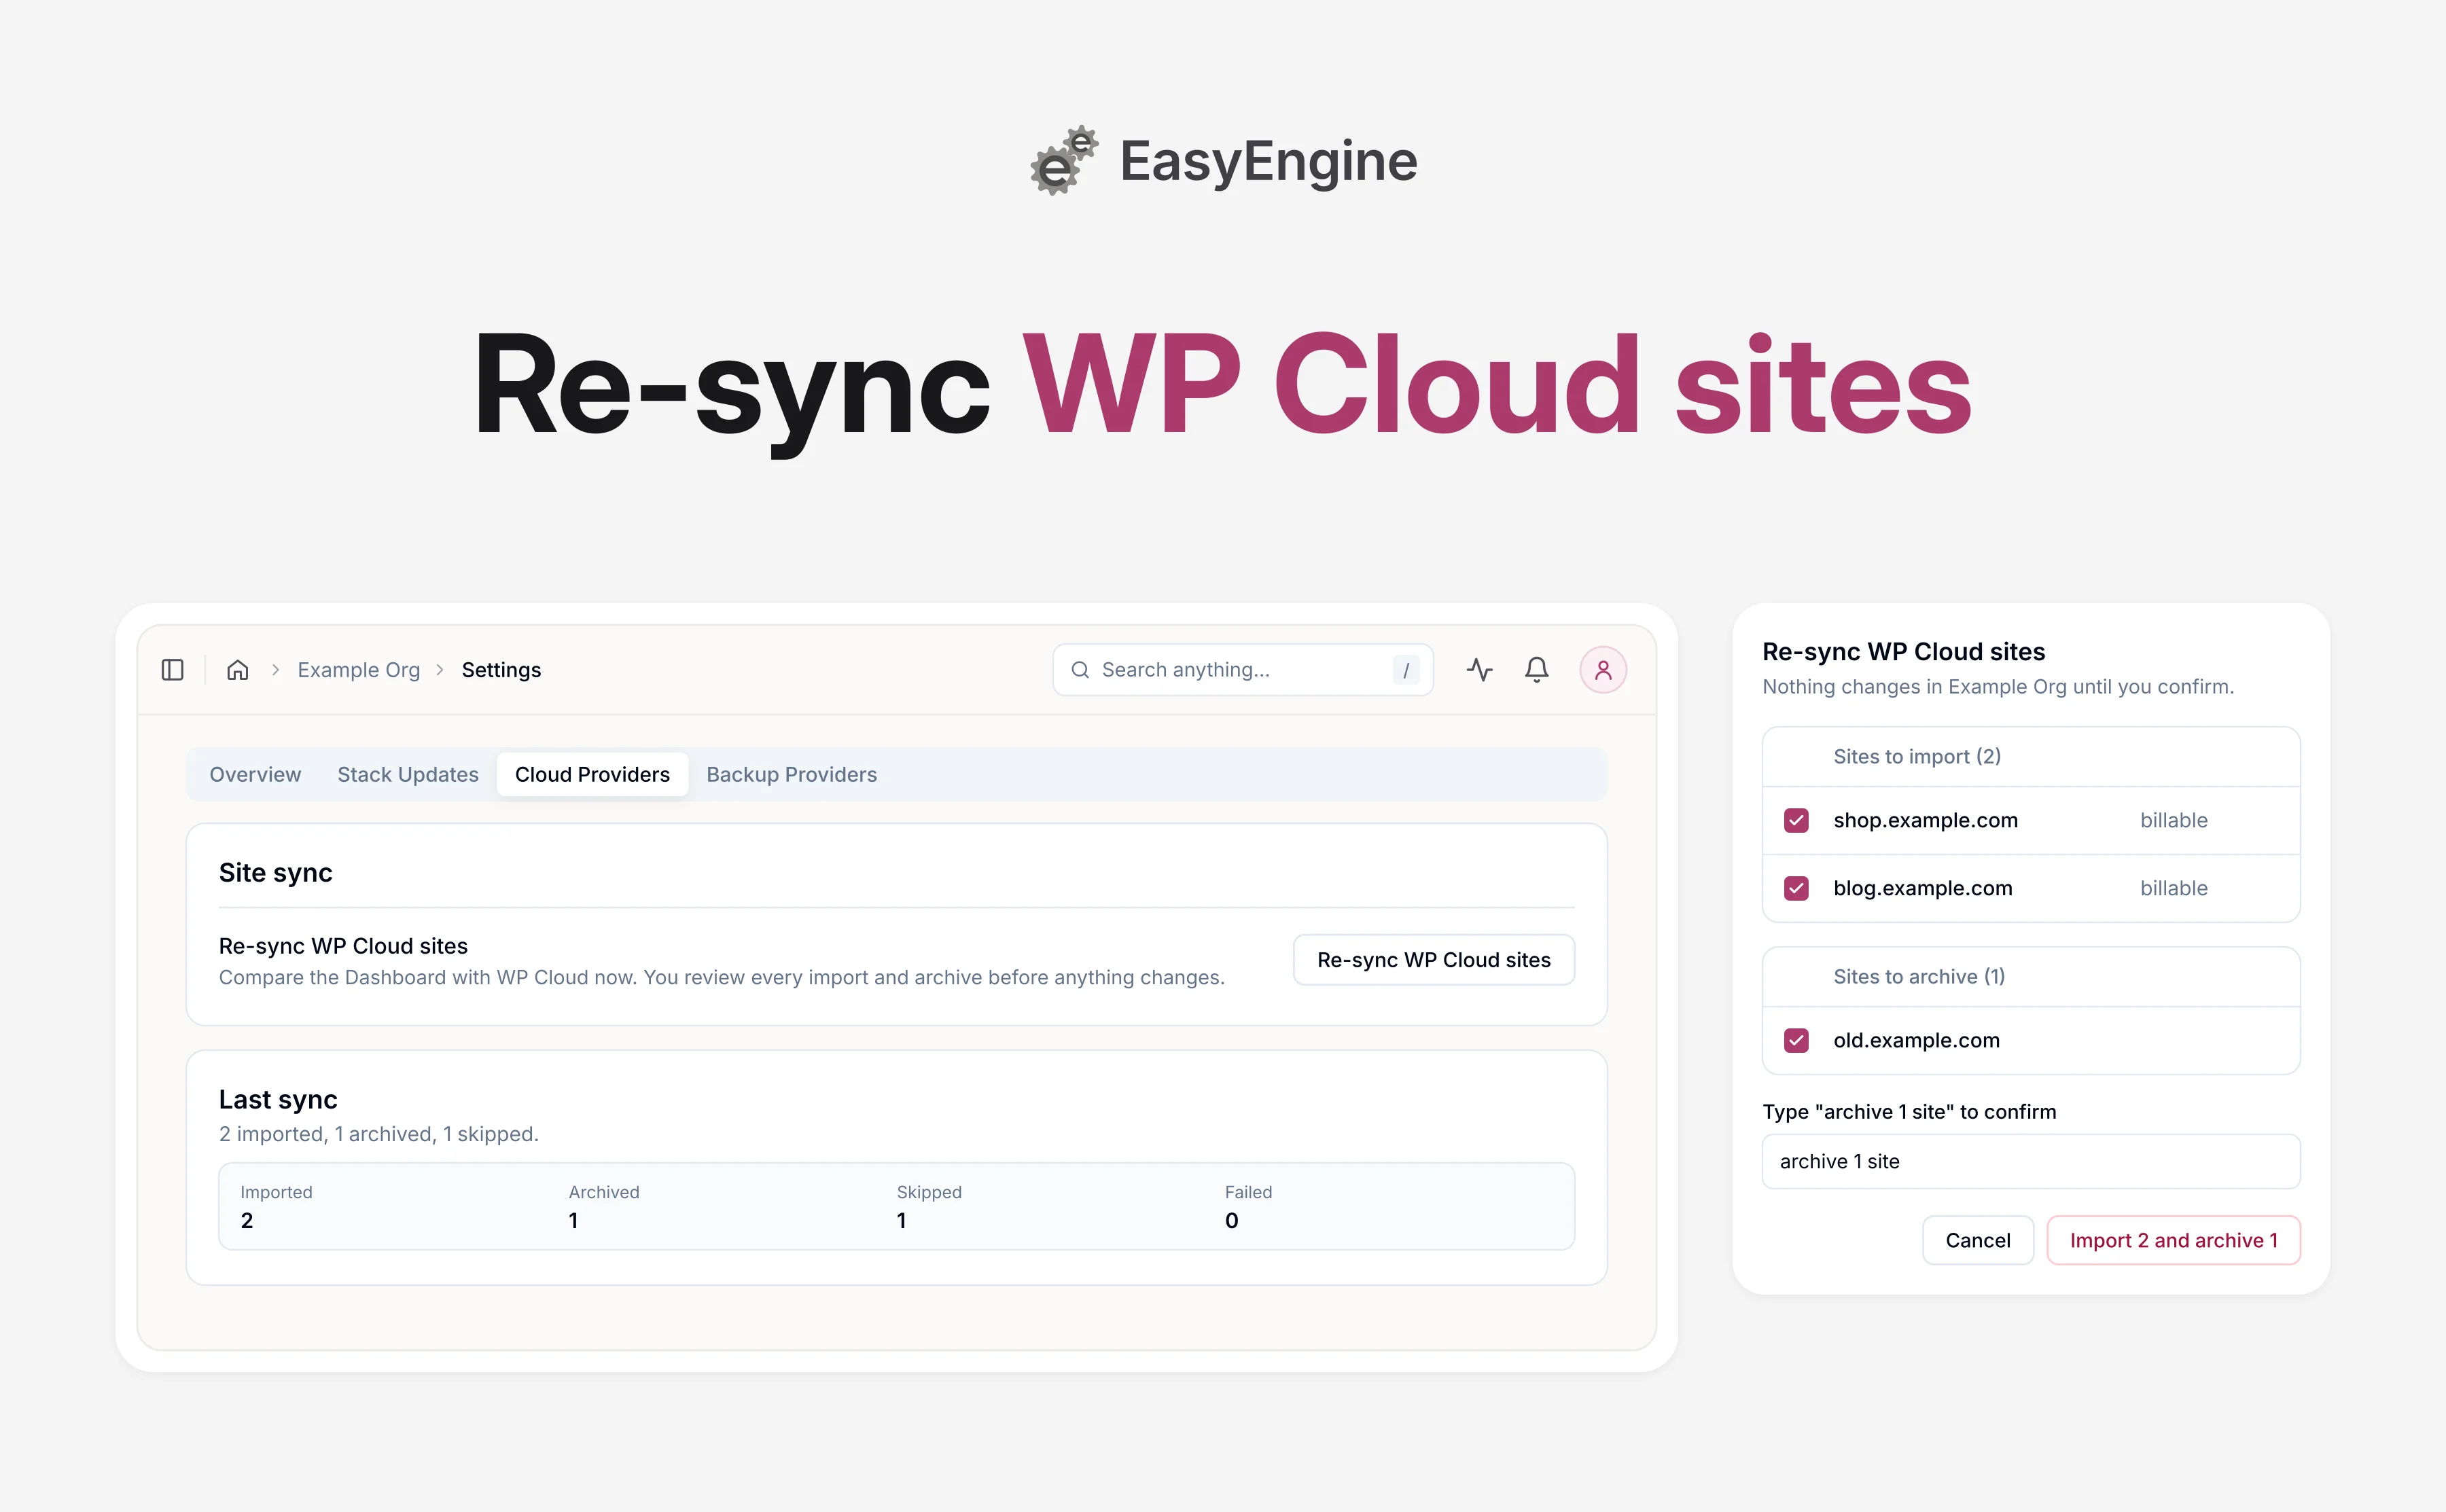
EasyEngine Dashboard now lets you re-sync your WP Cloud sites
Organization owners and admins can now re-sync their WP Cloud sites in EasyEngine Dashboard, including sites created or deleted outside it through the WP Cloud API or a CI/CD pipeline. Review what’s new and what’s gone, then import and archive the ones you choose, or turn on the daily sync.
-
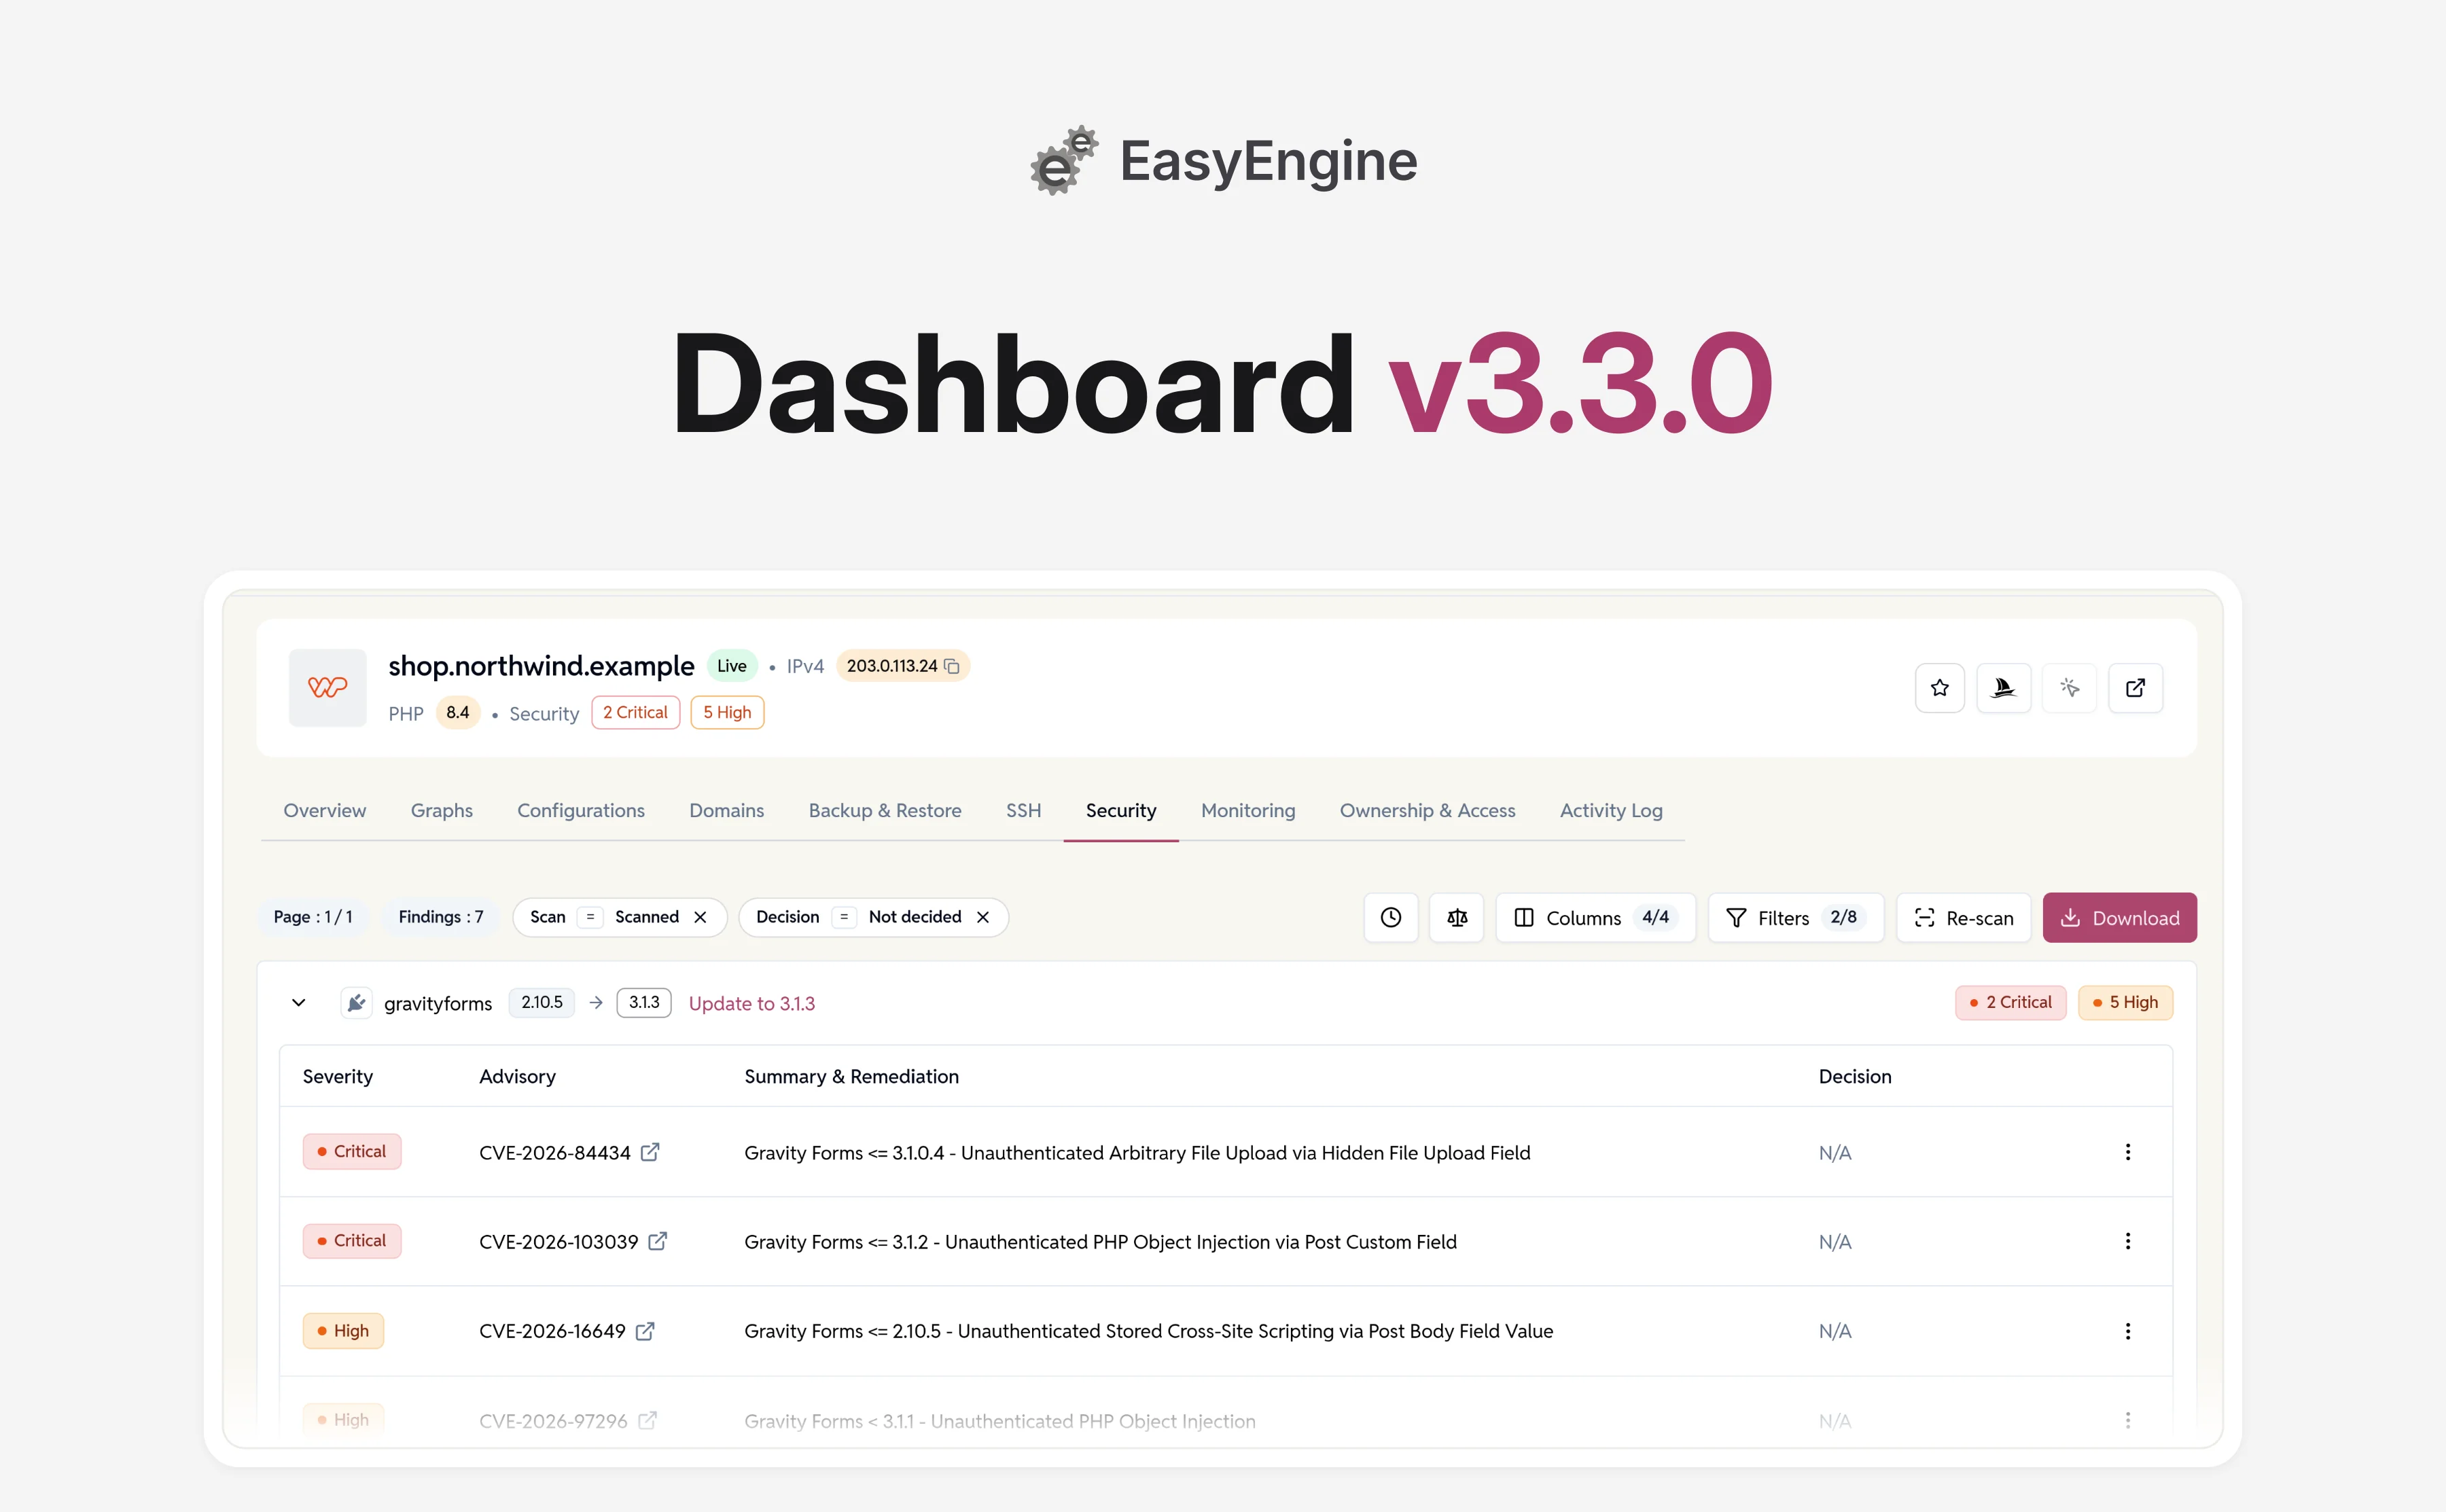
EasyEngine Dashboard v3.3.0 Released
Starting with EasyEngine Dashboard v3.3.0, Security Advisories also check your WP Cloud sites, not just your EasyEngine sites. Each live, connected WP Cloud site is checked daily for vulnerable WordPress core, plugins and themes, with findings on its Security tab and in the security digest. Sites and servers also get an Ownership & Access tab.
-
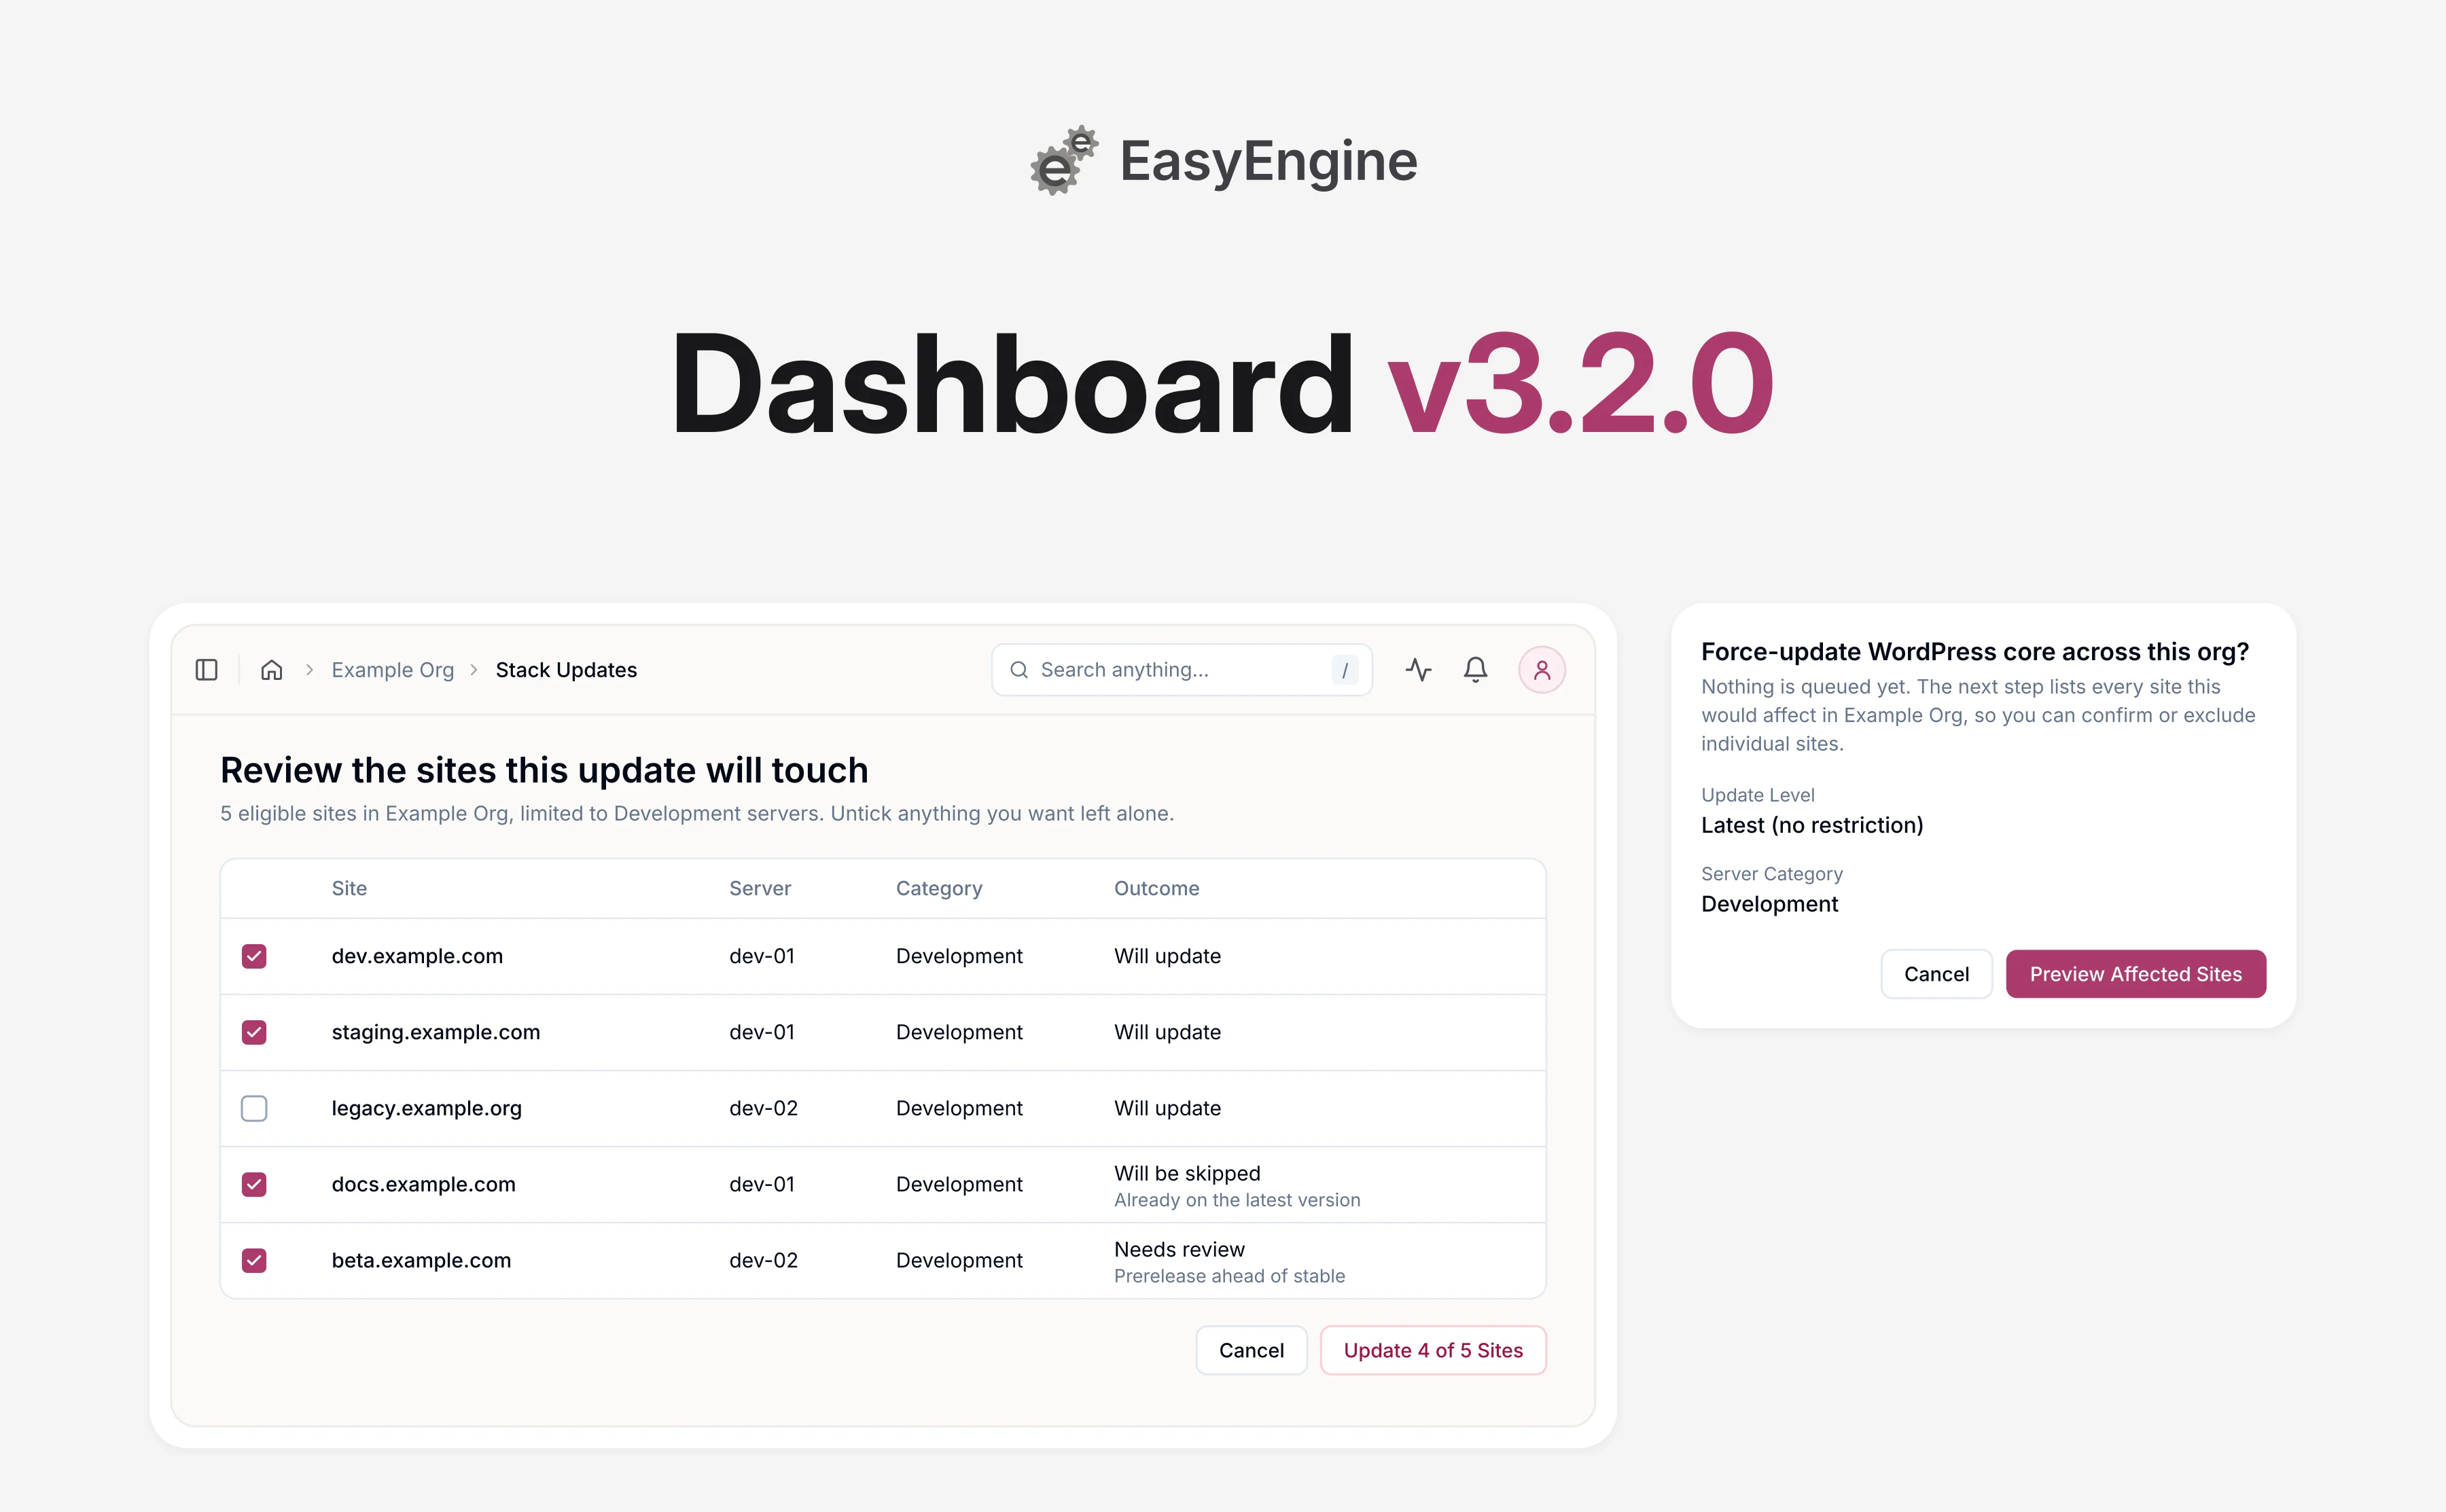
EasyEngine Dashboard v3.2.0 Released
EasyEngine Dashboard v3.2.0 adds a review step to bulk WordPress core updates: see every site an update will touch, limit an organization-wide run to Production or Development servers, and untick sites before anything runs. A failed CI/CD setup also no longer marks a new site as failed.
-
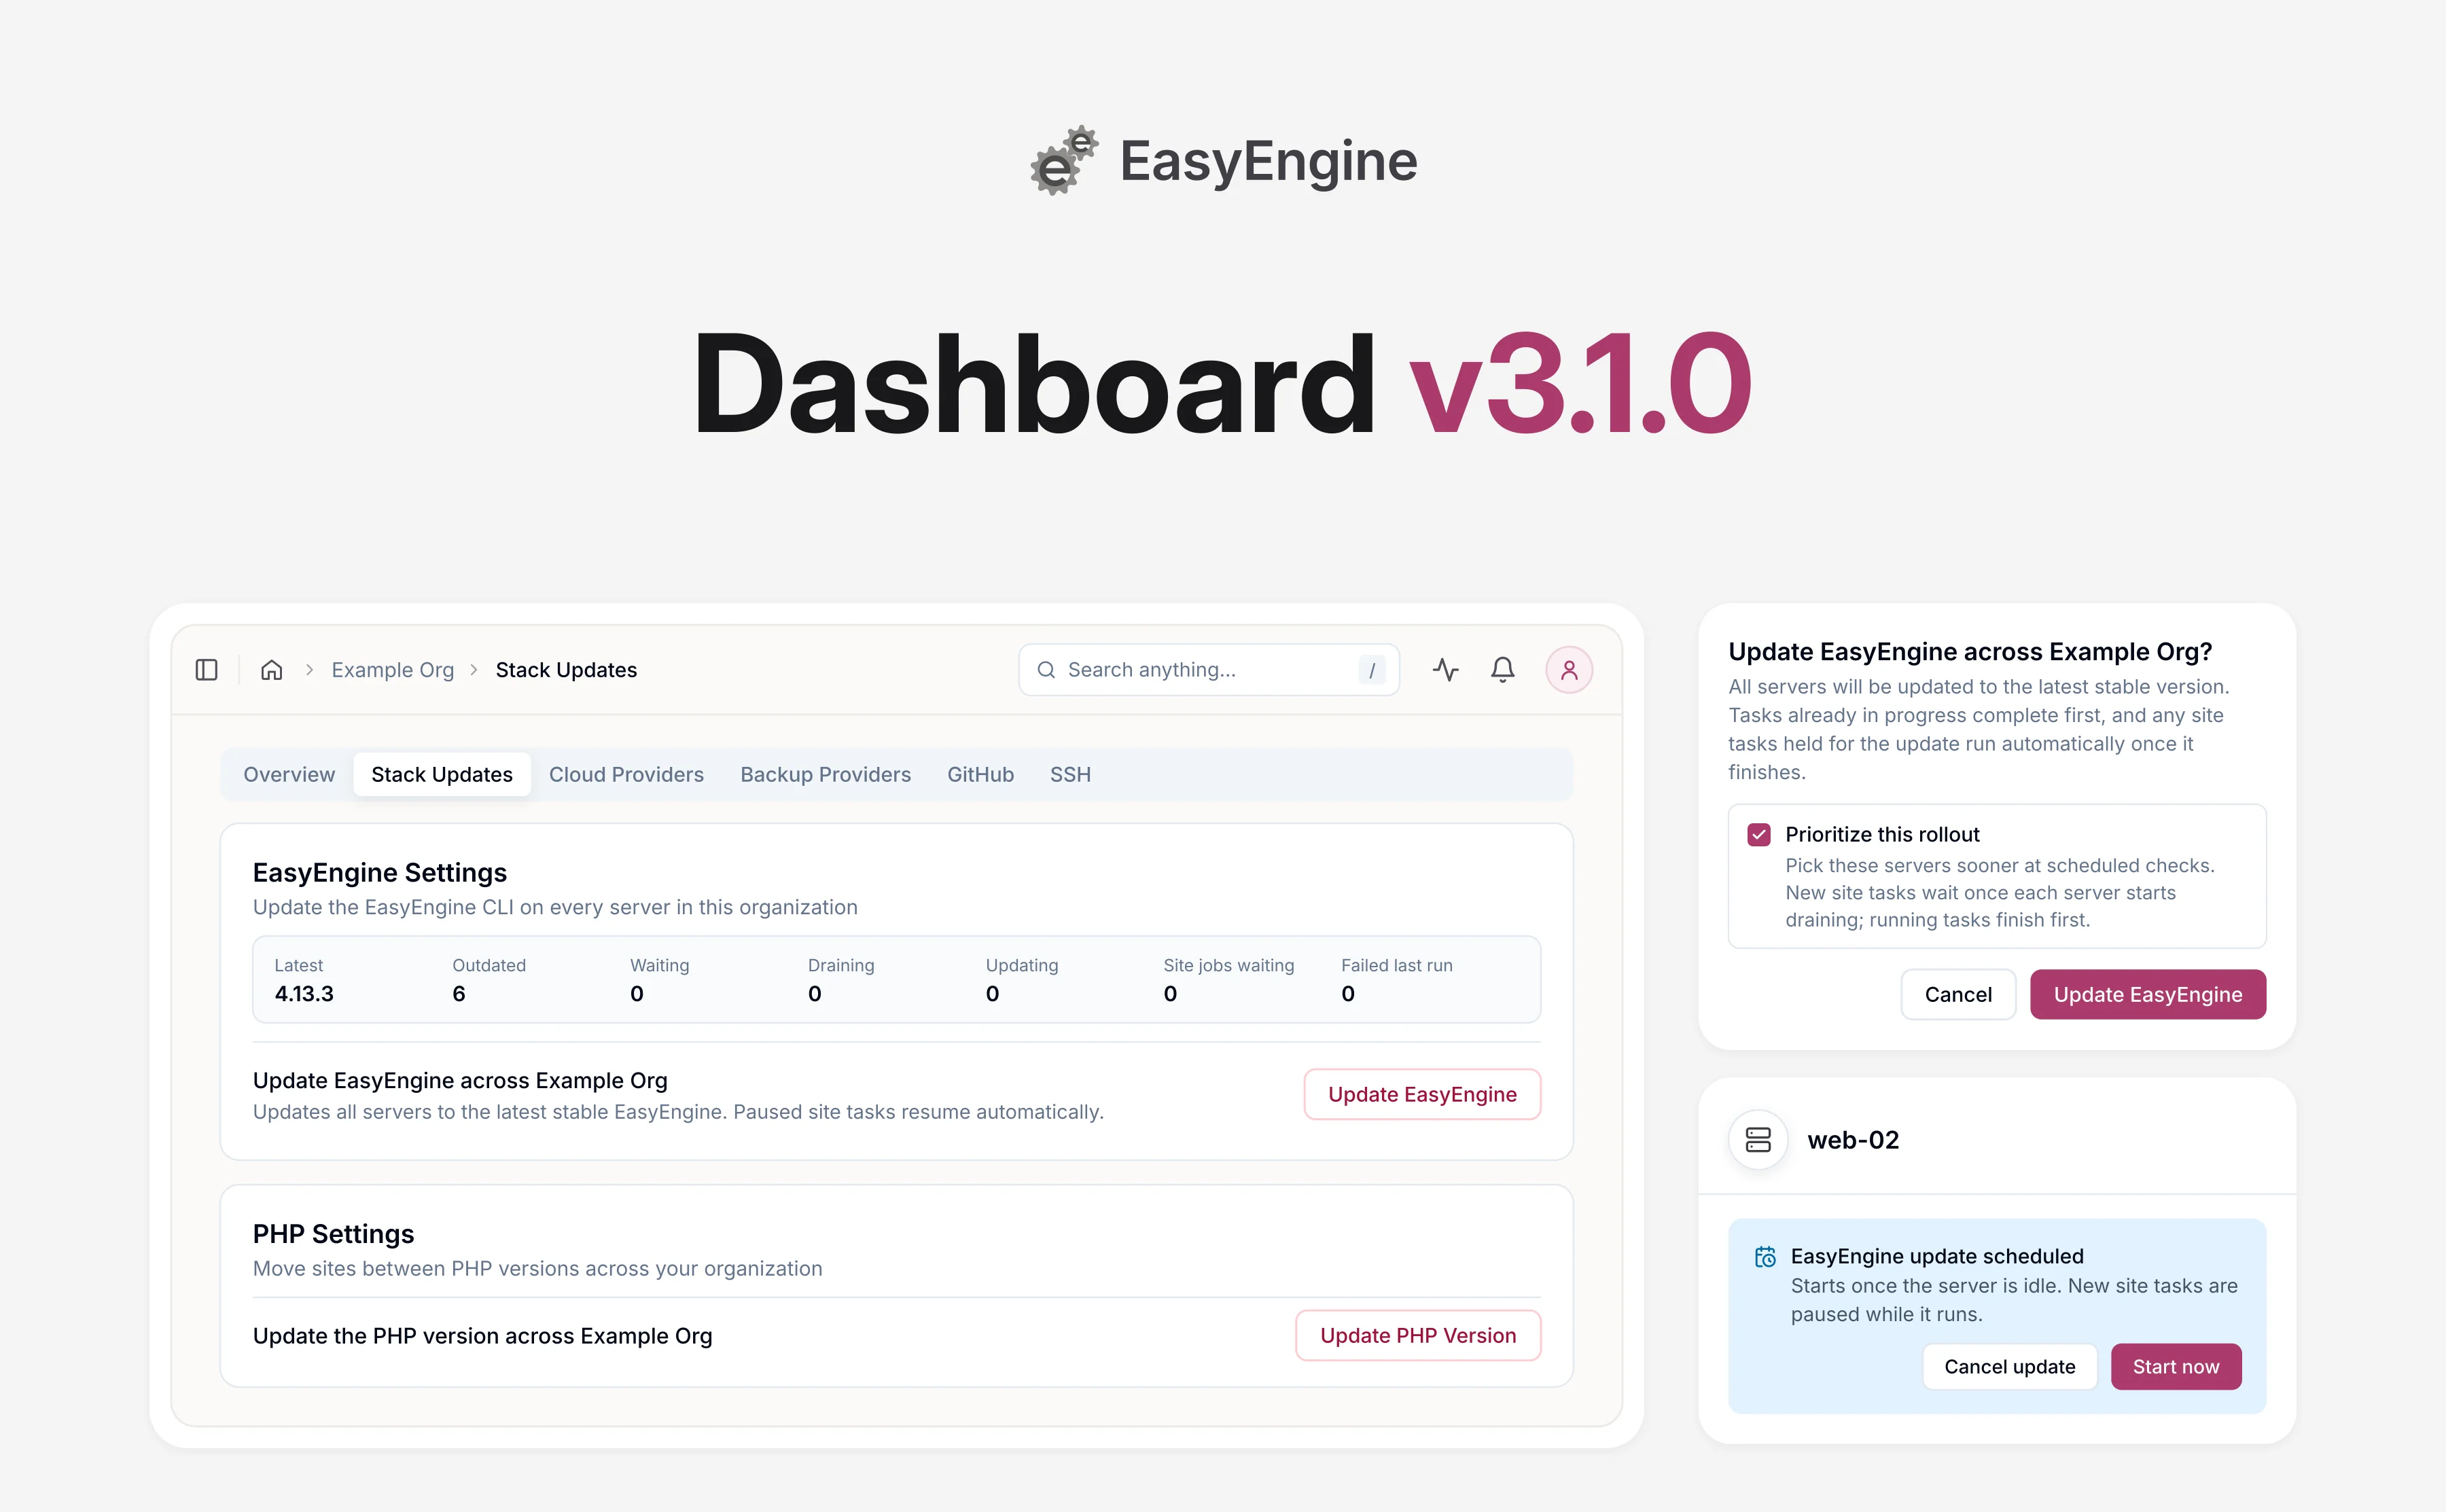
EasyEngine Dashboard v3.1.0 Released
EasyEngine Dashboard v3.1.0 lets organization owners, admins and managers request an EasyEngine update across their servers. Owners and admins can share servers with child organizations, and notification preferences are now separate for each organization.
-
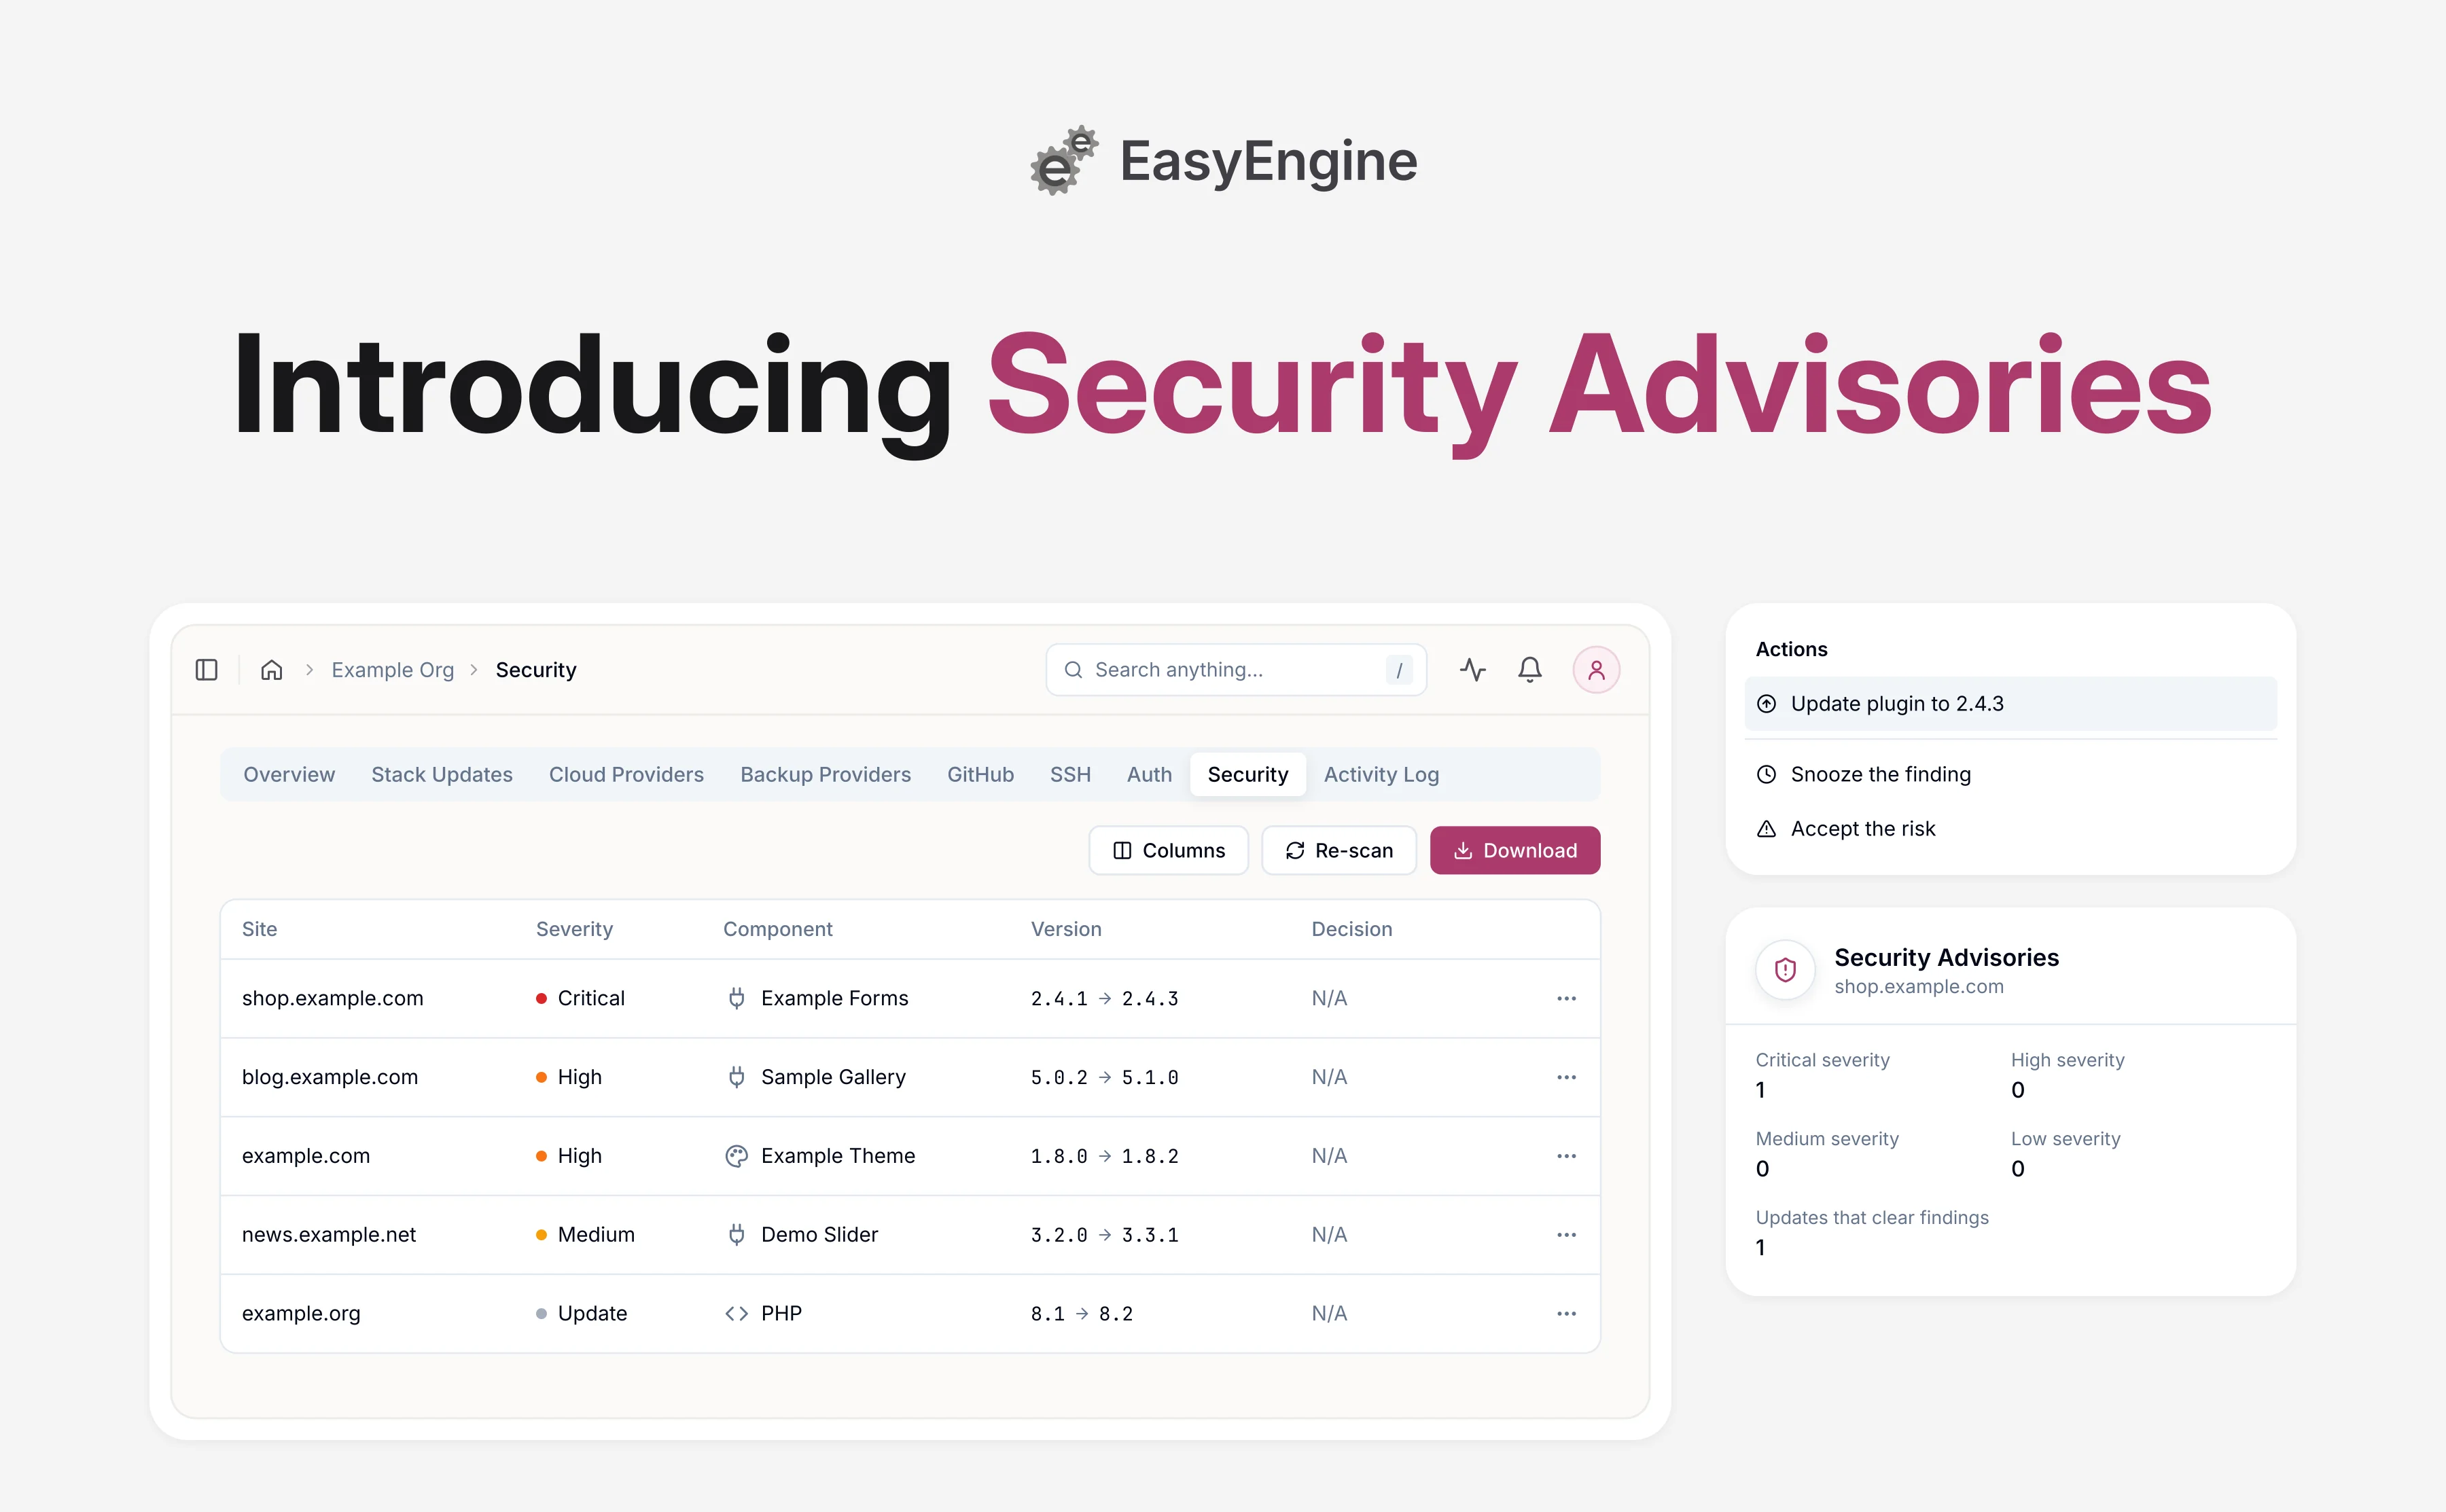
EasyEngine Dashboard now flags vulnerable plugins, themes and WordPress core
Security Advisories in EasyEngine Dashboard checks the plugins, themes and WordPress core on eligible live WordPress sites on your EasyEngine servers against published security advisories, shows which sites need attention, and lets you update the affected plugin or theme from the same screen.
-
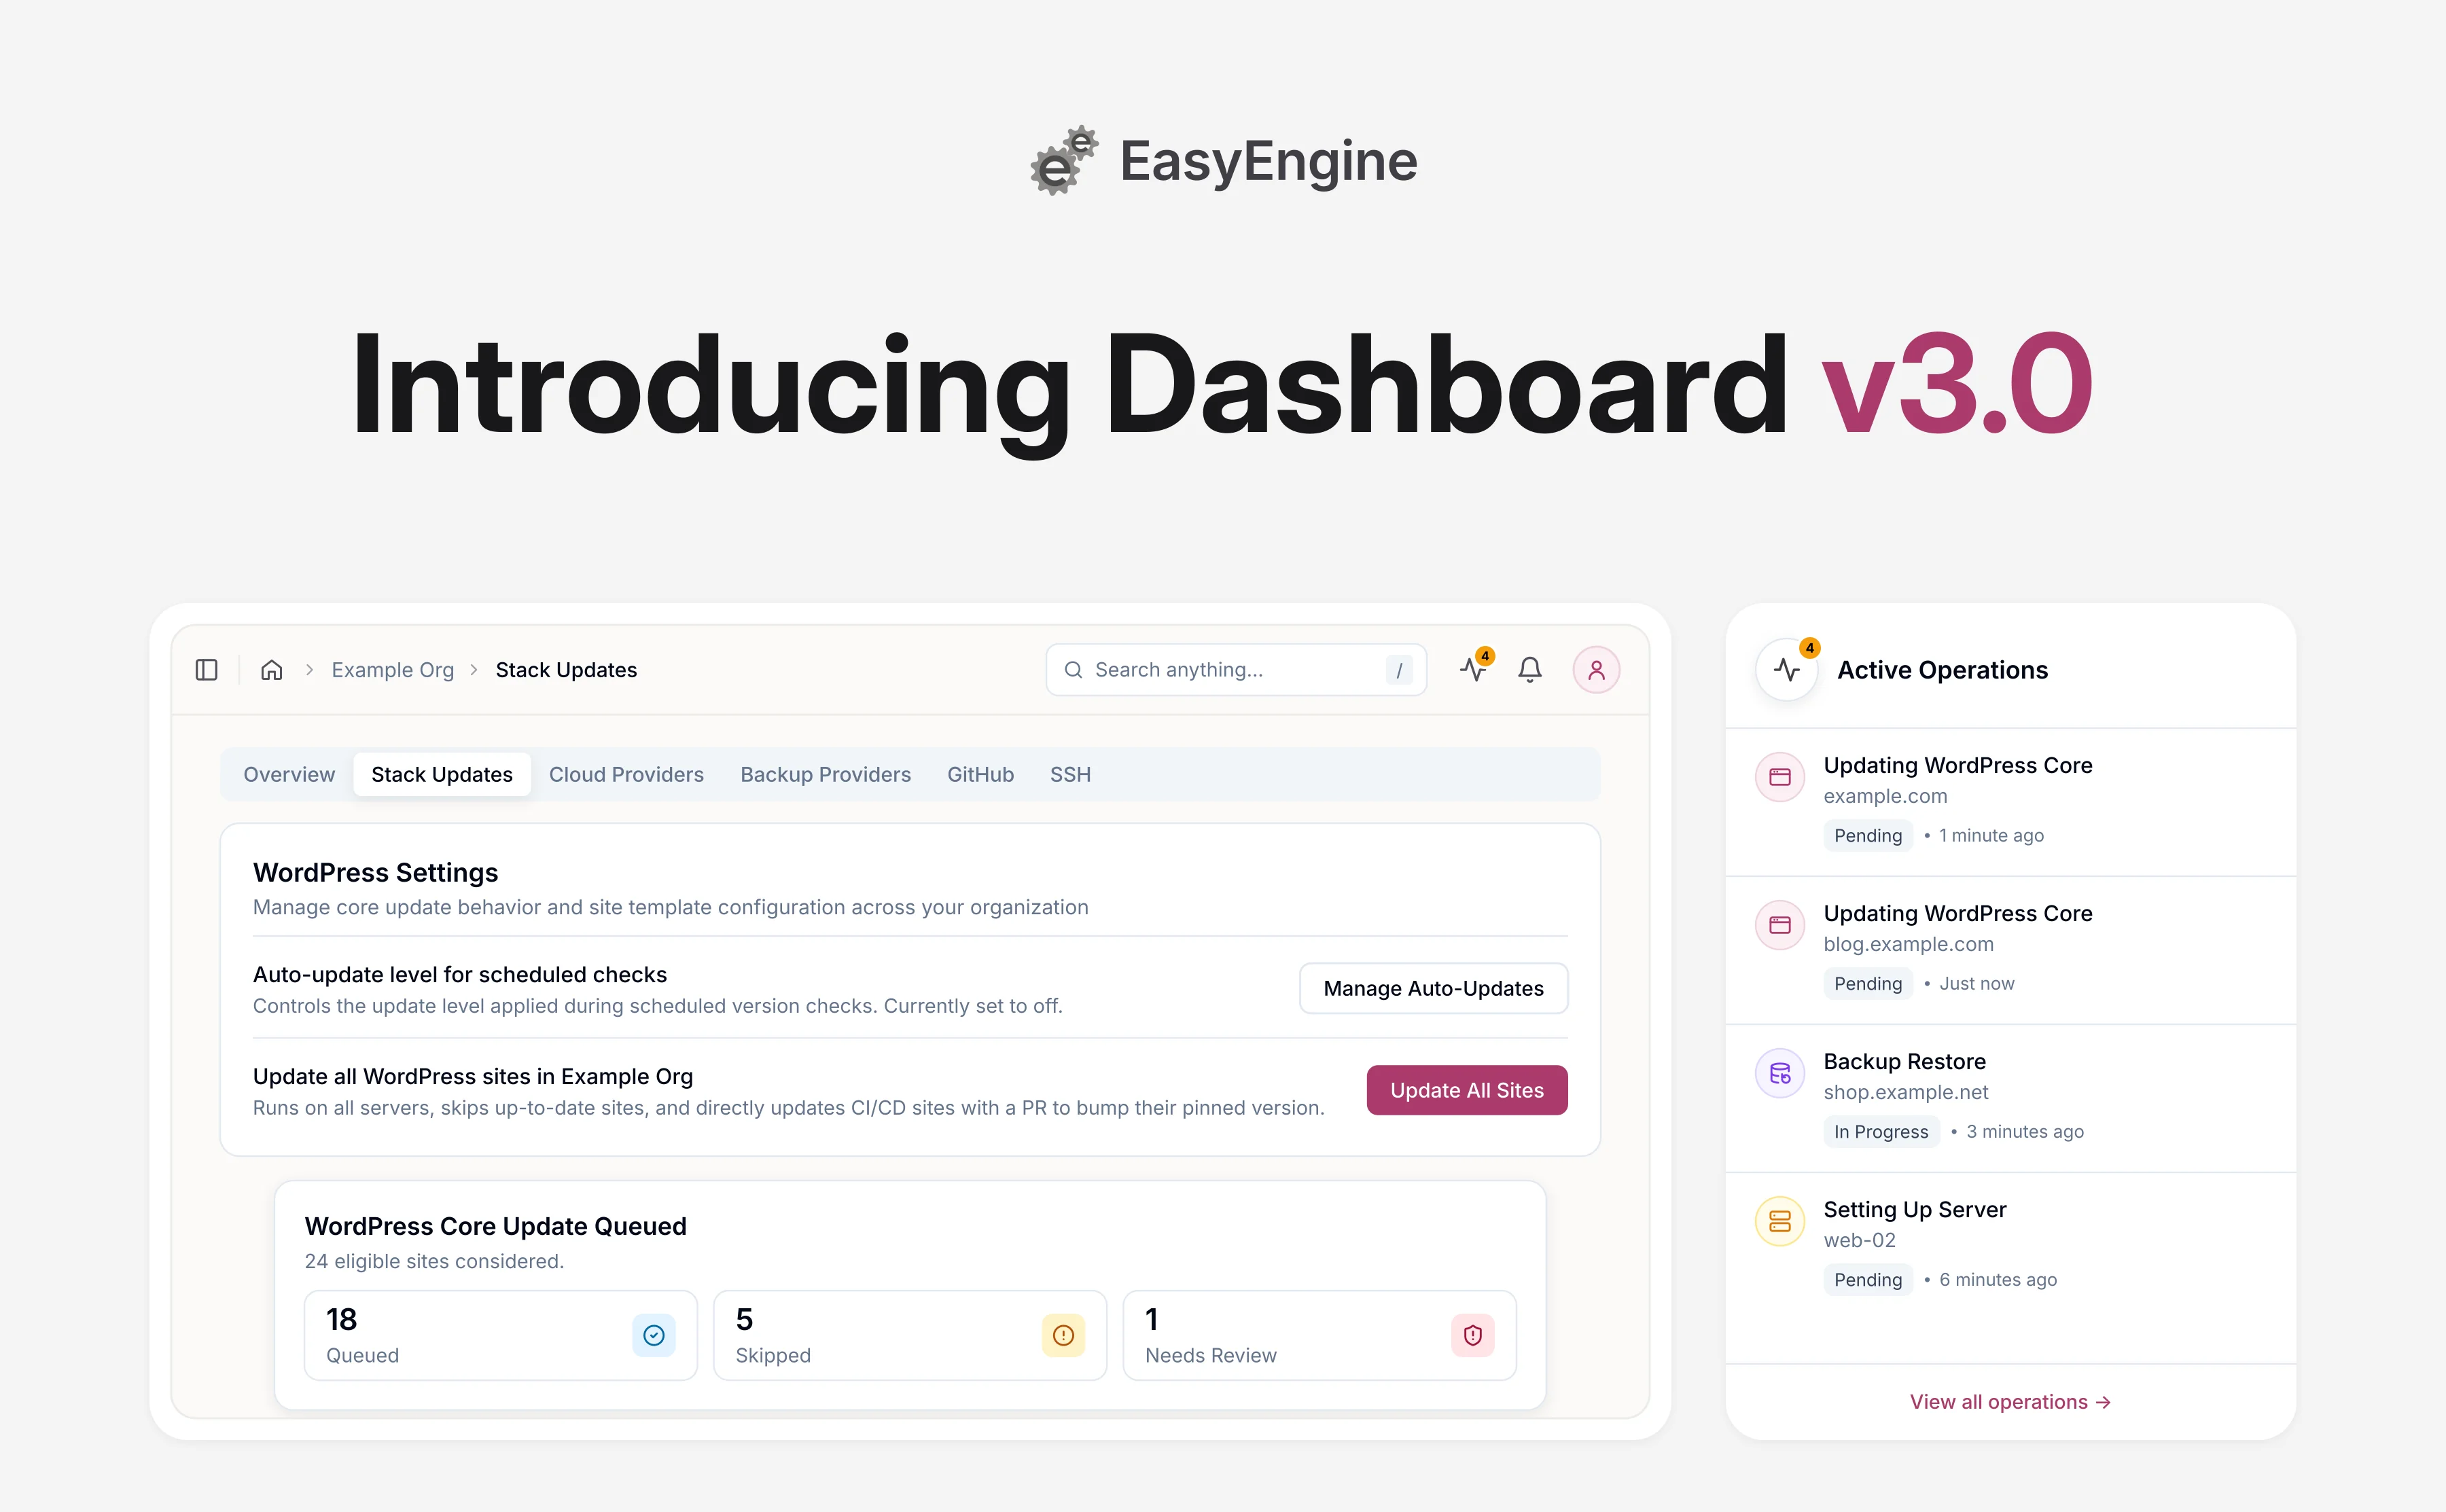
EasyEngine Dashboard v3.0 Released
EasyEngine Dashboard v3.0 is out, with bulk WordPress core updates across a server or a whole organization, backup restores and egress rules for WP Cloud sites, a live view of background jobs, and Ubuntu 26.04 servers.
-
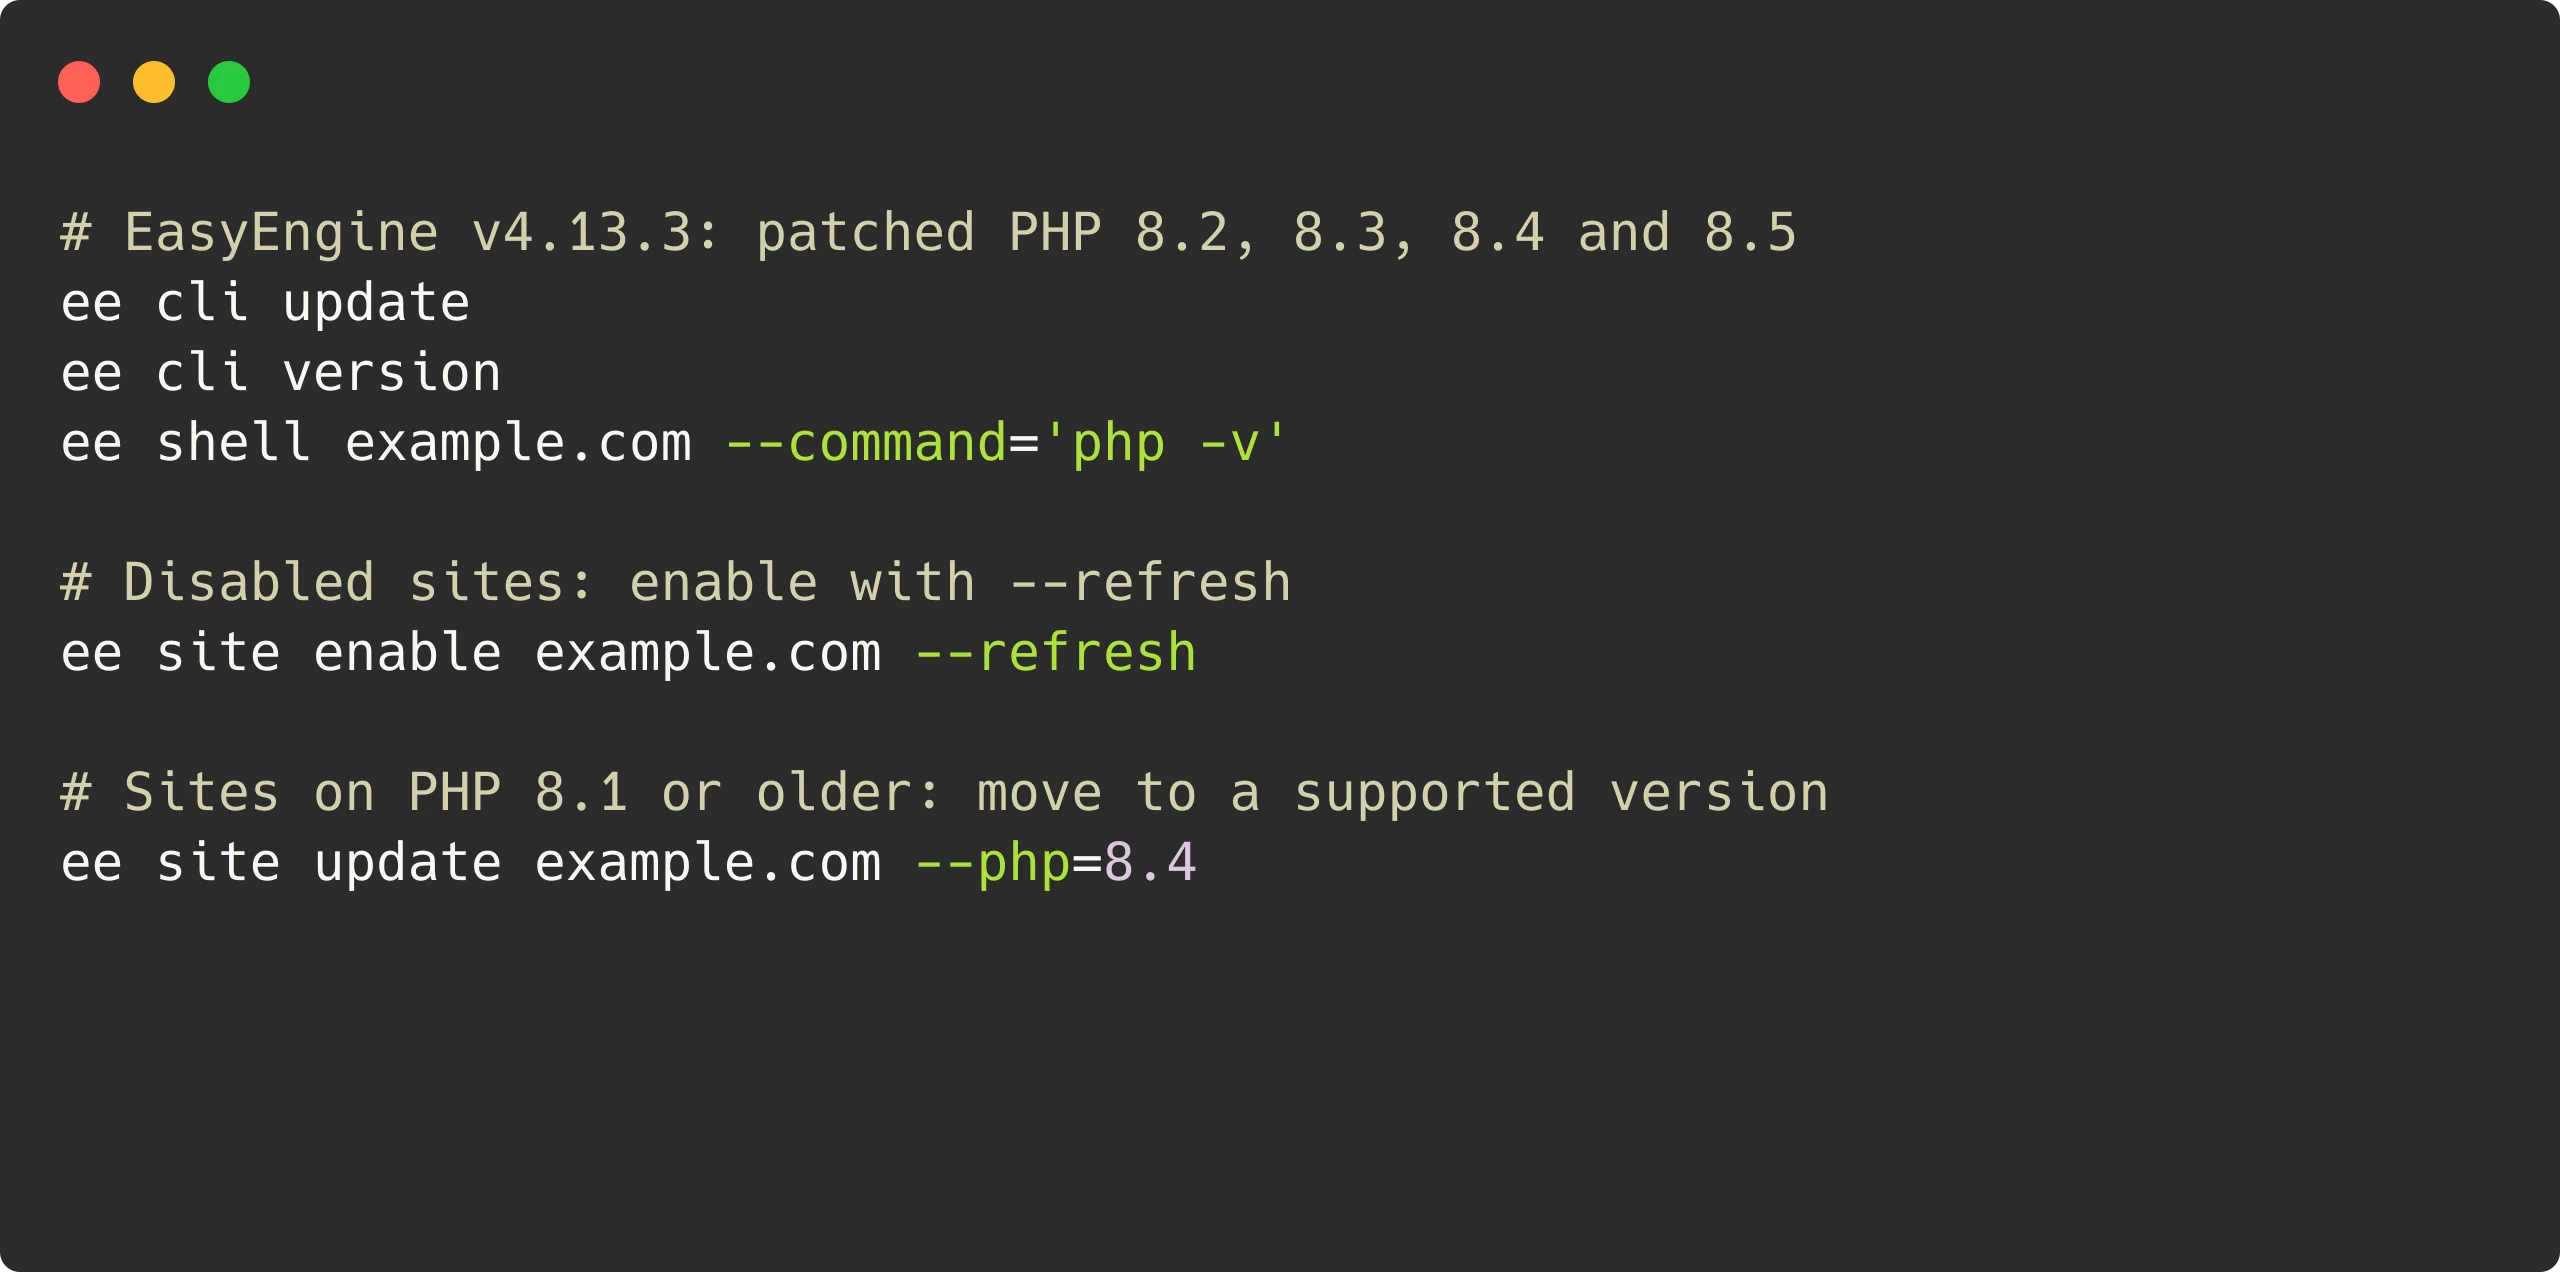
EasyEngine v4.13.3 Fixes Critical PHP Vulnerabilities
EasyEngine v4.13.3 moves enabled sites on PHP 8.2 through 8.5 to patched images for two critical PHP vulnerabilities, and turns off session upload progress on WordPress and PHP sites on Linux. On CLI-managed servers, run ee cli update. Dashboard-managed servers update automatically.
-
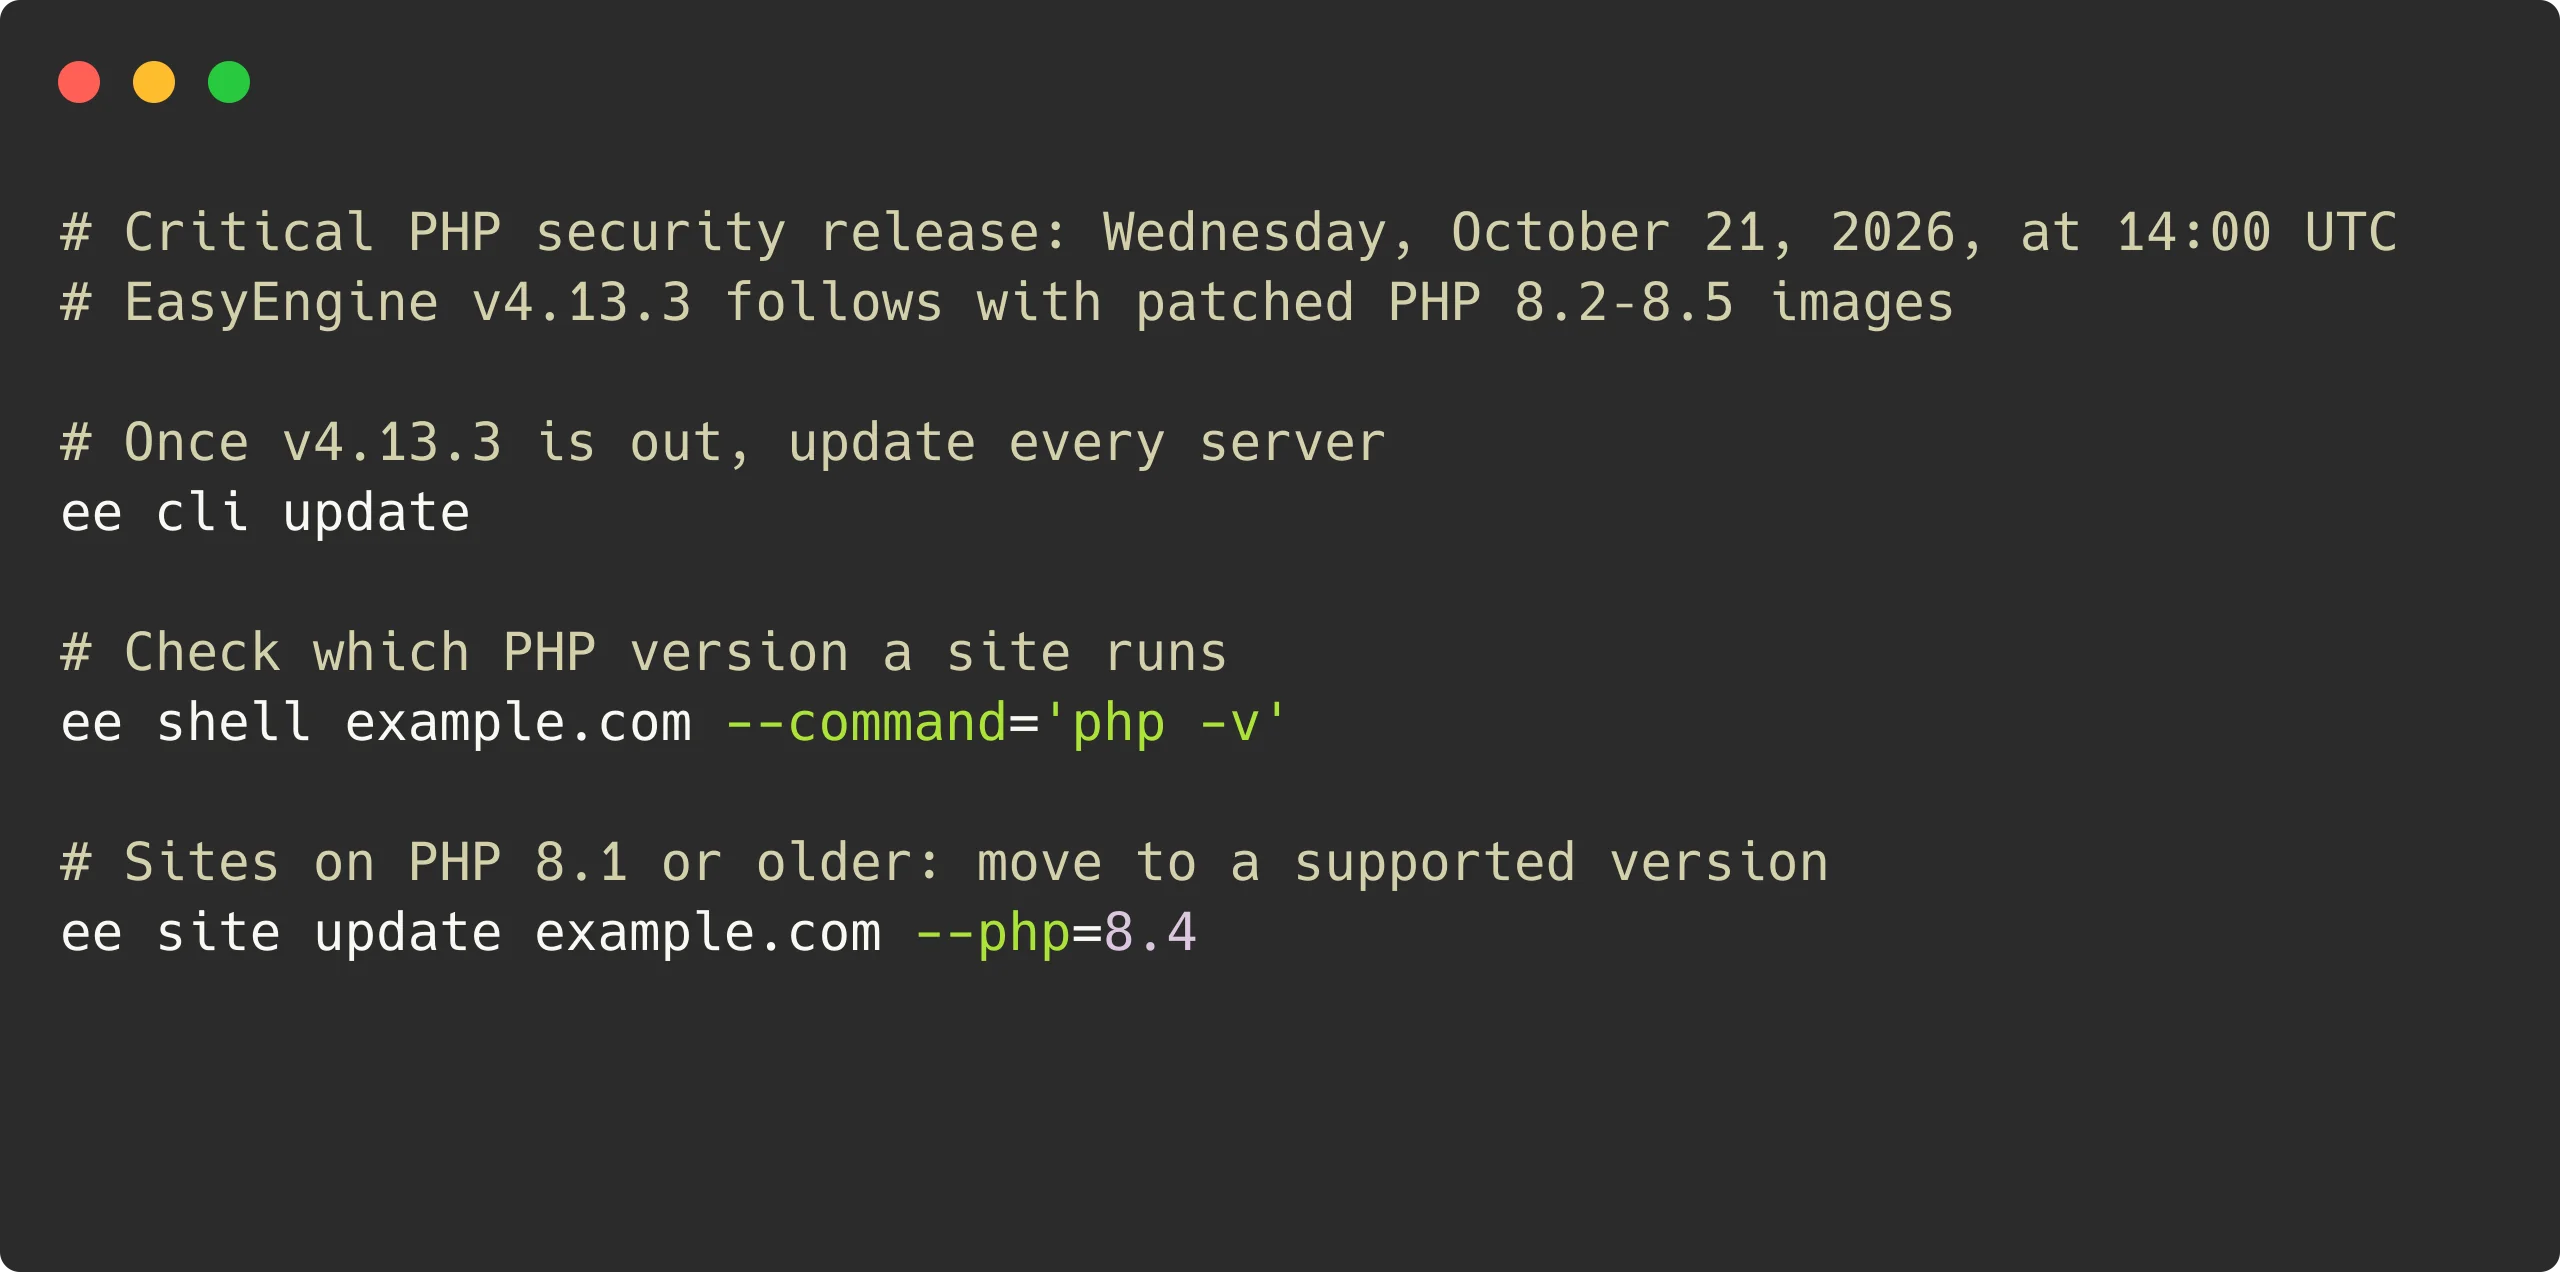
Critical PHP Security Release on October 21: EasyEngine’s Plan
PHP’s security release for two critical vulnerabilities is scheduled for October 21, 2026, at 14:00 UTC. We’re preparing EasyEngine v4.13.3 to deliver tested, patched images for PHP 8.2 through 8.5 once the official PHP Docker images are available. Here’s what to do now so you can update quickly.
-
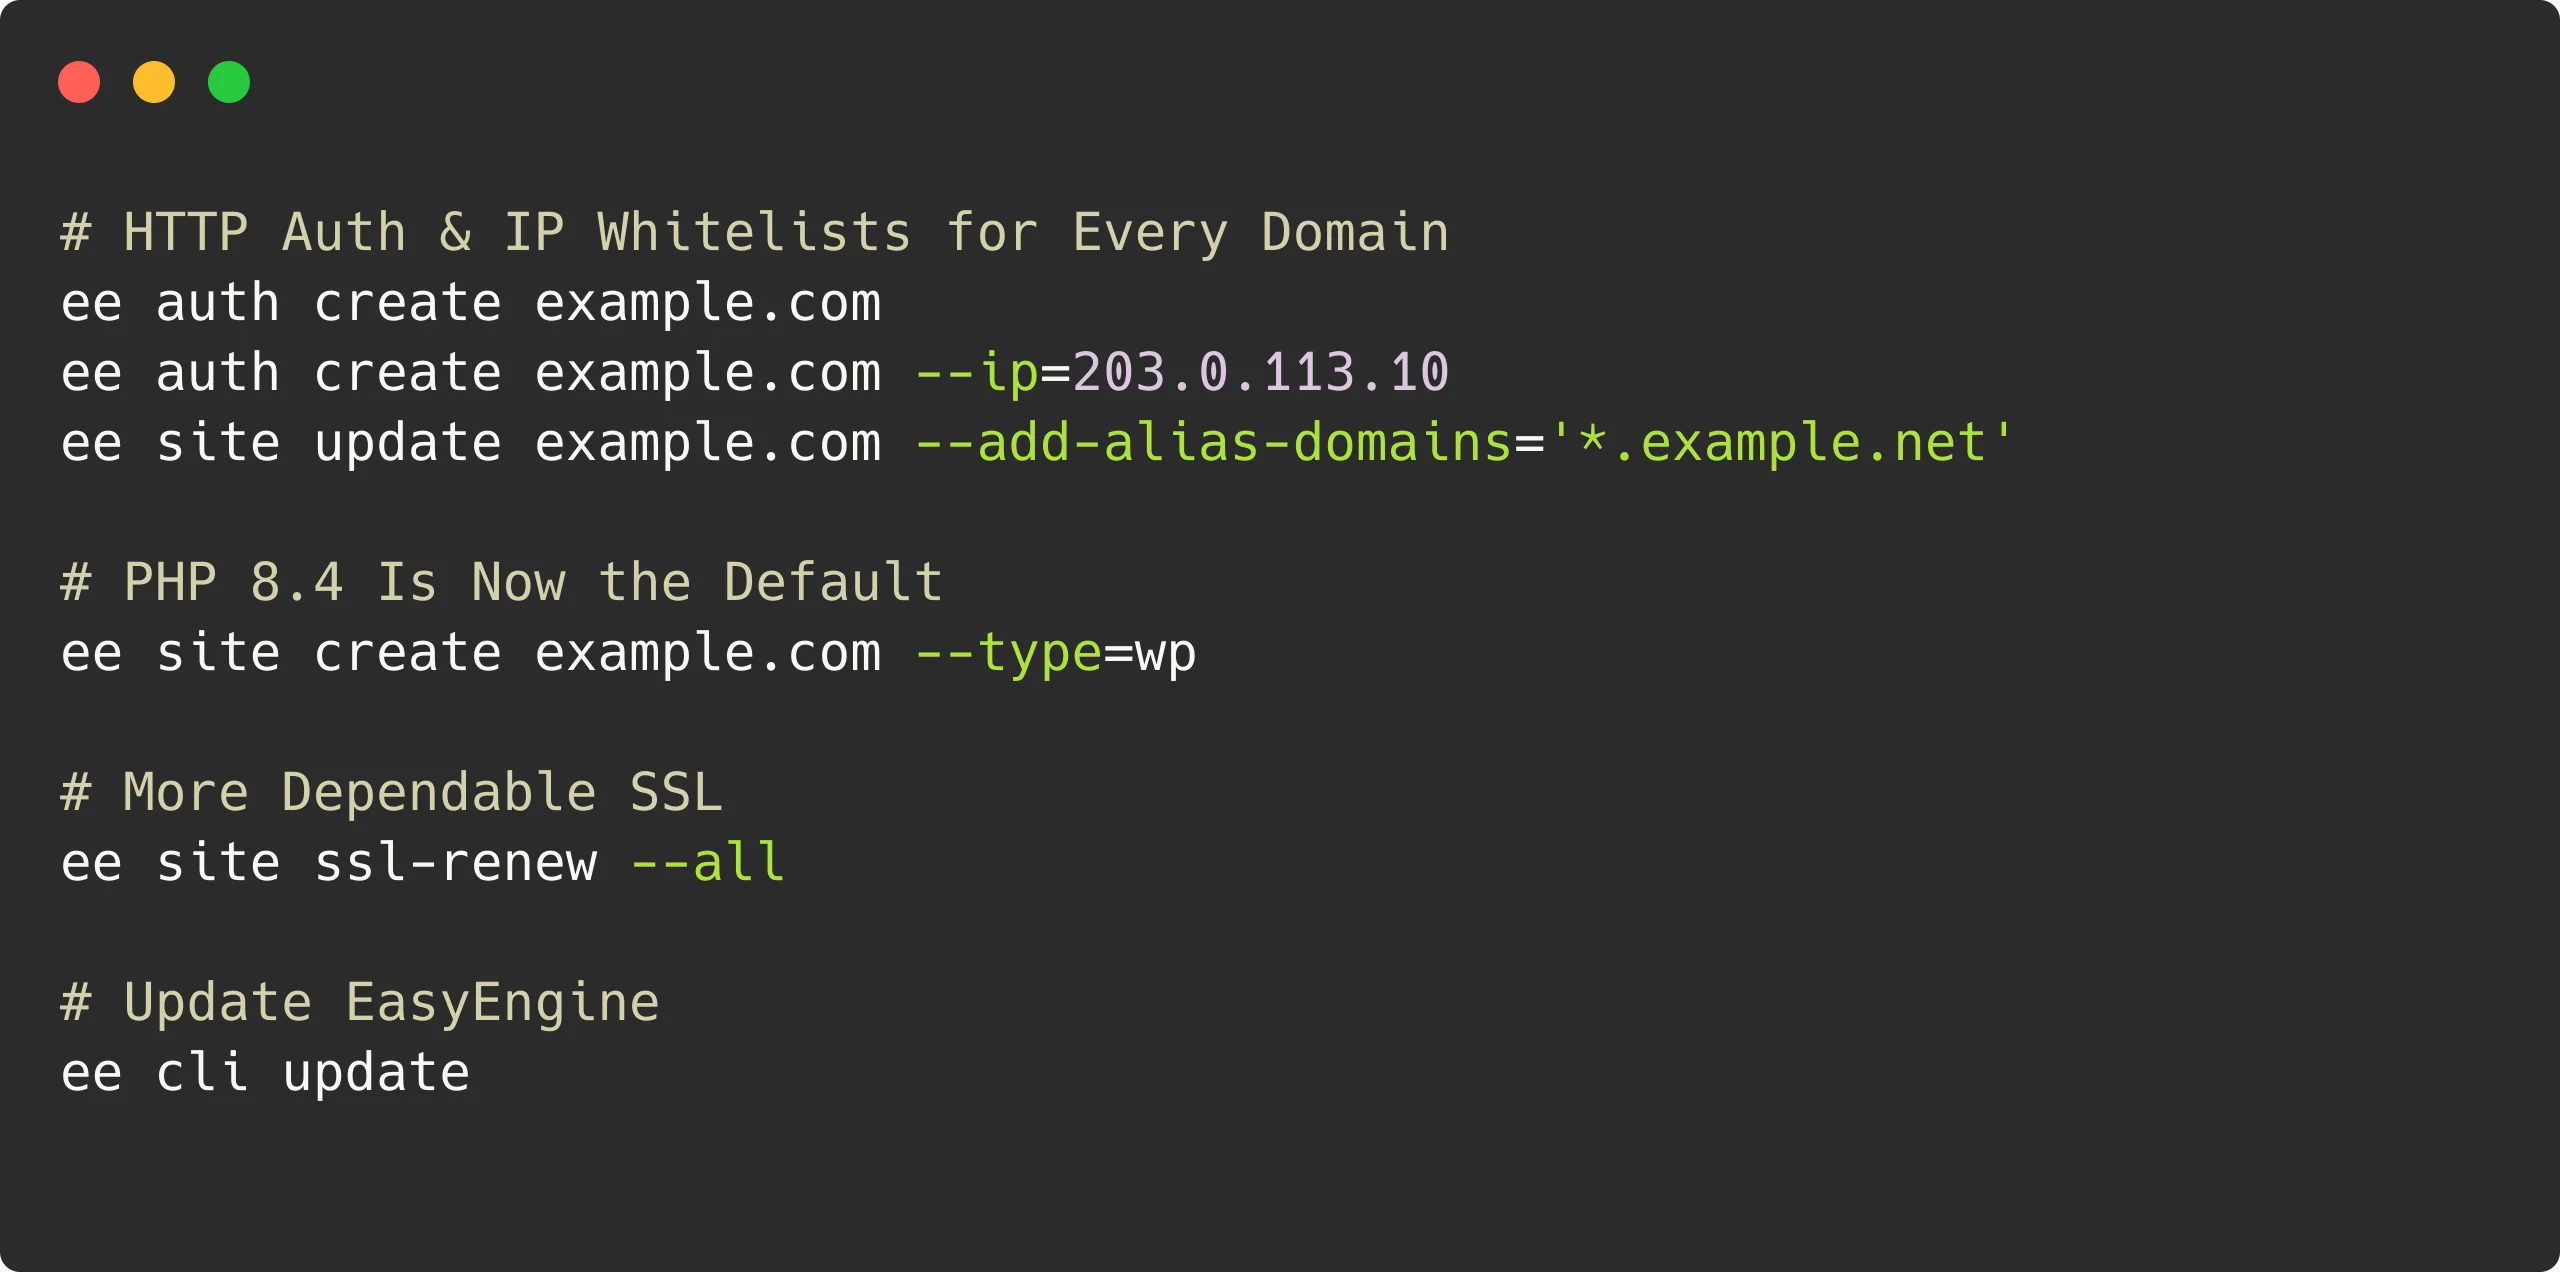
EasyEngine v4.10.2-v4.13.2 Released
Six EasyEngine releases, v4.10.2 through v4.13.2, bring stricter shell input handling, HTTP auth across a site’s domains, PHP 8.4 by default, and improvements to SSL, backups and updates.
-

EasyEngine v4.9.0-v4.10.1 Released
Hello there! 👋 We’re excited to announce a series of six releases for EasyEngine – versions 4.9.0 through 4.10.1. These releases, spanning from July to December 2025, bring some highly anticipated features and significant improvements to the platform. The highlight? Native backup and restore functionality, PHP 8.5 support, and improved integration with EasyEngine Dashboard. Let’s […]
-
 News
EasyEngine v4.7.1 Released
EasyEngine v4.7.1 is out, bringing crucial stack updates and minor patches. Highlights include updated HTTP/2 Nginx configuration, improved site service migrations, and added cron configuration updates. Bugfixes address issues with Docker Compose updates affecting cron jobs. Update now for enhanced performance!