
Expert insights
Unlock a wealth of knowledge with our comprehensive resources library, featuring insightful guides, e-books, checklists and white papers
-
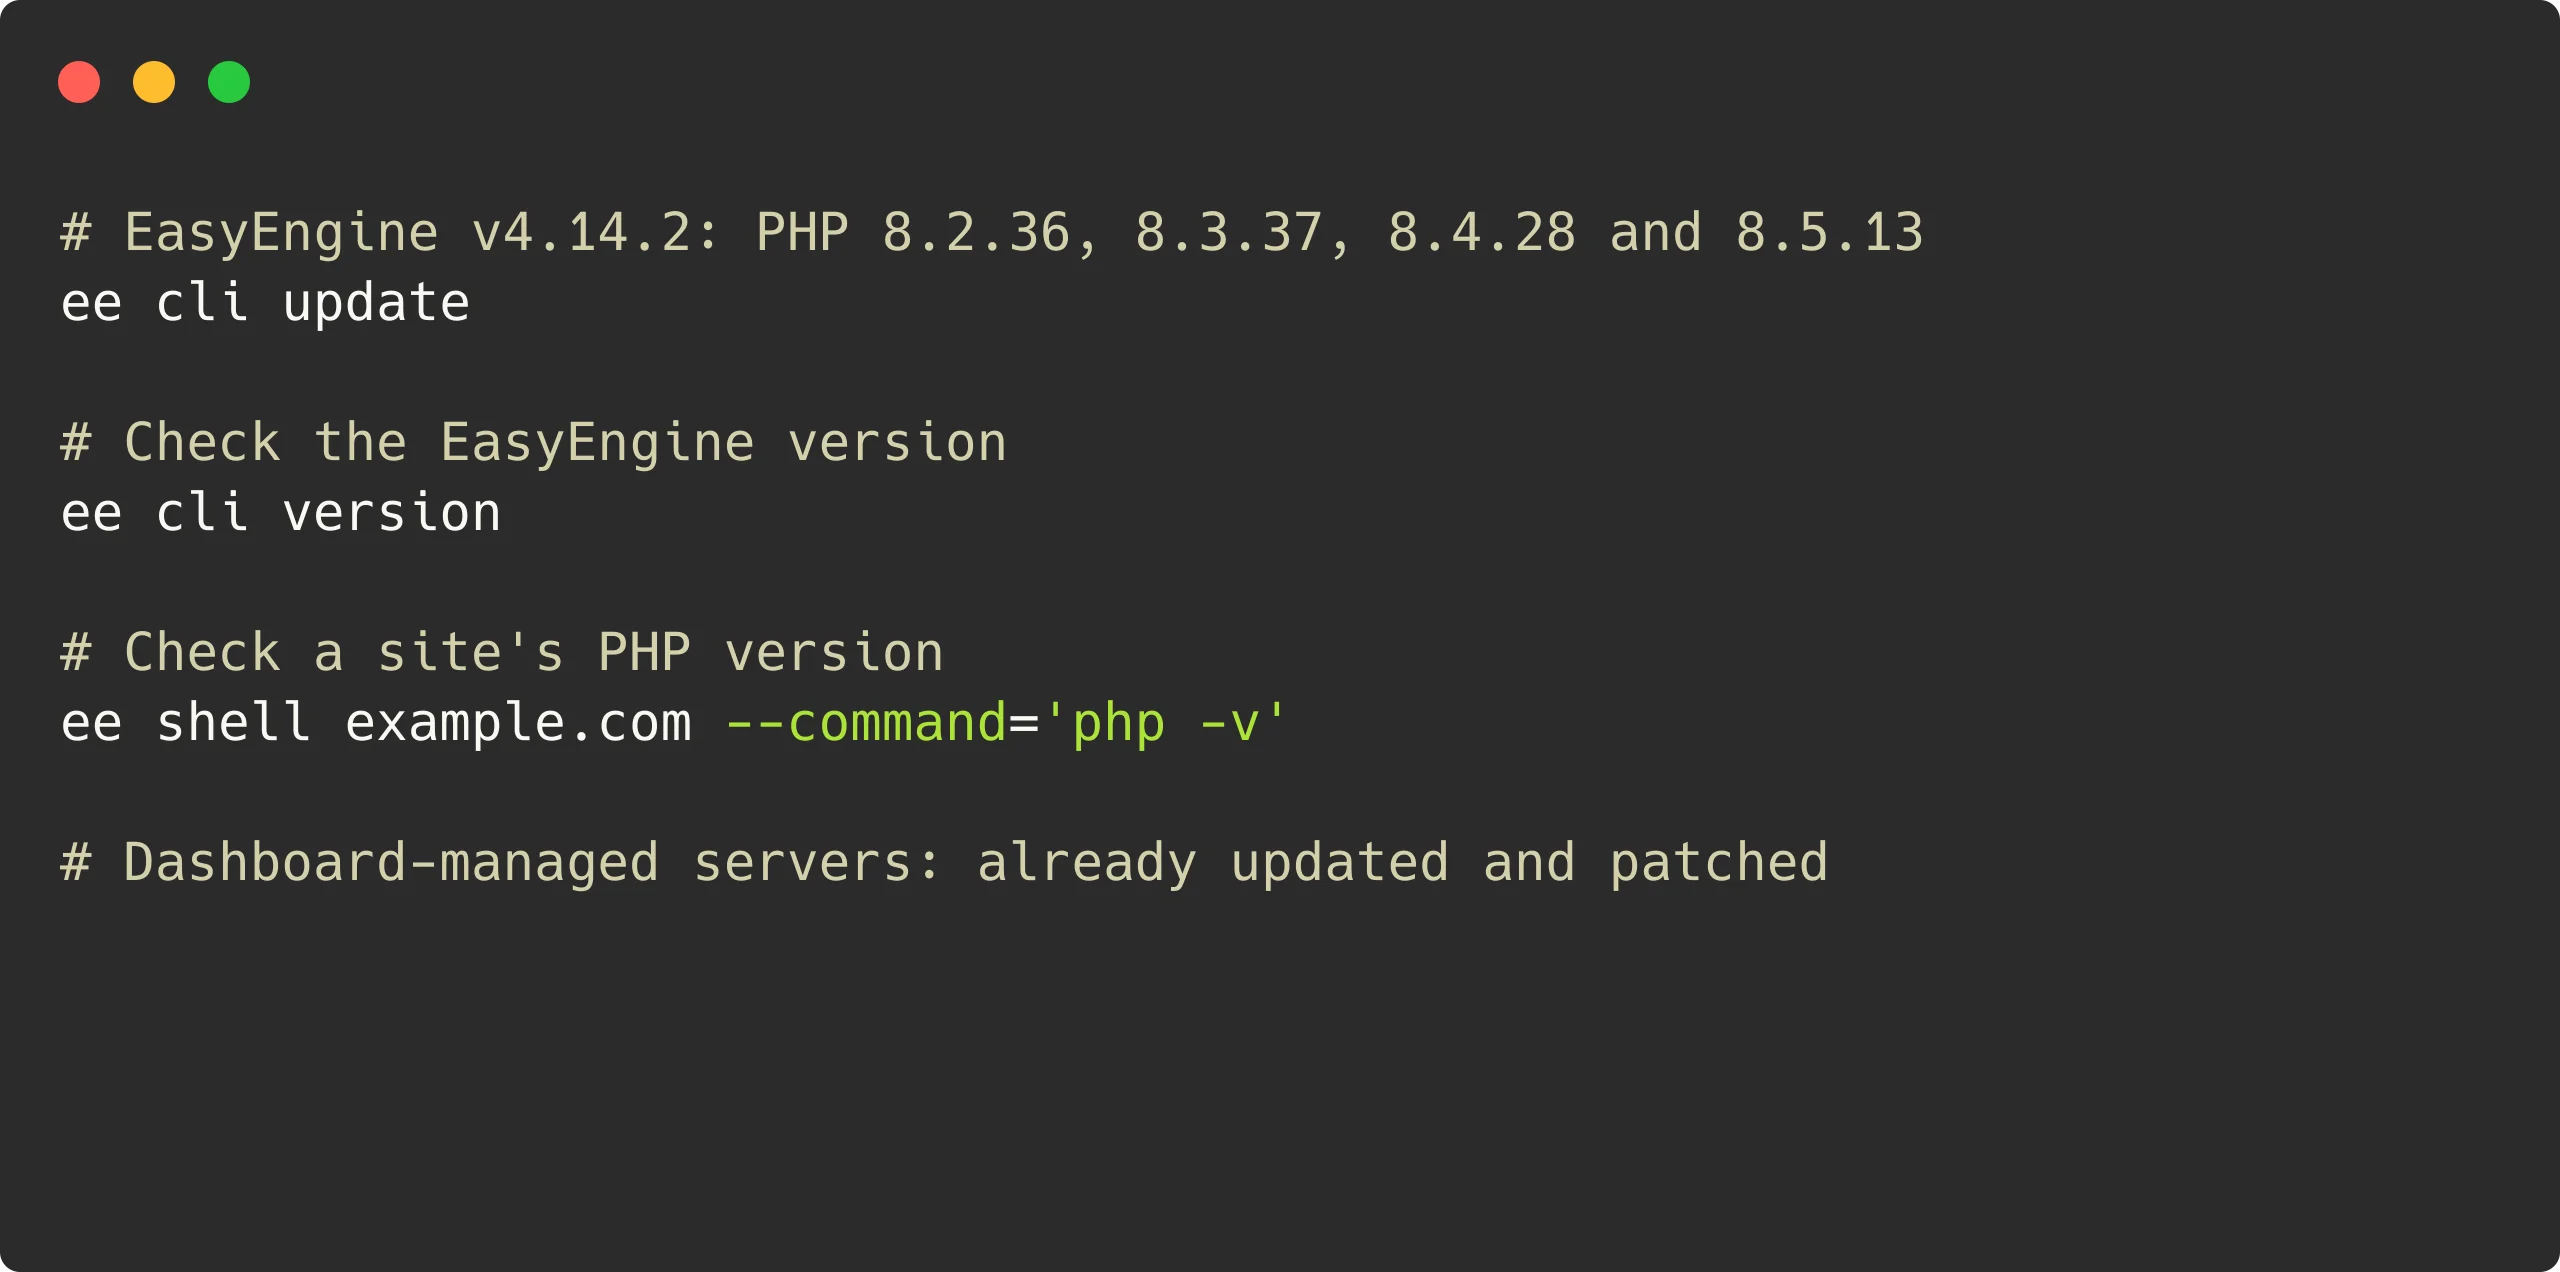
EasyEngine v4.14.2 Delivers November’s PHP Security Fixes
EasyEngine v4.14.2 delivers PHP’s security fixes for PHP 8.2 to 8.5, moving enabled sites to PHP 8.2.36, 8.3.37, 8.4.28 and 8.5.13. PHP released fixes for 17 security advisories, 7 of them rated critical. On CLI-managed servers, run ee cli update. Dashboard-managed servers are already updated and patched. There’s nothing for you to do unless you have sites on PHP 8.1 or older.
-
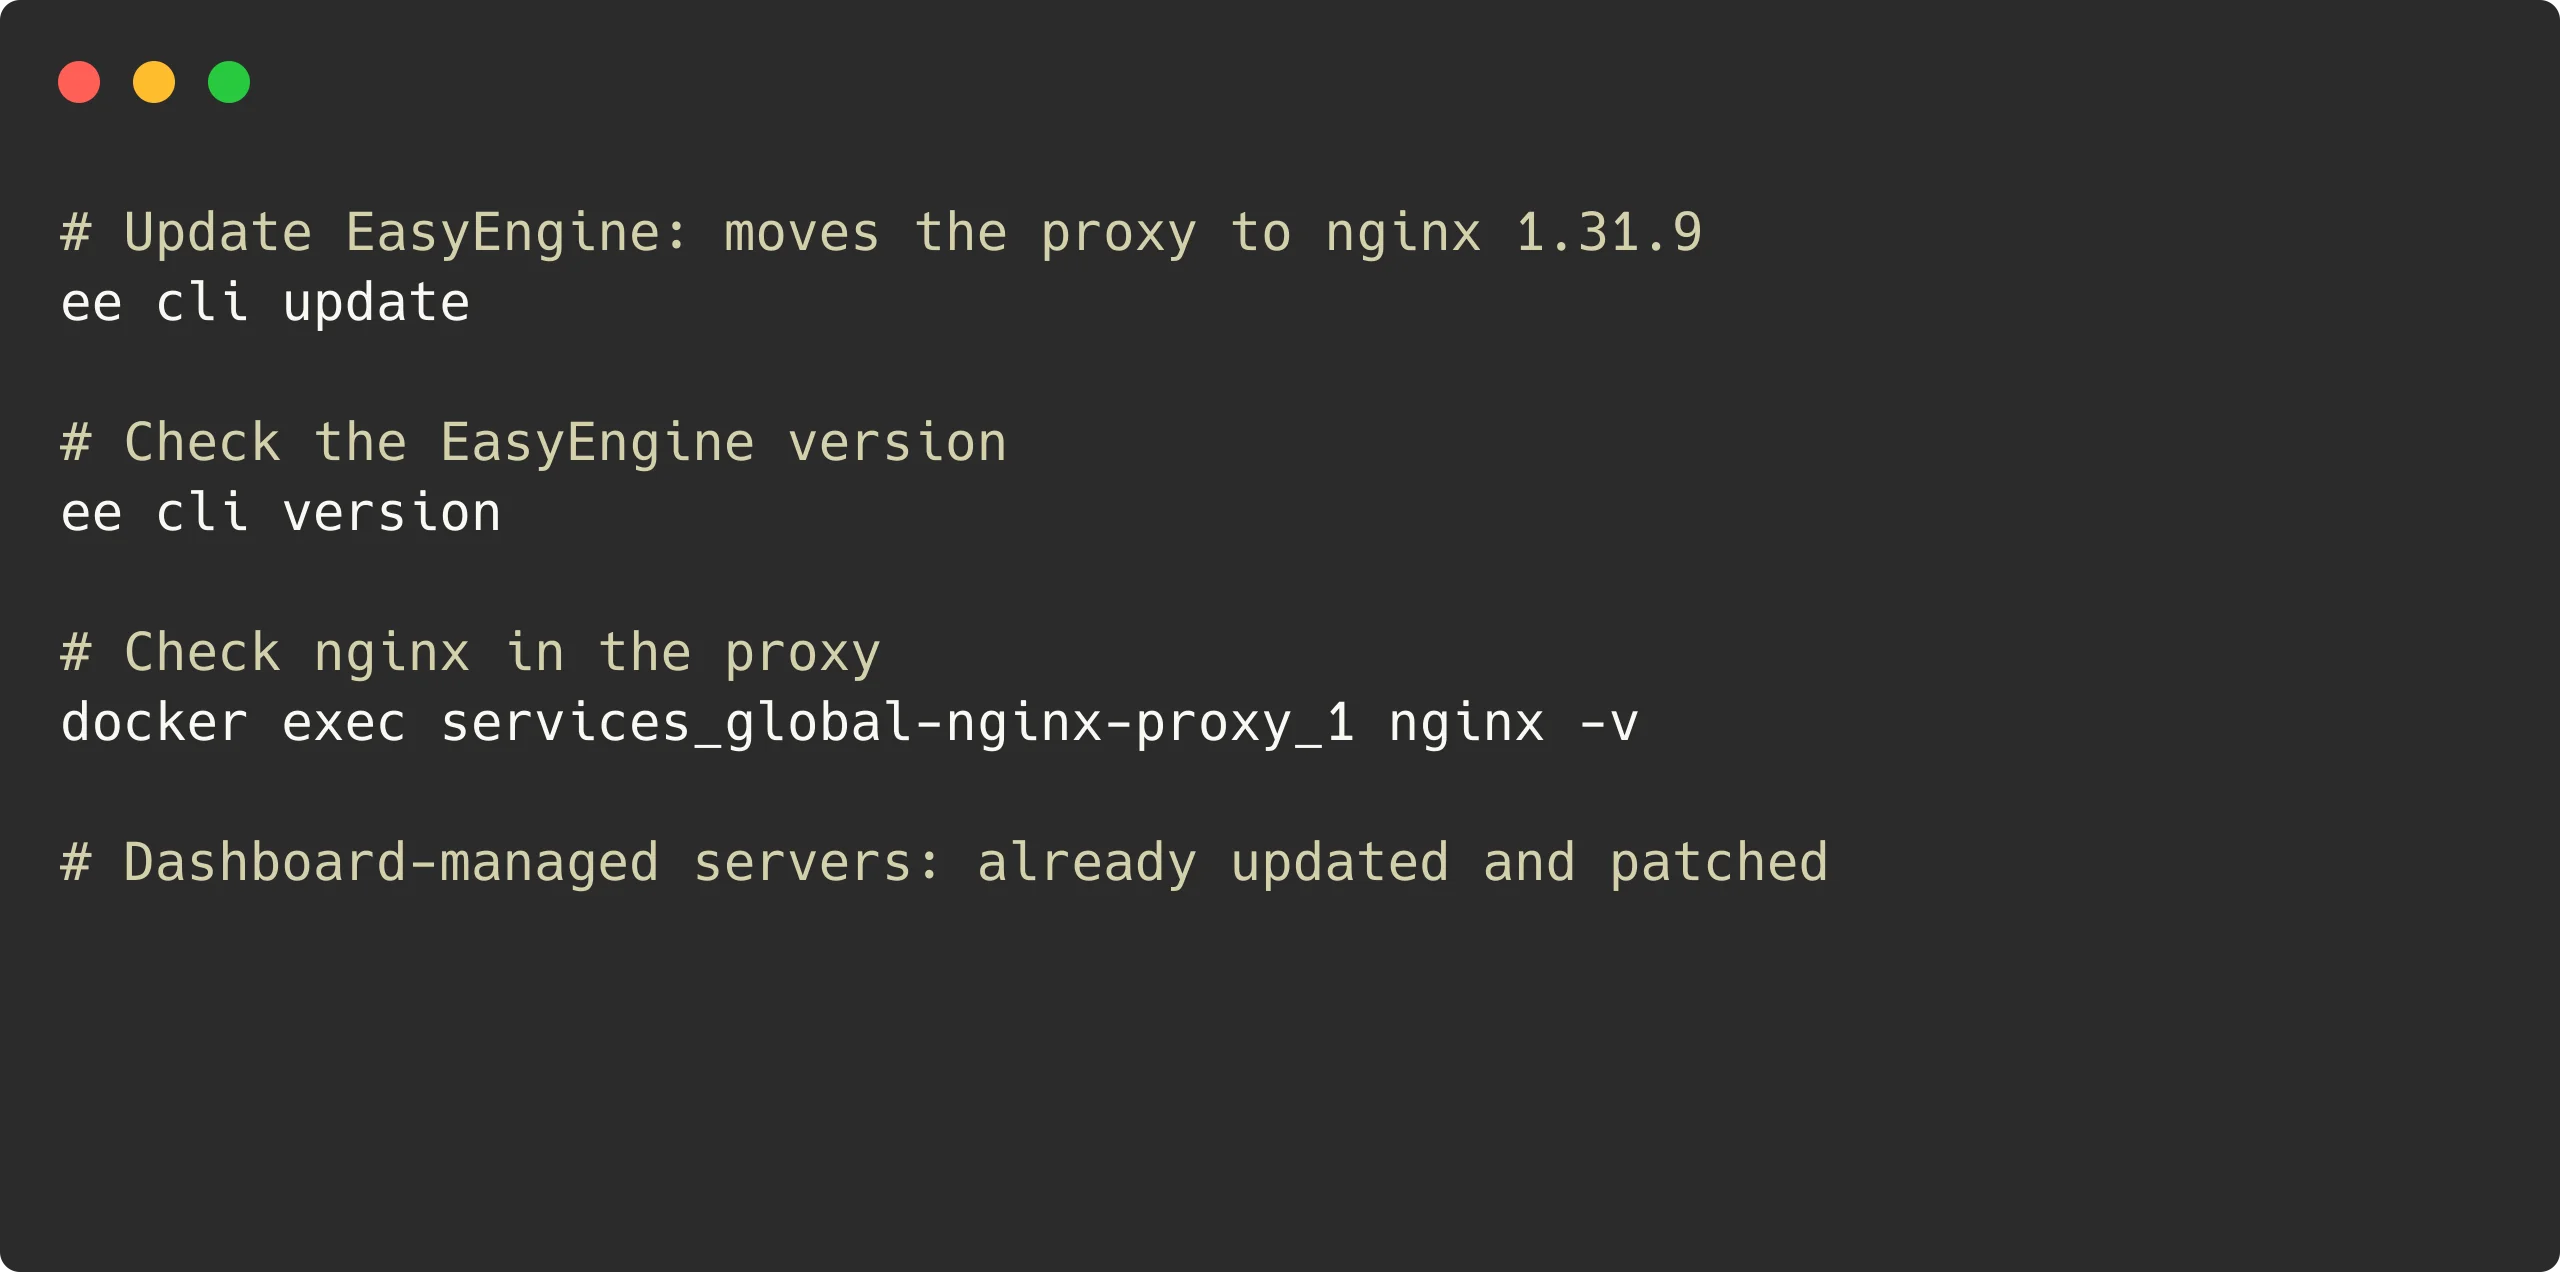
EasyEngine v4.14.1 Fixes nginx HTTP/2 Vulnerabilities
EasyEngine v4.14.1 fixes two HTTP/2 vulnerabilities in nginx, in the proxy that all traffic to your sites passes through. Servers on EasyEngine v4.14.0 or earlier are affected. On CLI-managed servers, run ee cli update. Dashboard-managed servers are already updated and patched, so there’s nothing for you to do.
-
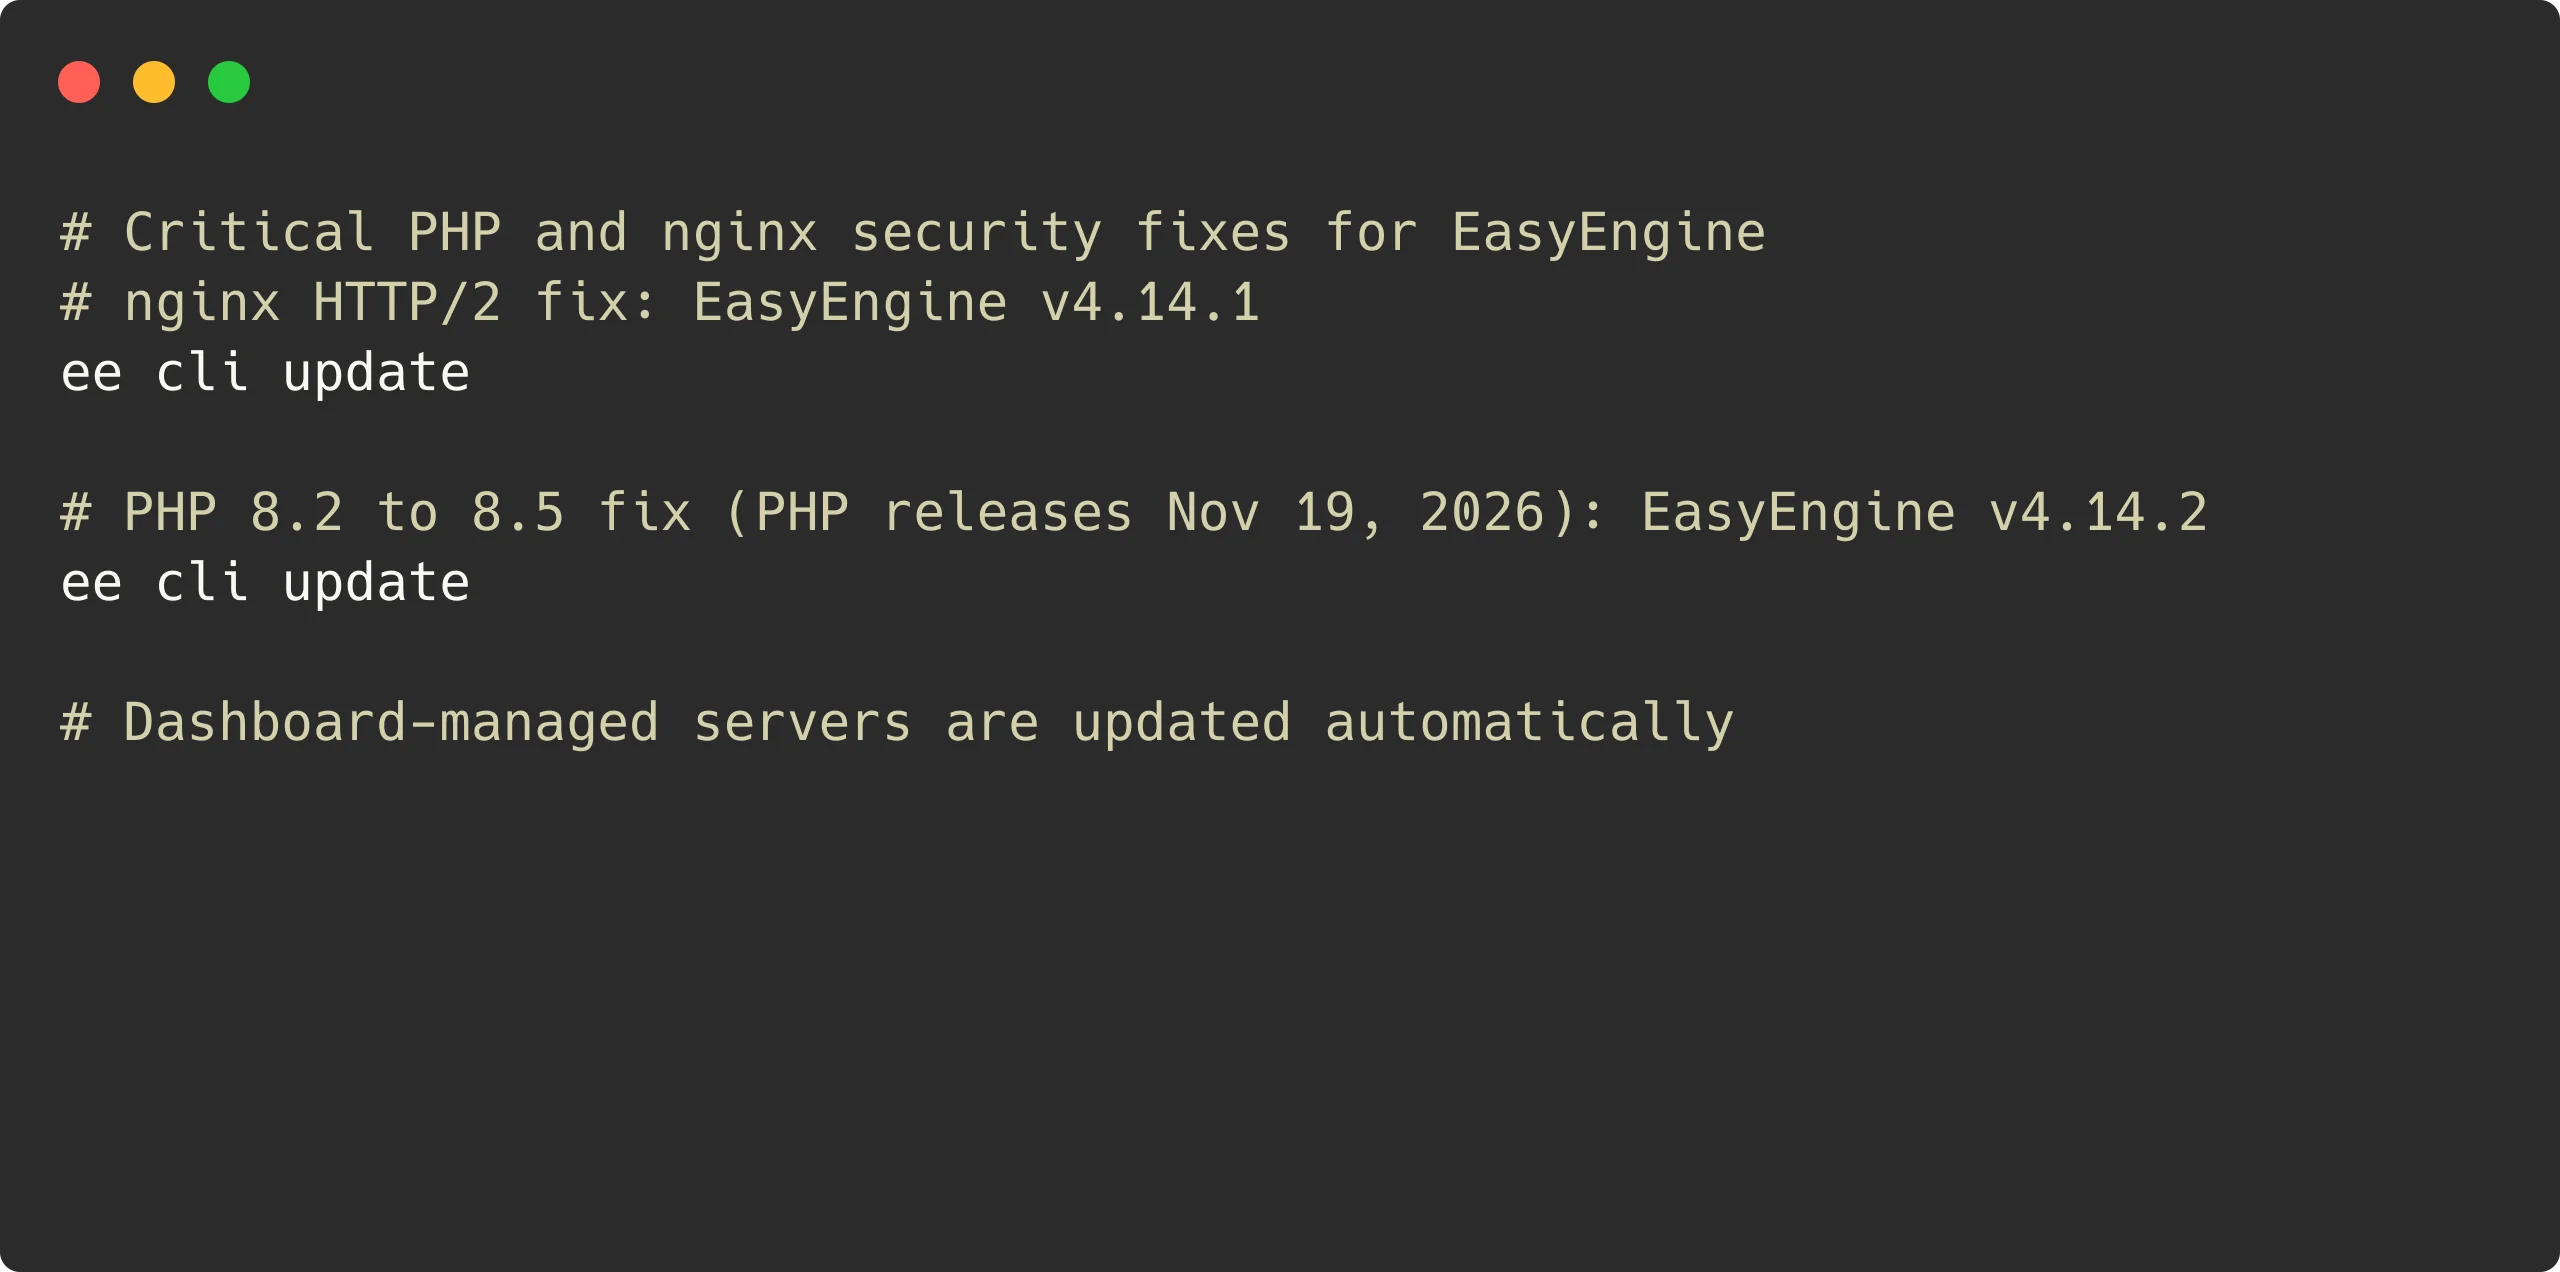
Critical PHP and nginx Security Fixes: EasyEngine’s Release Plan
EasyEngine v4.14.2 is out with PHP’s security fixes for PHP 8.2 to 8.5, and EasyEngine v4.14.1 with nginx’s fixes for two HTTP/2 vulnerabilities in the proxy that serves every HTTPS site. On CLI-managed servers, run ee cli update. Dashboard-managed servers are already updated to v4.14.2.
-
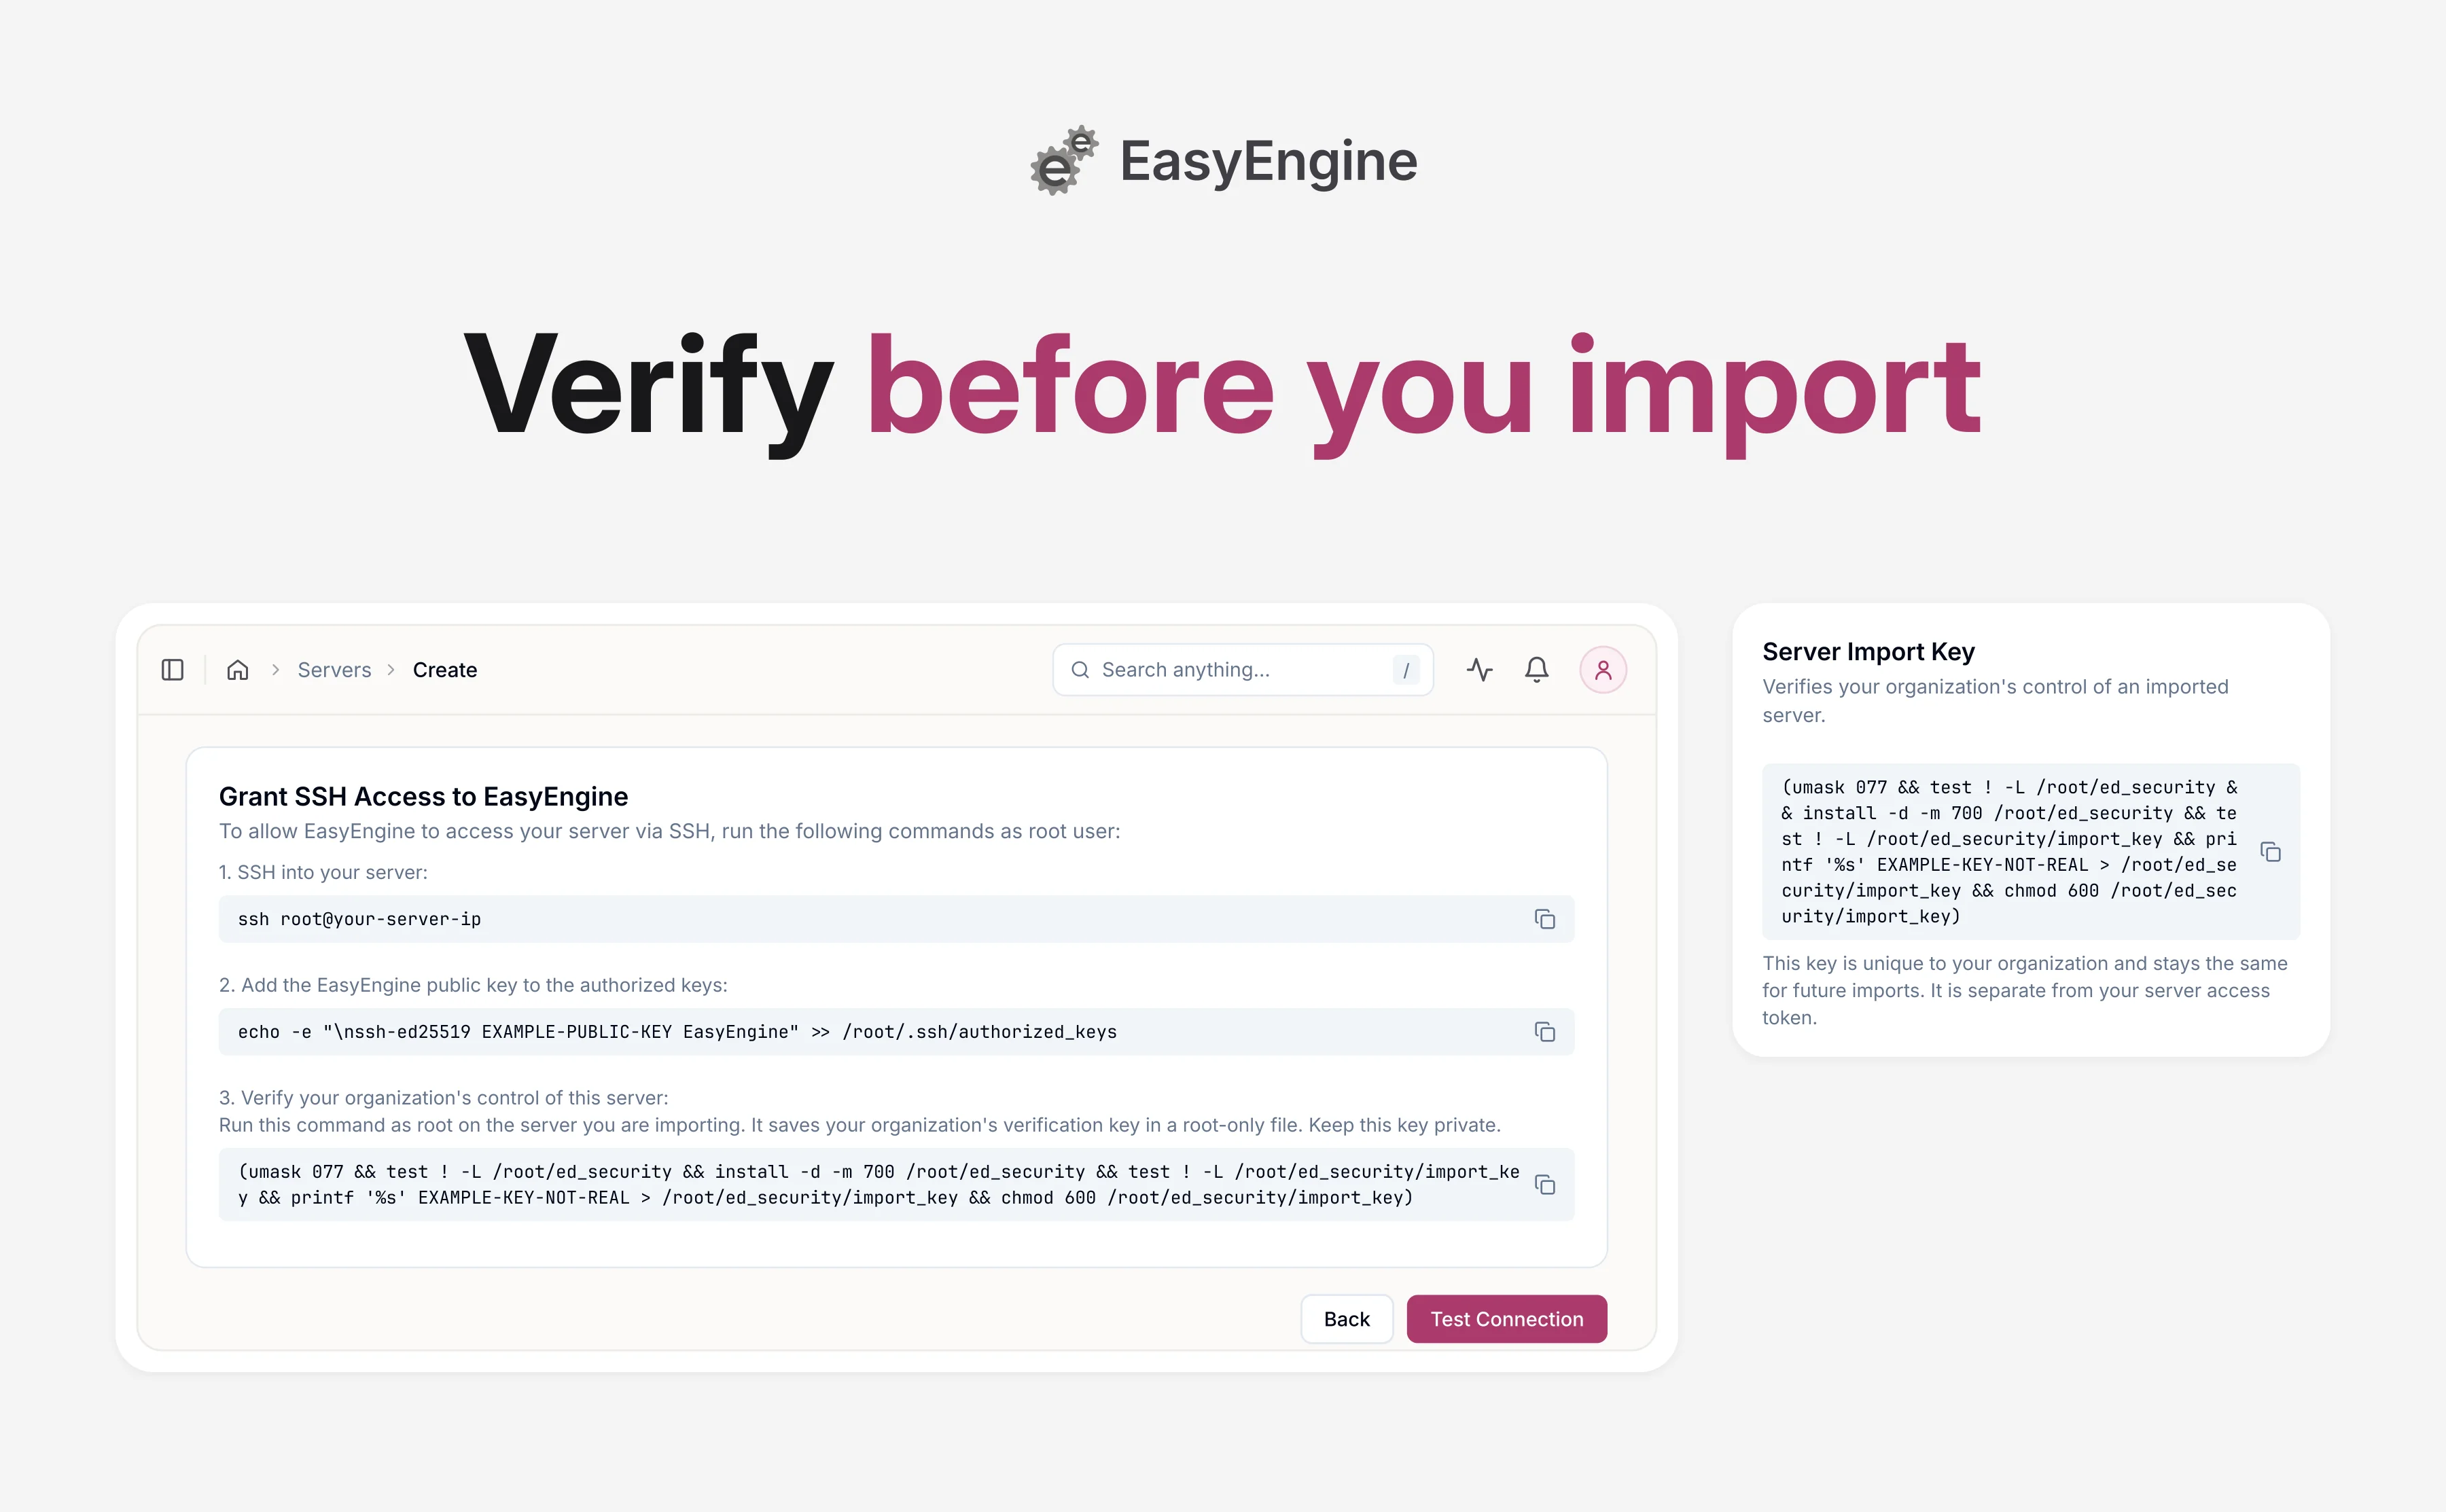
EasyEngine Dashboard security update: verified server imports, safer sign-ups
EasyEngine Dashboard now adds a server you import to your organization only after it finds your organization’s key in a root-only file, which only someone with root on that server can write. Email sign-ups start clean when you verify your email, and 26 security fixes ship in all.
-
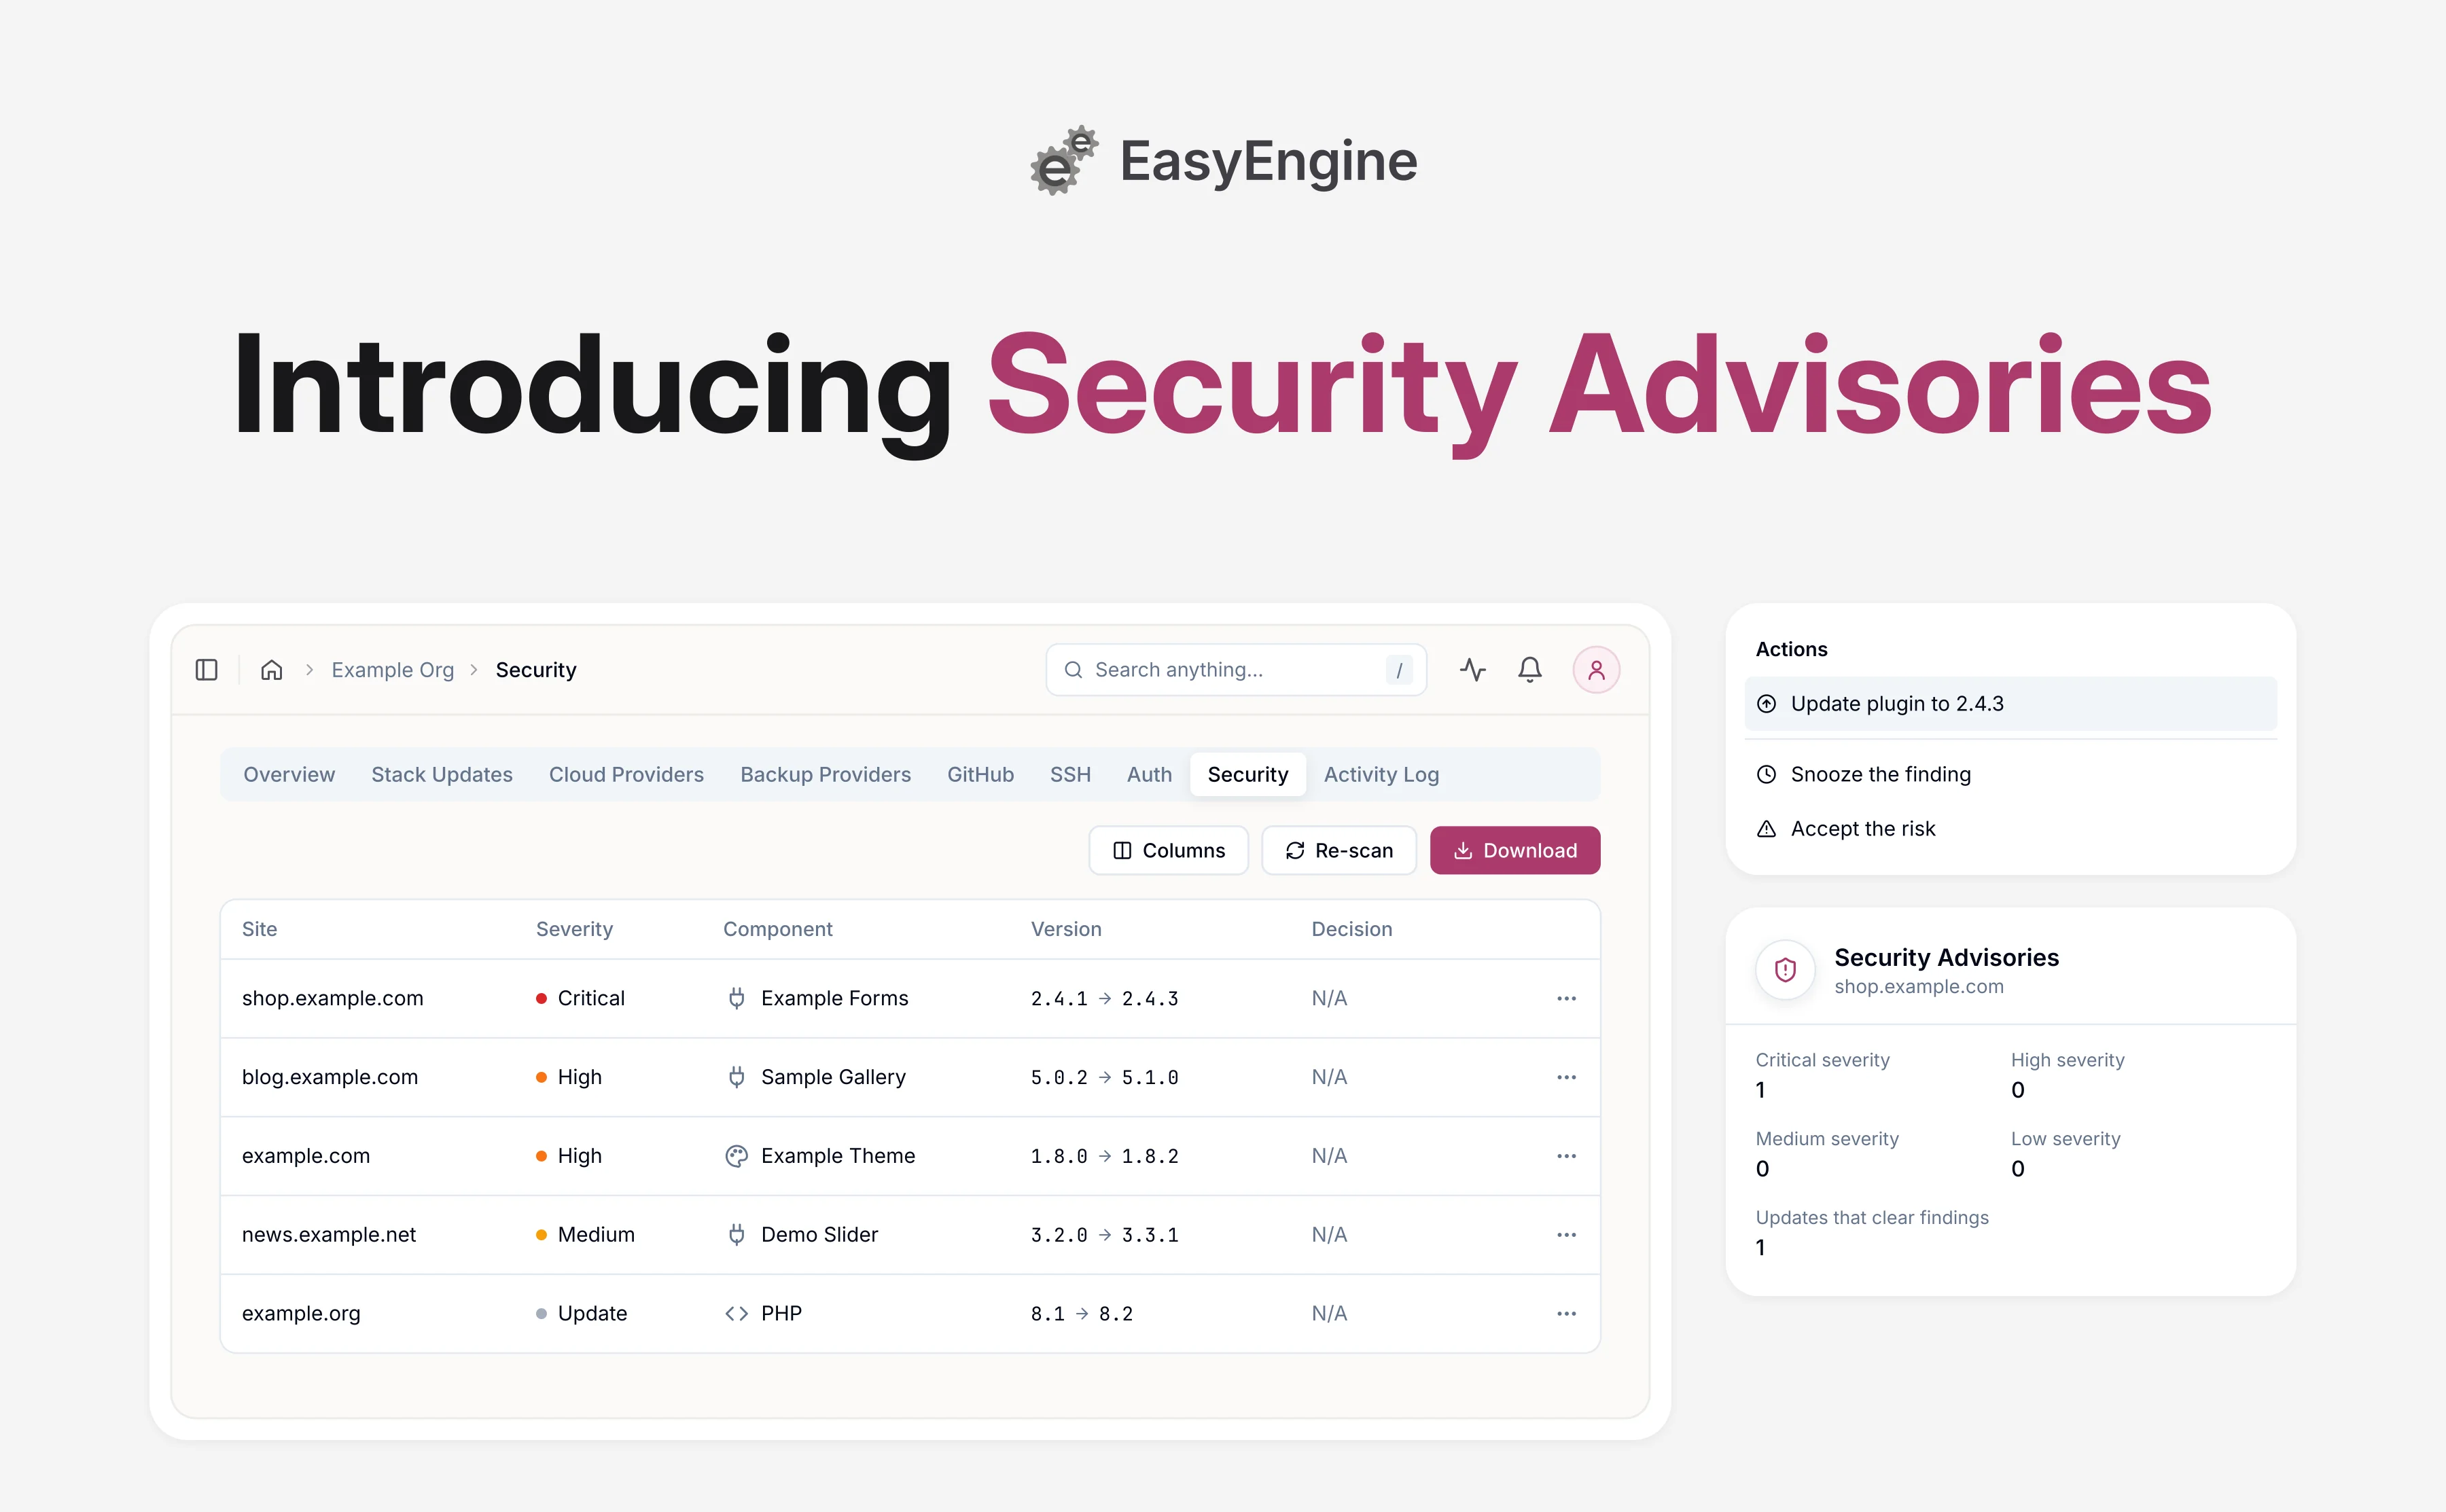
EasyEngine Dashboard now flags vulnerable plugins, themes and WordPress core
Security Advisories in EasyEngine Dashboard checks the plugins, themes and WordPress core on eligible live WordPress sites on your EasyEngine servers against published security advisories, shows which sites need attention, and lets you update the affected plugin or theme from the same screen.
-
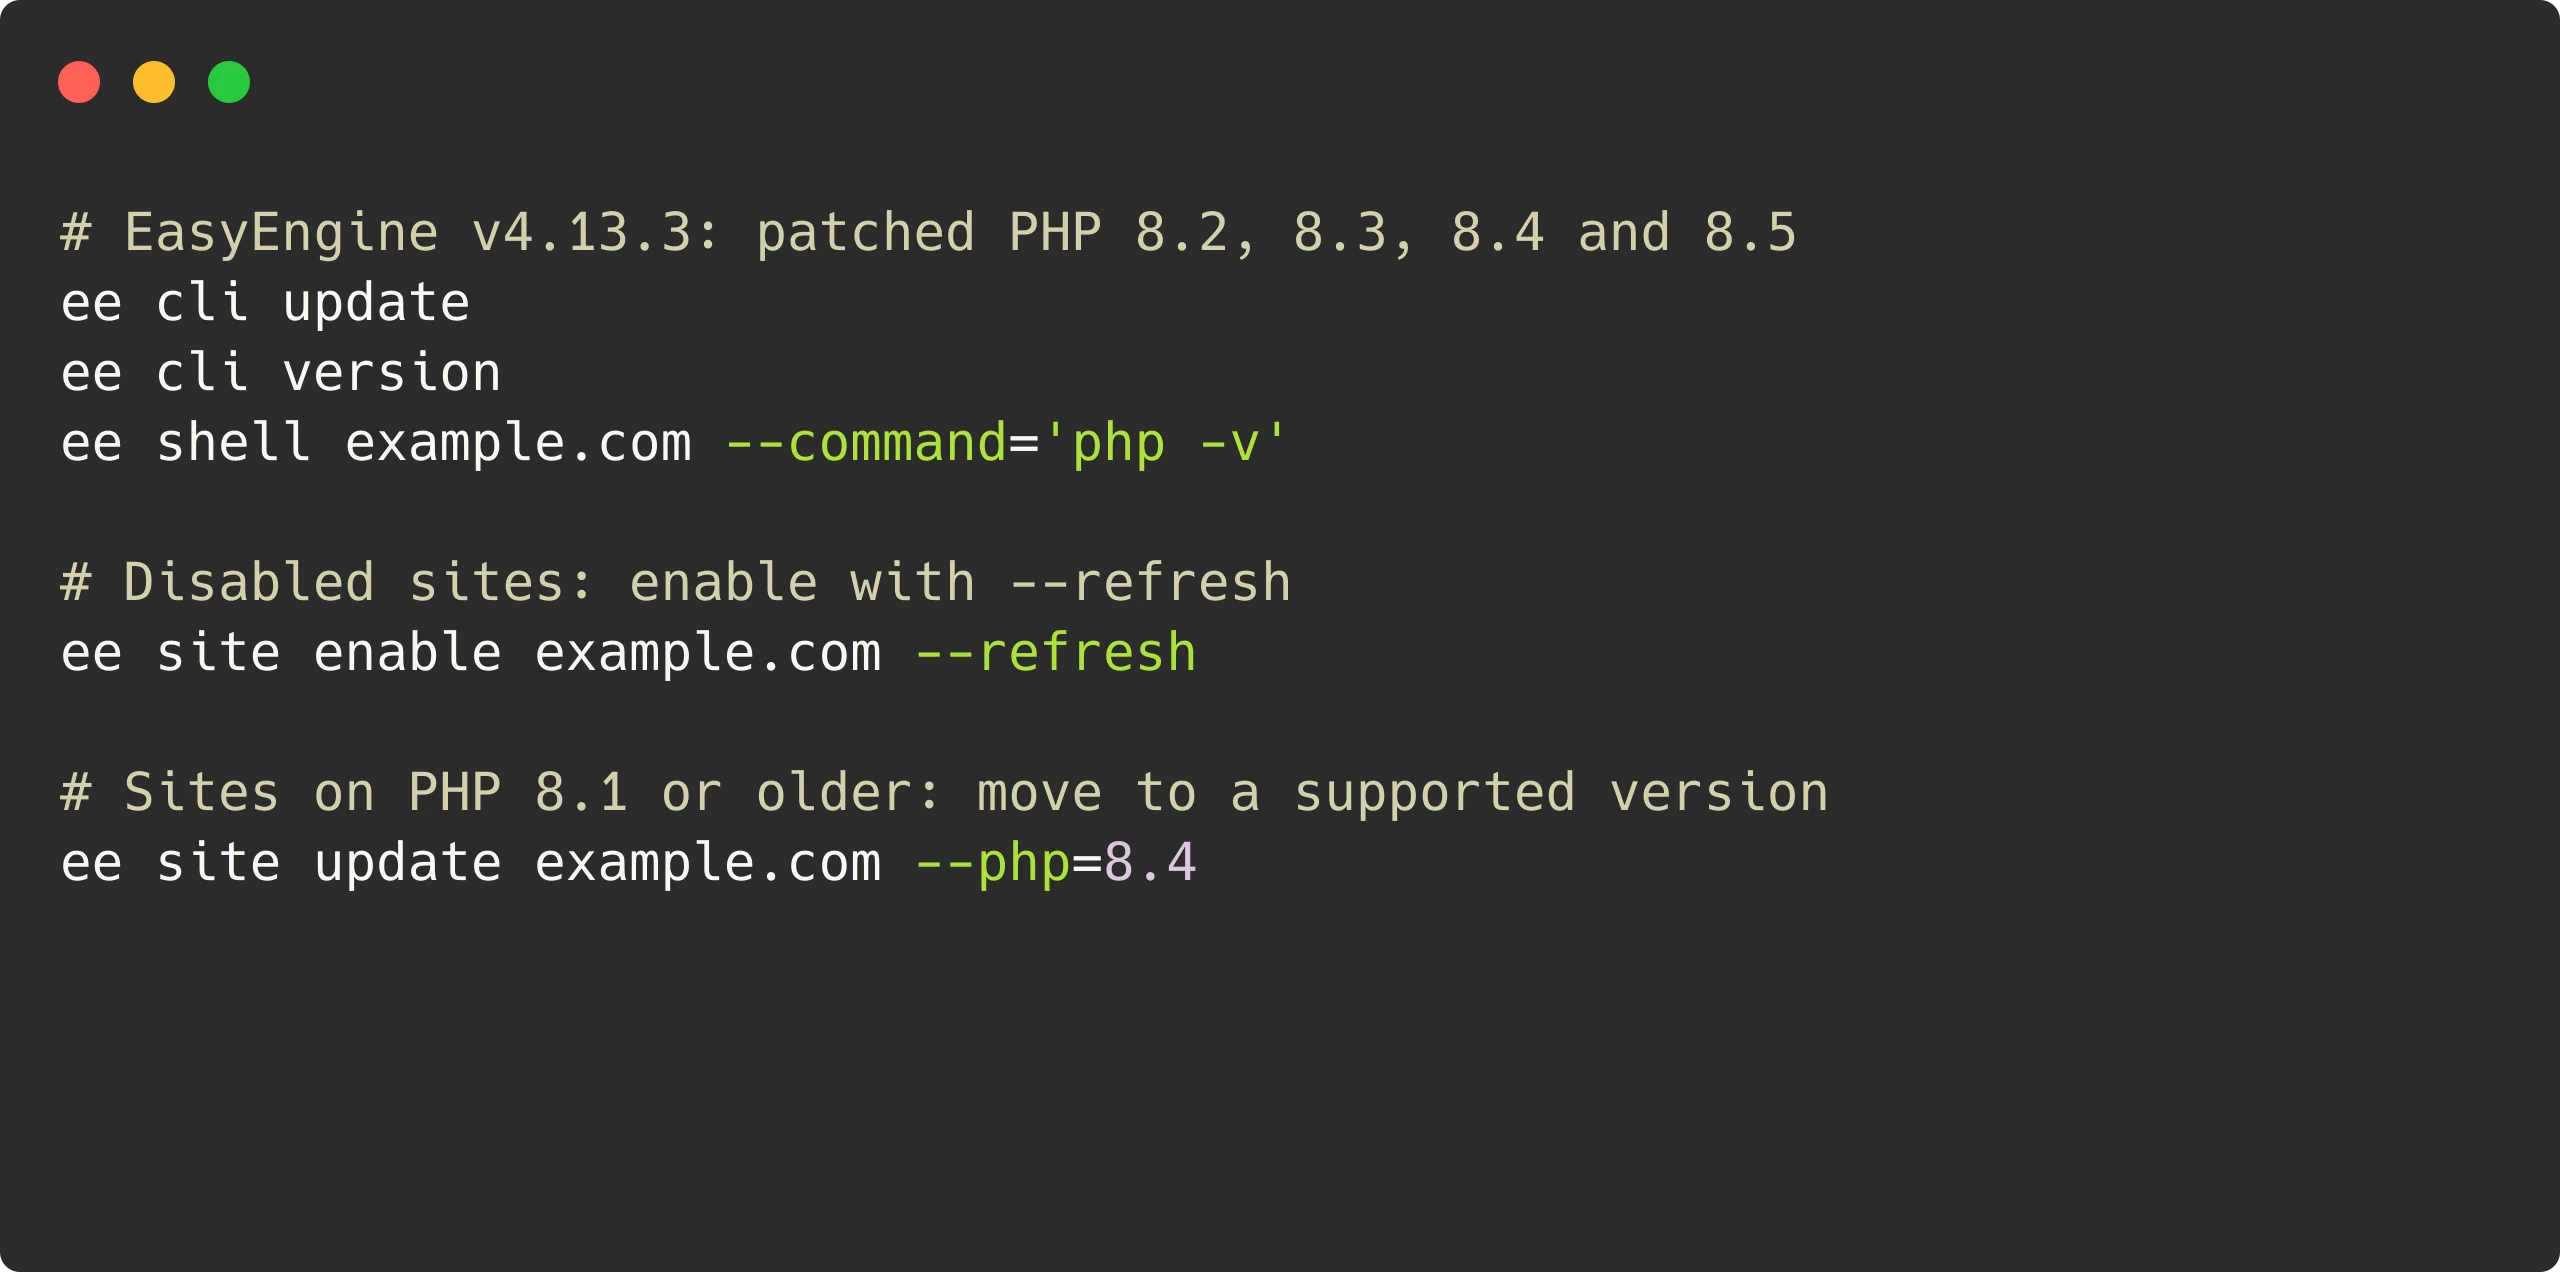
EasyEngine v4.13.3 Fixes Critical PHP Vulnerabilities
EasyEngine v4.13.3 moves enabled sites on PHP 8.2 through 8.5 to patched images for two critical PHP vulnerabilities, and turns off session upload progress on WordPress and PHP sites on Linux. On CLI-managed servers, run ee cli update. Dashboard-managed servers update automatically.
-
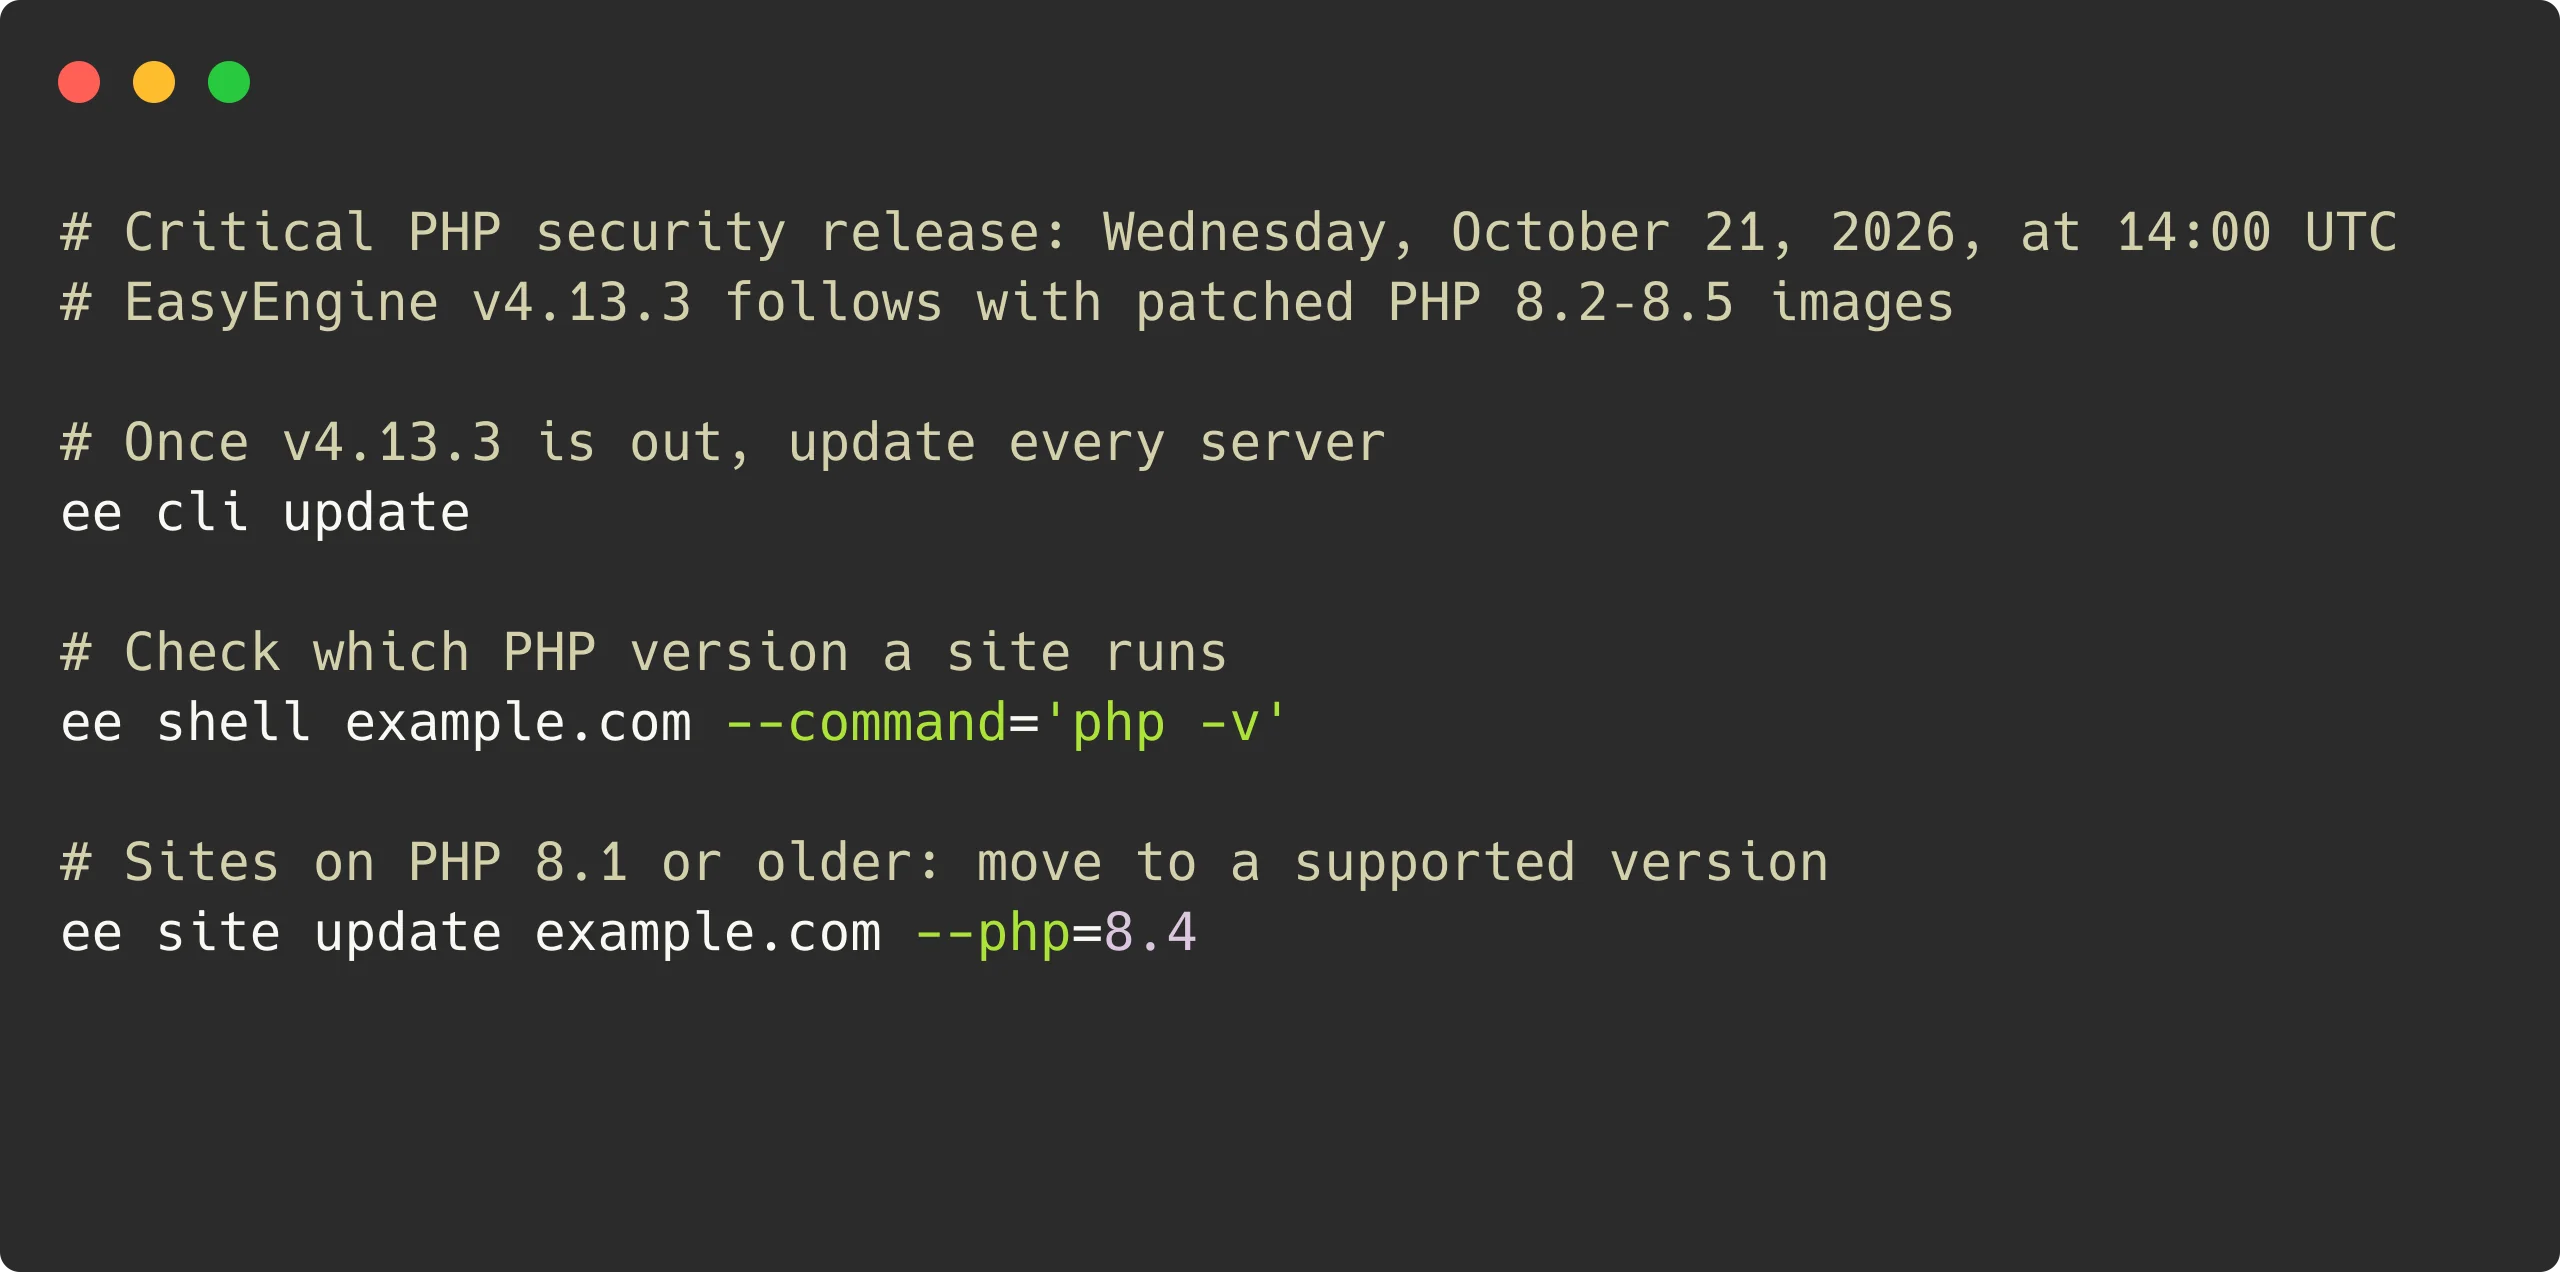
Critical PHP Security Release on October 21: EasyEngine’s Plan
PHP’s security release for two critical vulnerabilities is scheduled for October 21, 2026, at 14:00 UTC. We’re preparing EasyEngine v4.13.3 to deliver tested, patched images for PHP 8.2 through 8.5 once the official PHP Docker images are available. Here’s what to do now so you can update quickly.
-
 News
How EasyEngine Dashboard handled Copy Fail before you noticed
Copy Fail is a CVSS 7.8 Linux kernel CVE affecting every distribution shipped since 2017. EasyEngine Dashboard had the mitigation running on every managed server within hours, before most customers even saw the advisory.
-
 News
A few words on Dirty Cow
We have been receiving a lot of questions and concerns from EasyEngine users about Dirty Cow, which is why we thought it best to write this post. Below is tweet showing concern raised by Vikram. What is Dirty Cow Dirty Cow is a Linux kernel vulnerability that can be exploited to elevate an unauthorized user’s […]
-
 News
Security Vulnerability in MariaDB 10.1
Recently a vulnerability was discovered in MariaDB referred to as MySQL Remote Root Code Execution / Privilege Escalation 0day with CVE code CVE-2016-6662.
-
 Release
HTTPoxy CGI Vulnerabilities Fix
EasyEngine security update to fix httpoxy – a set of vulnerabilities that affects PHP/CGI applications that rely on HTTP_PROXY header
-
 News
EasyEngine 3.5.6 Fixes ImageMagick Remote Code Execution Vulnerability
EasyEngine security update to fix recent ImageMagick vulnerability discovered by slack team at https://imagetragick.com/